Skip to the main content.
Watch Demo Meet With Our Team

Randy Lindberg

Randy Lindberg is the founder and CEO of Rivial Data Security. He has more than twenty years of experience in information security and started Rivial to fix the issues he saw as an Information Systems Security Officer in the U.S. Air Force and Information Security Manager at a $4 billion dollar financial institution.

4 min read

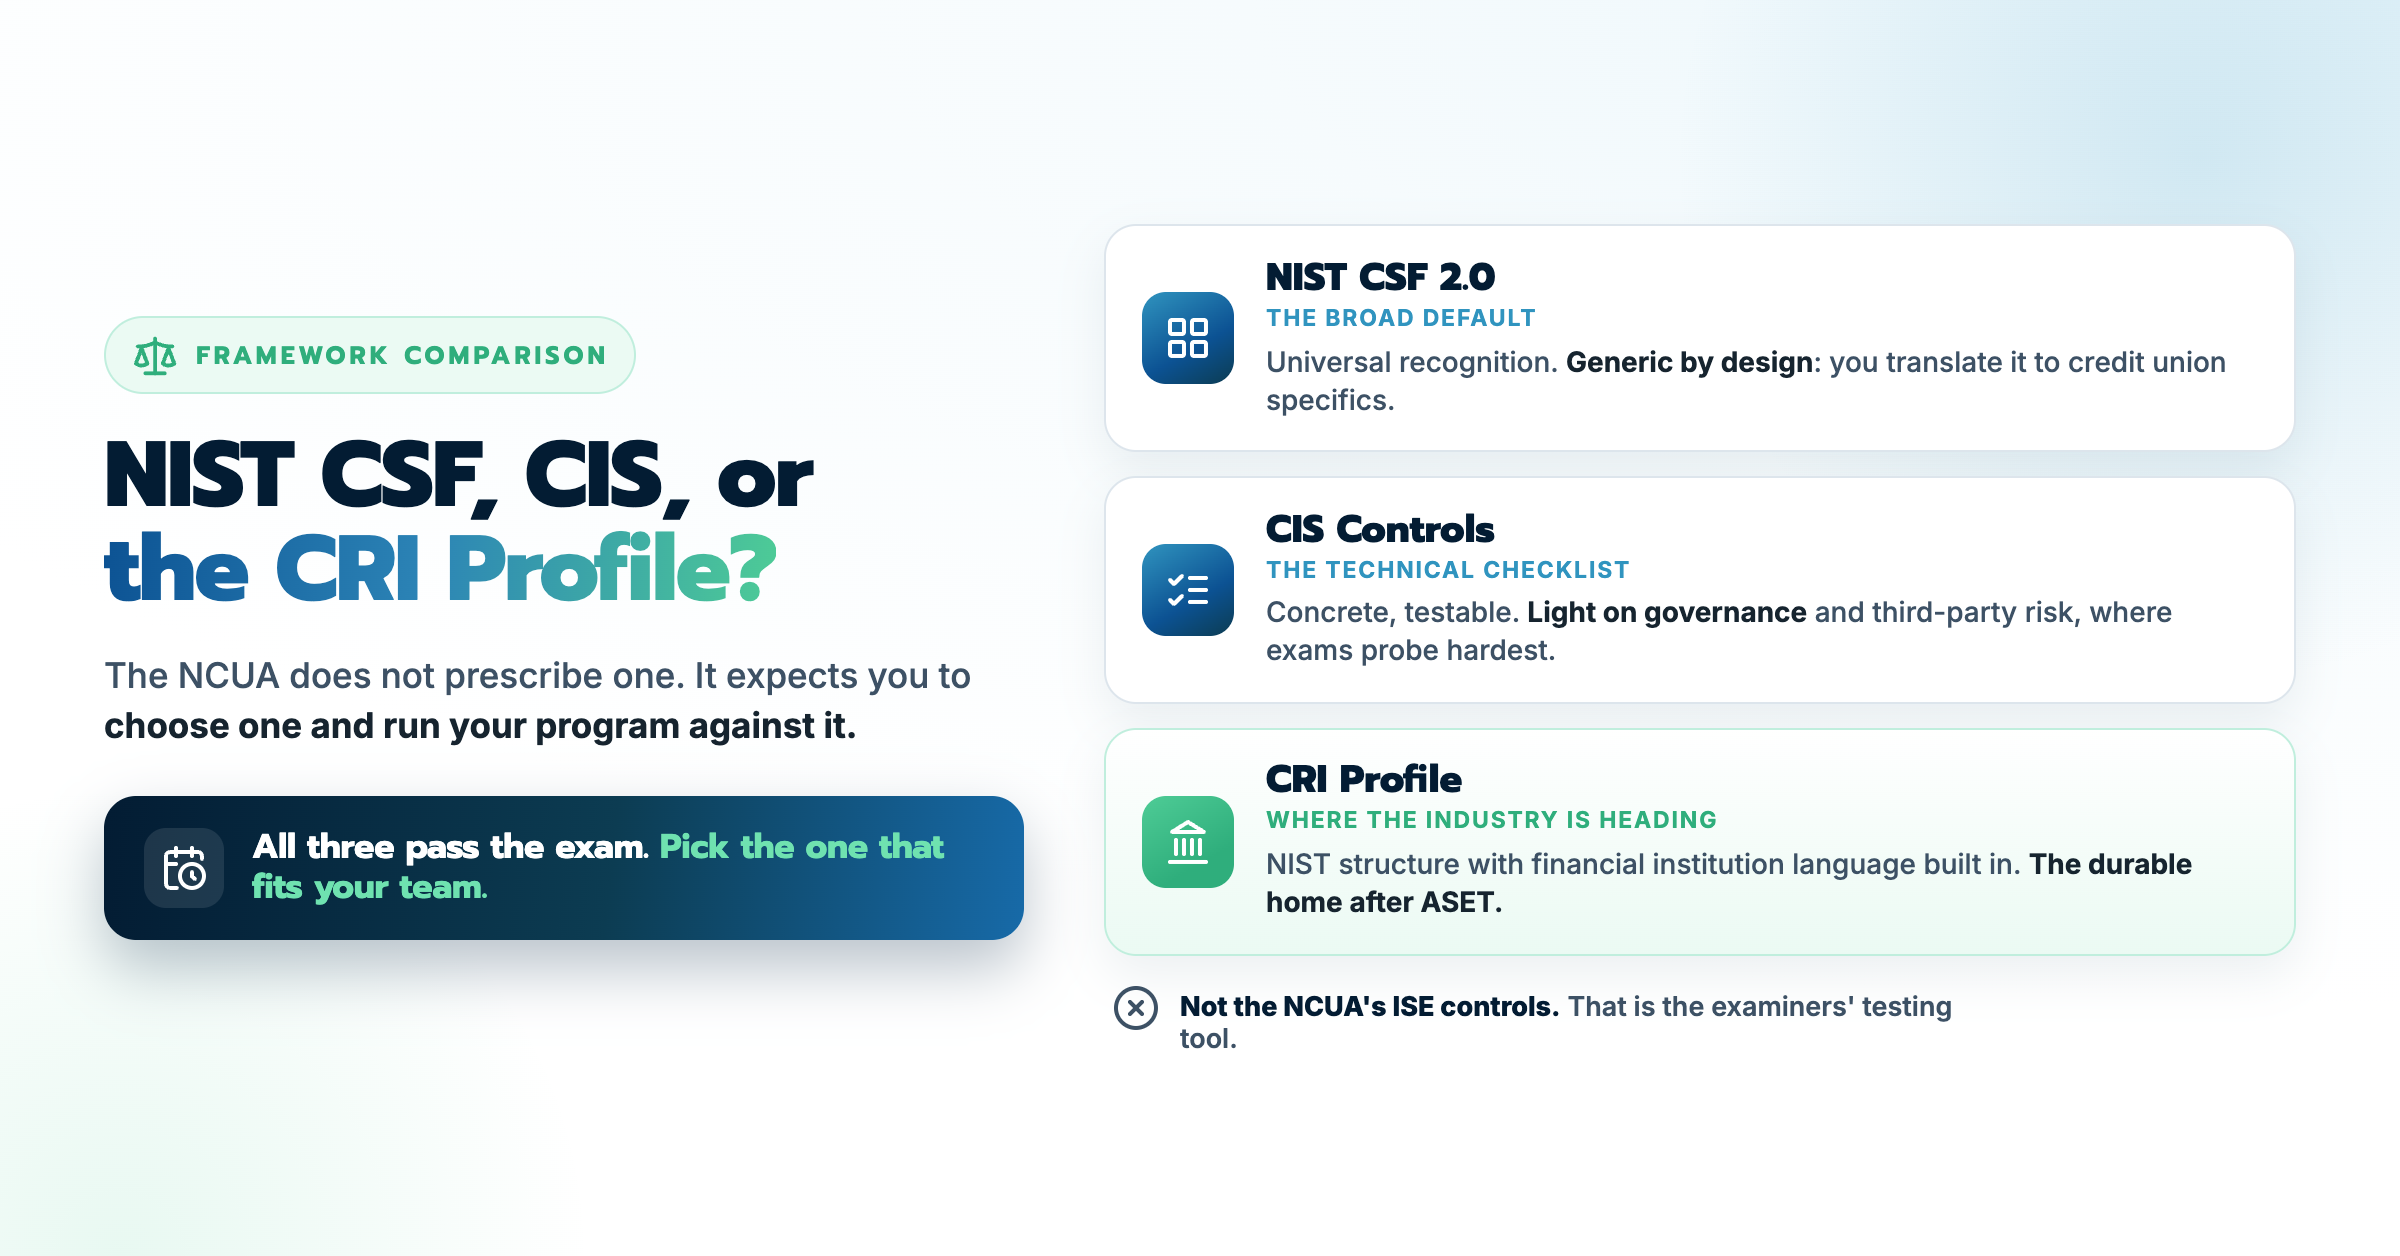
NIST CSF vs CIS vs CRI Profile: Which Framework Should Your Credit Union Choose?

Every credit union security leader eventually asks the same question, usually right before an exam or right after a merger: which framework does the NCUA actually want us on? Two credit unions of the same size sit on different frameworks and both...

Read More
4 min read

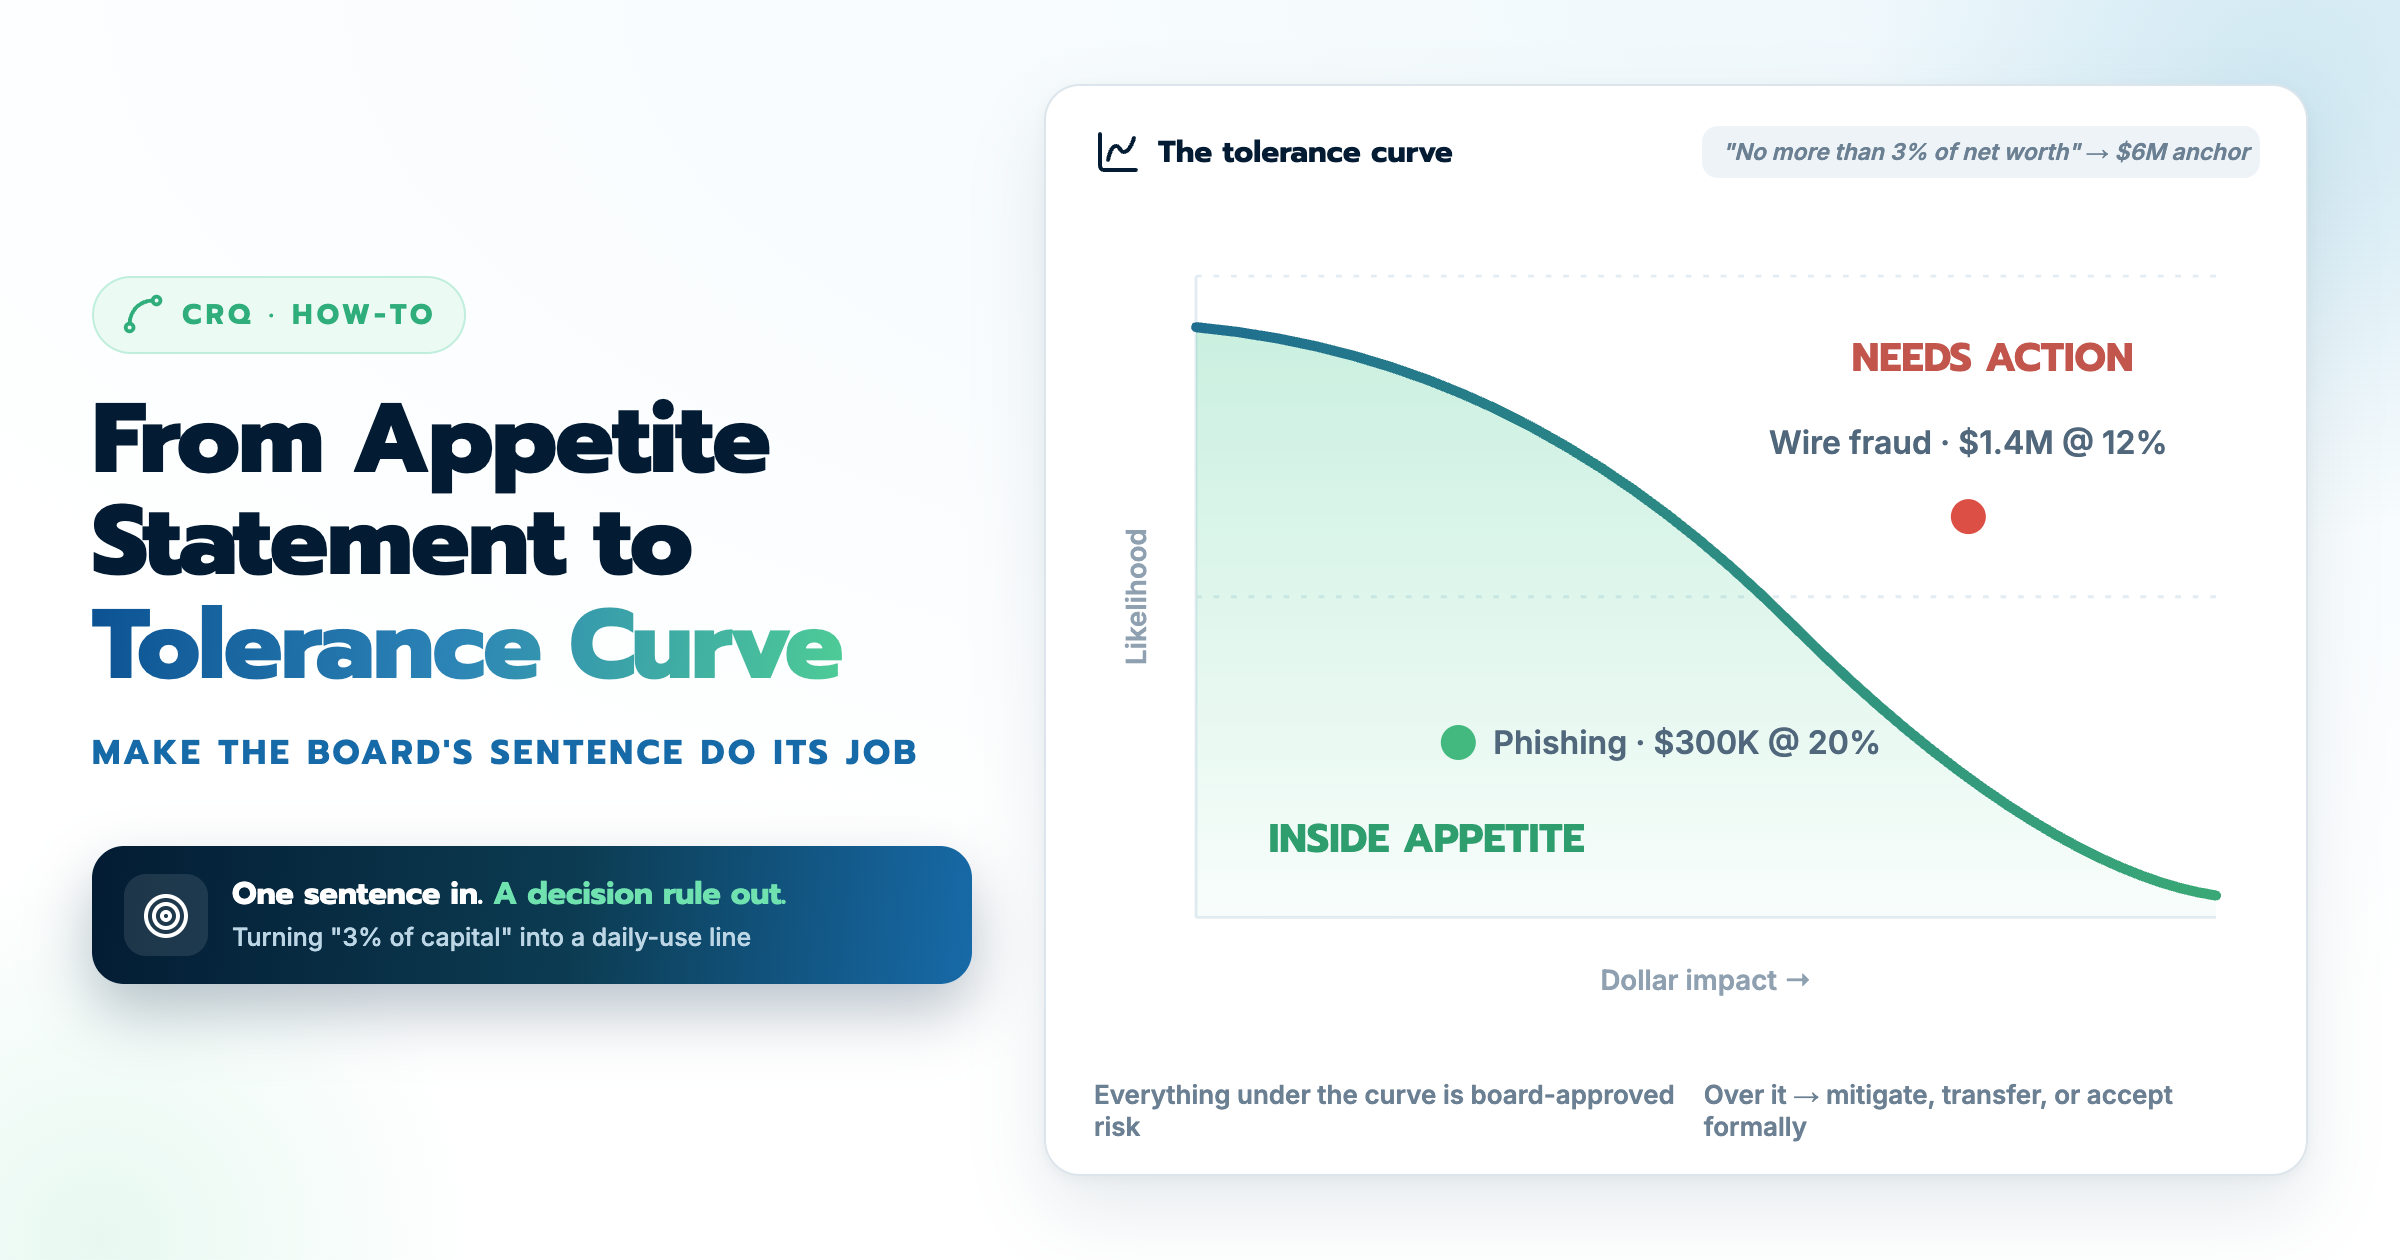
How to Turn a Risk Appetite Statement Into a Usable Curve

Somewhere in your board policy there is a sentence like this: "The credit union will not accept cyber risk exceeding 3 percent of net worth." The...

Read More

5 min read

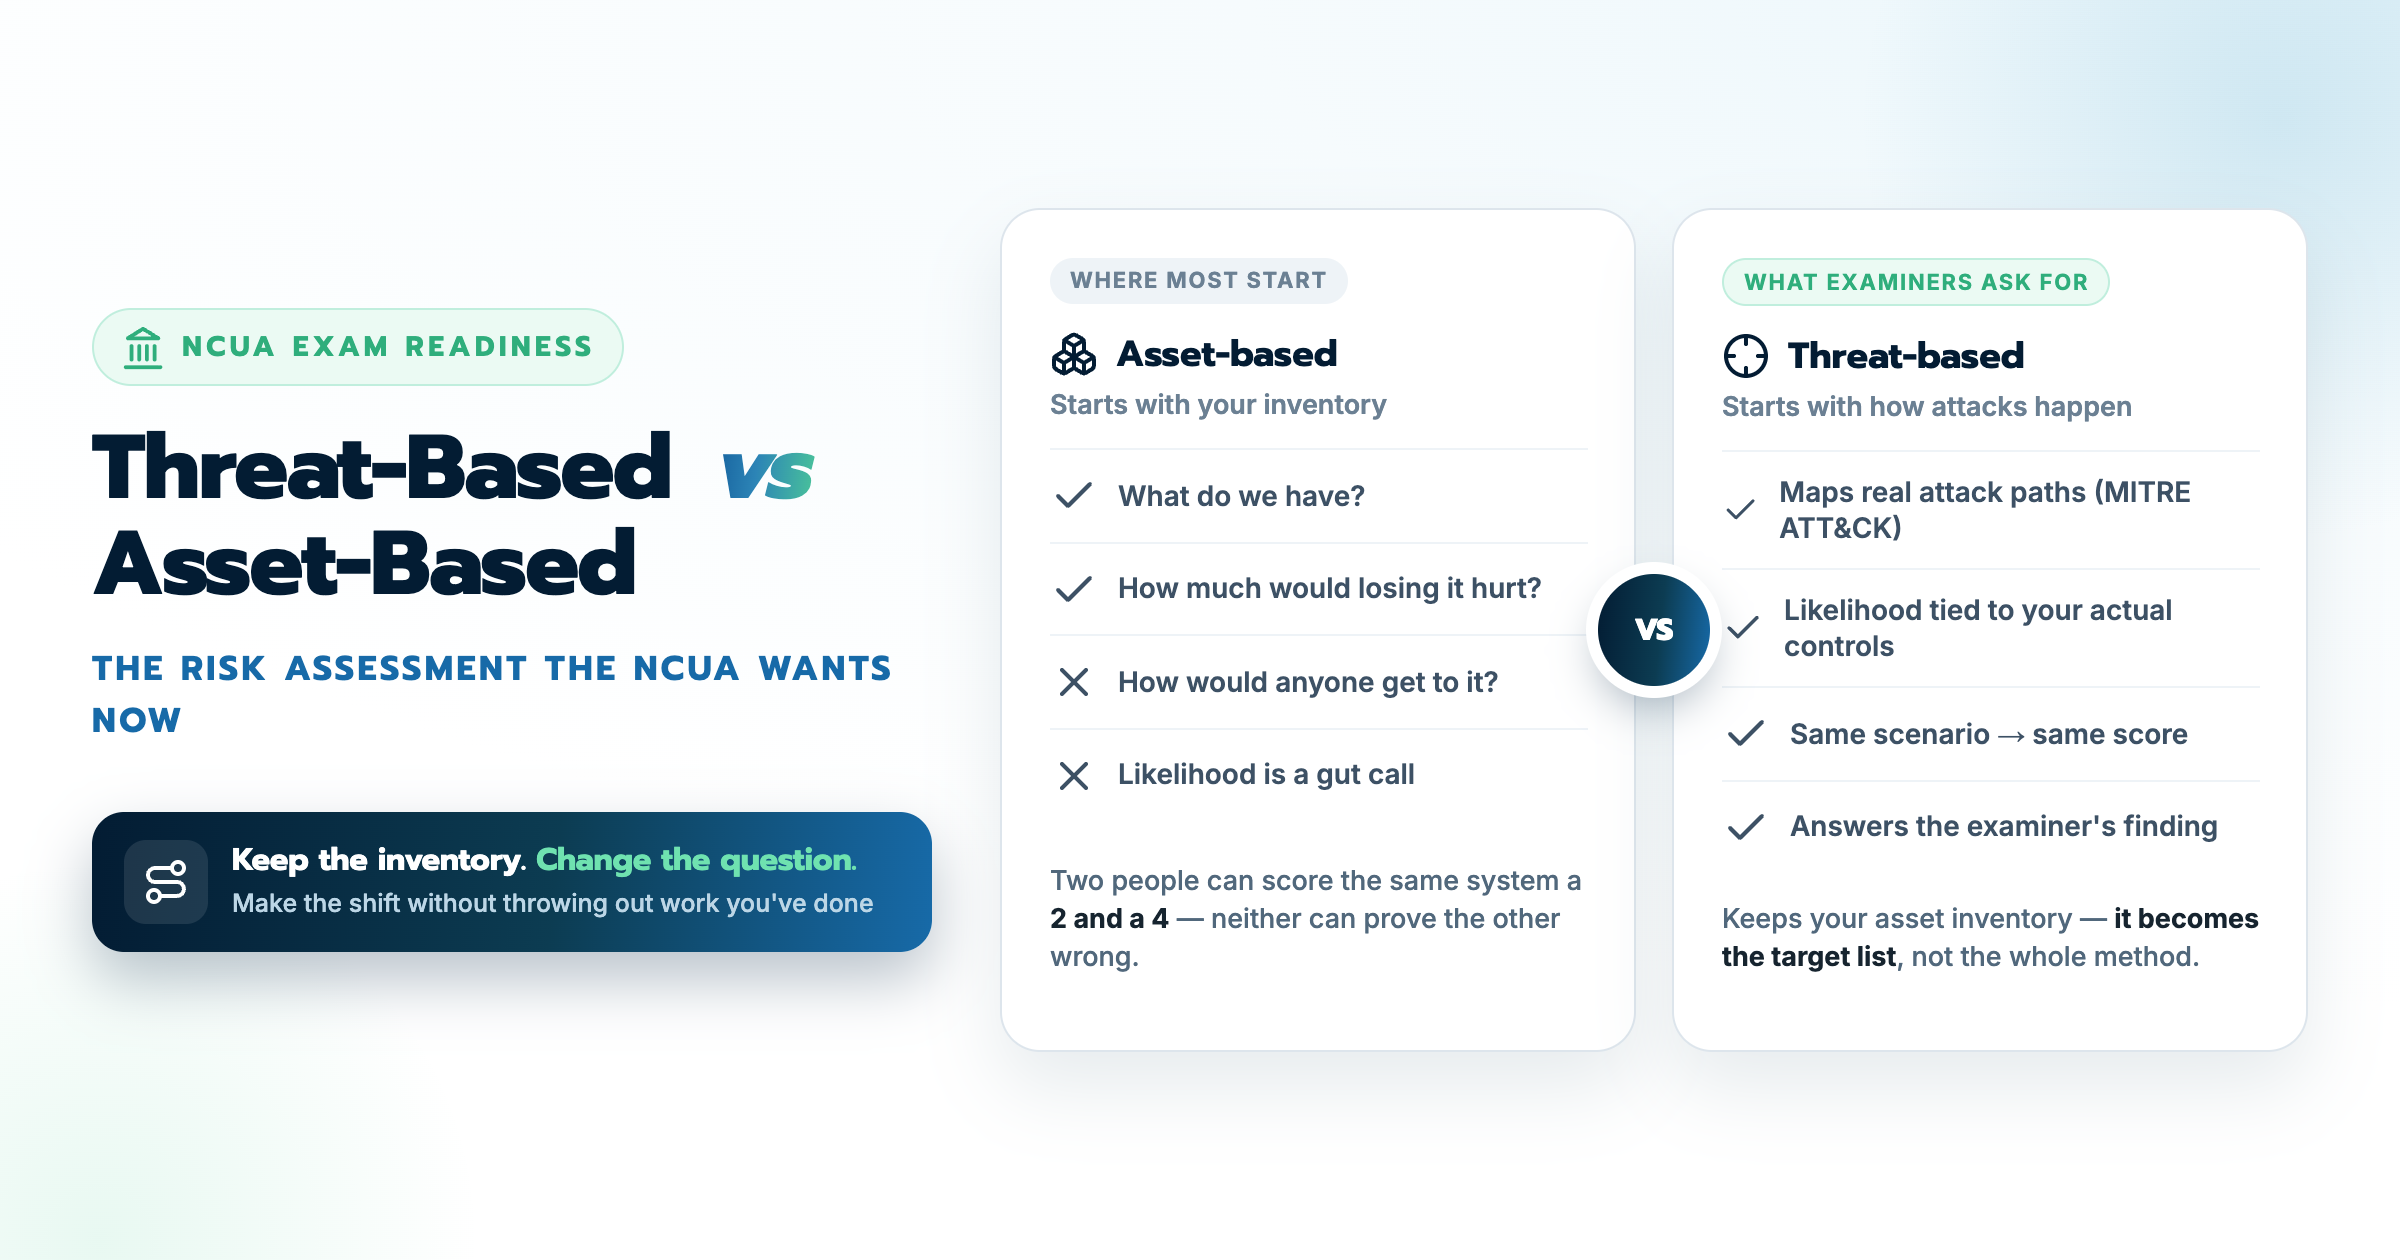
Threat-Based vs Asset-Based Risk Assessment: NCUA View

Pull up your current risk assessment and look at what the rows actually are. For most institutions, they are threats: ransomware, phishing, insider...

Read More

5 min read

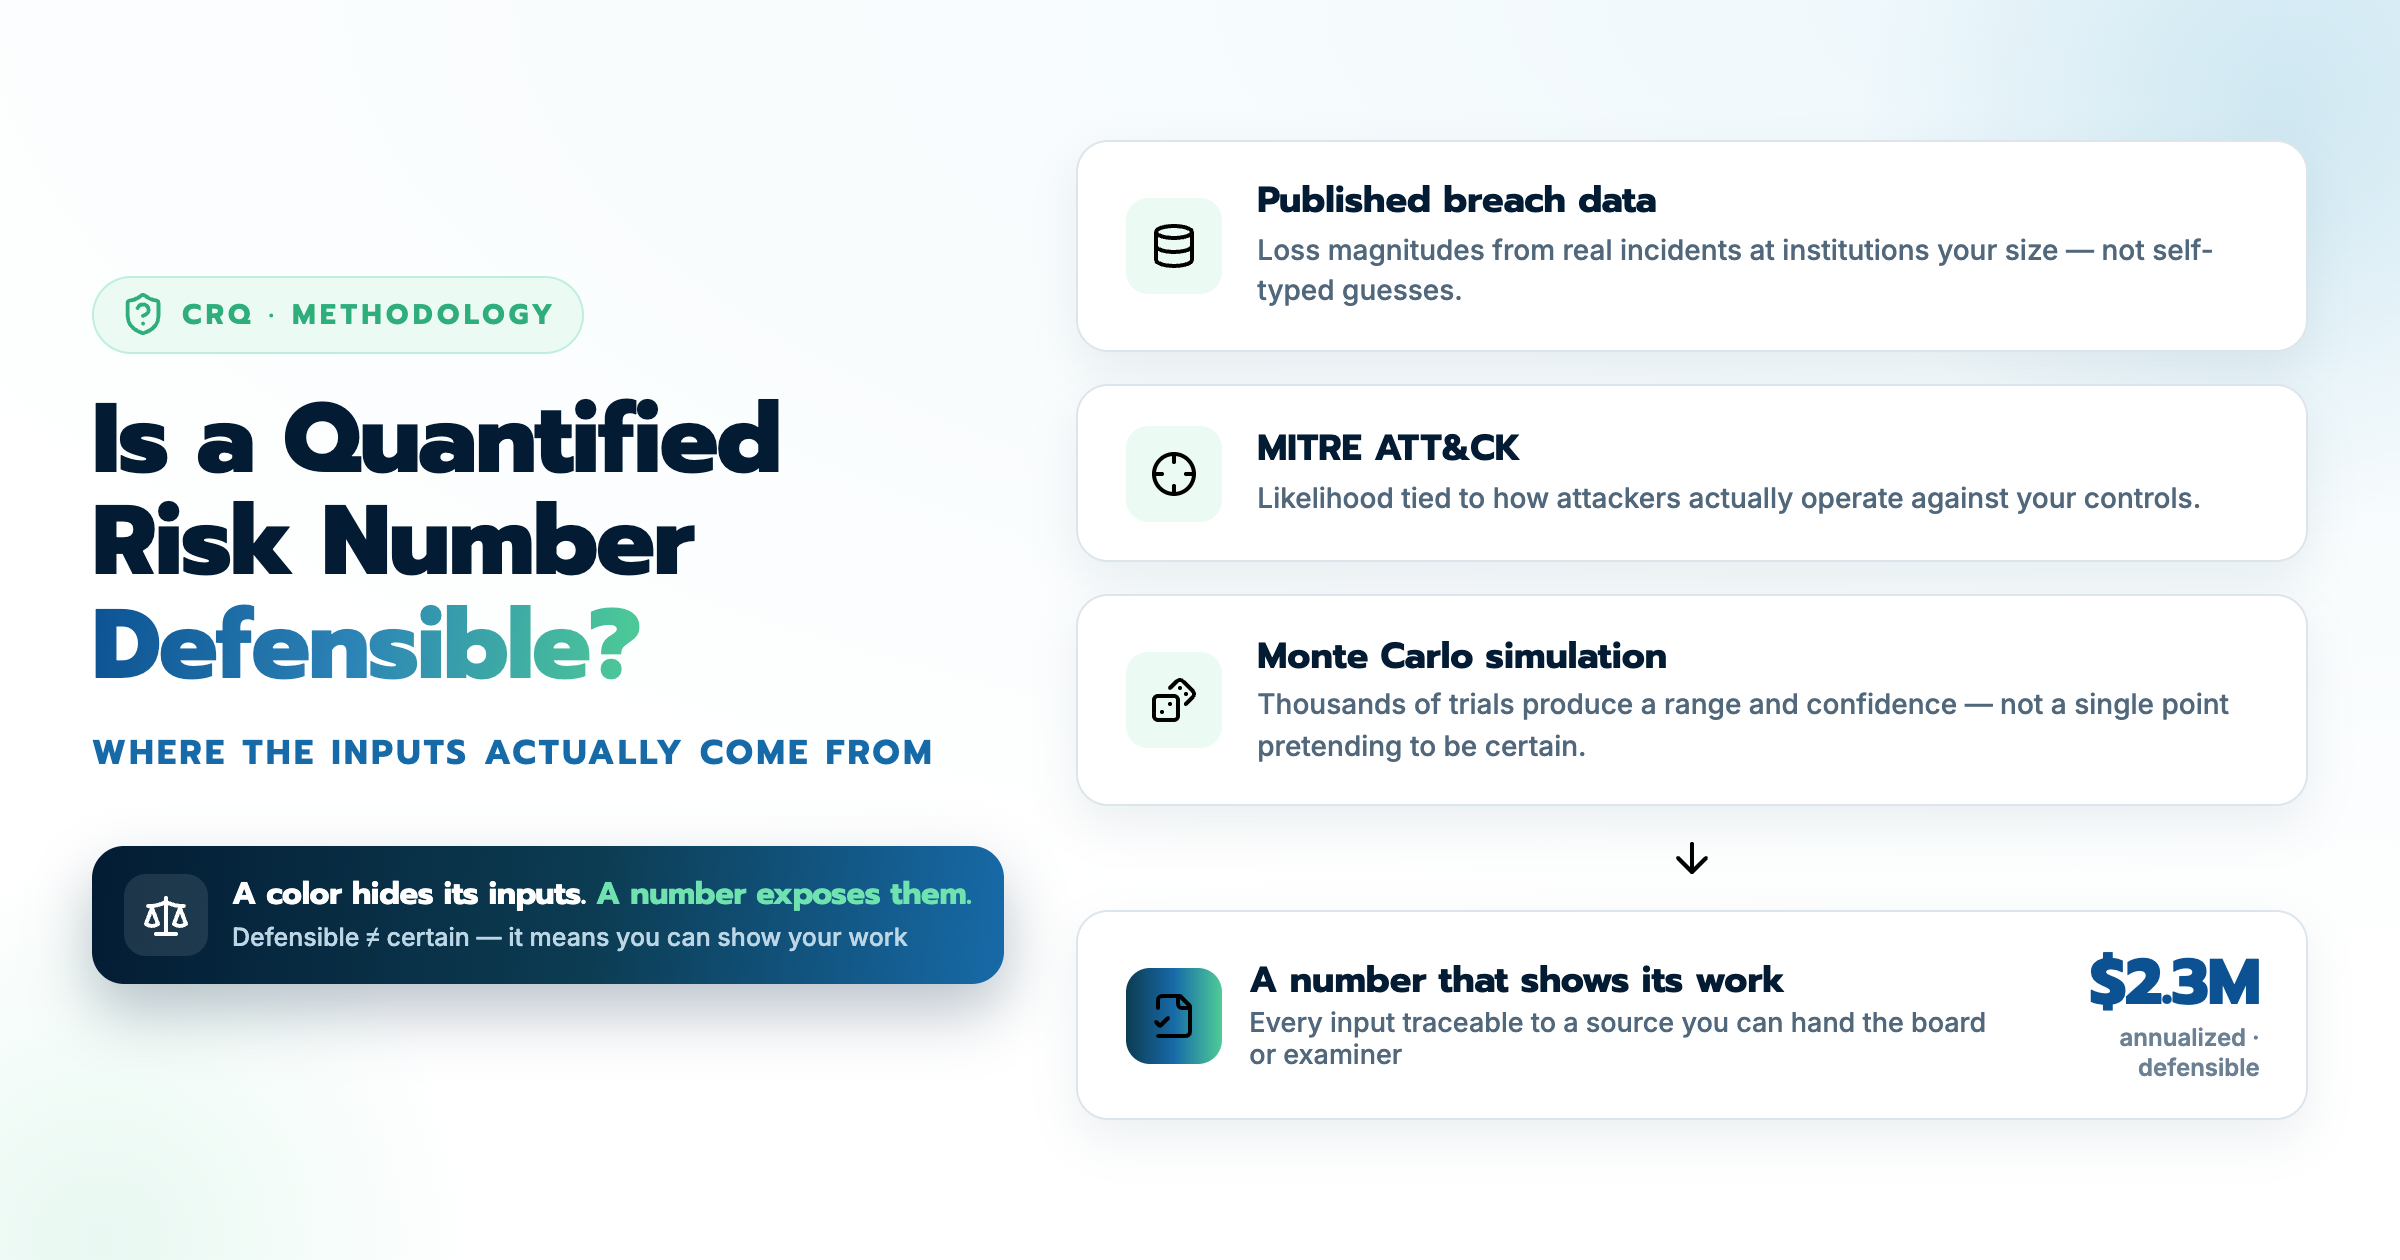
Is a Quantified Cyber Risk Number Defensible? The Inputs

The most common objection to cyber risk quantification does not come from boards. It comes from security leaders, and it goes like this: the number...

Read More

4 min read

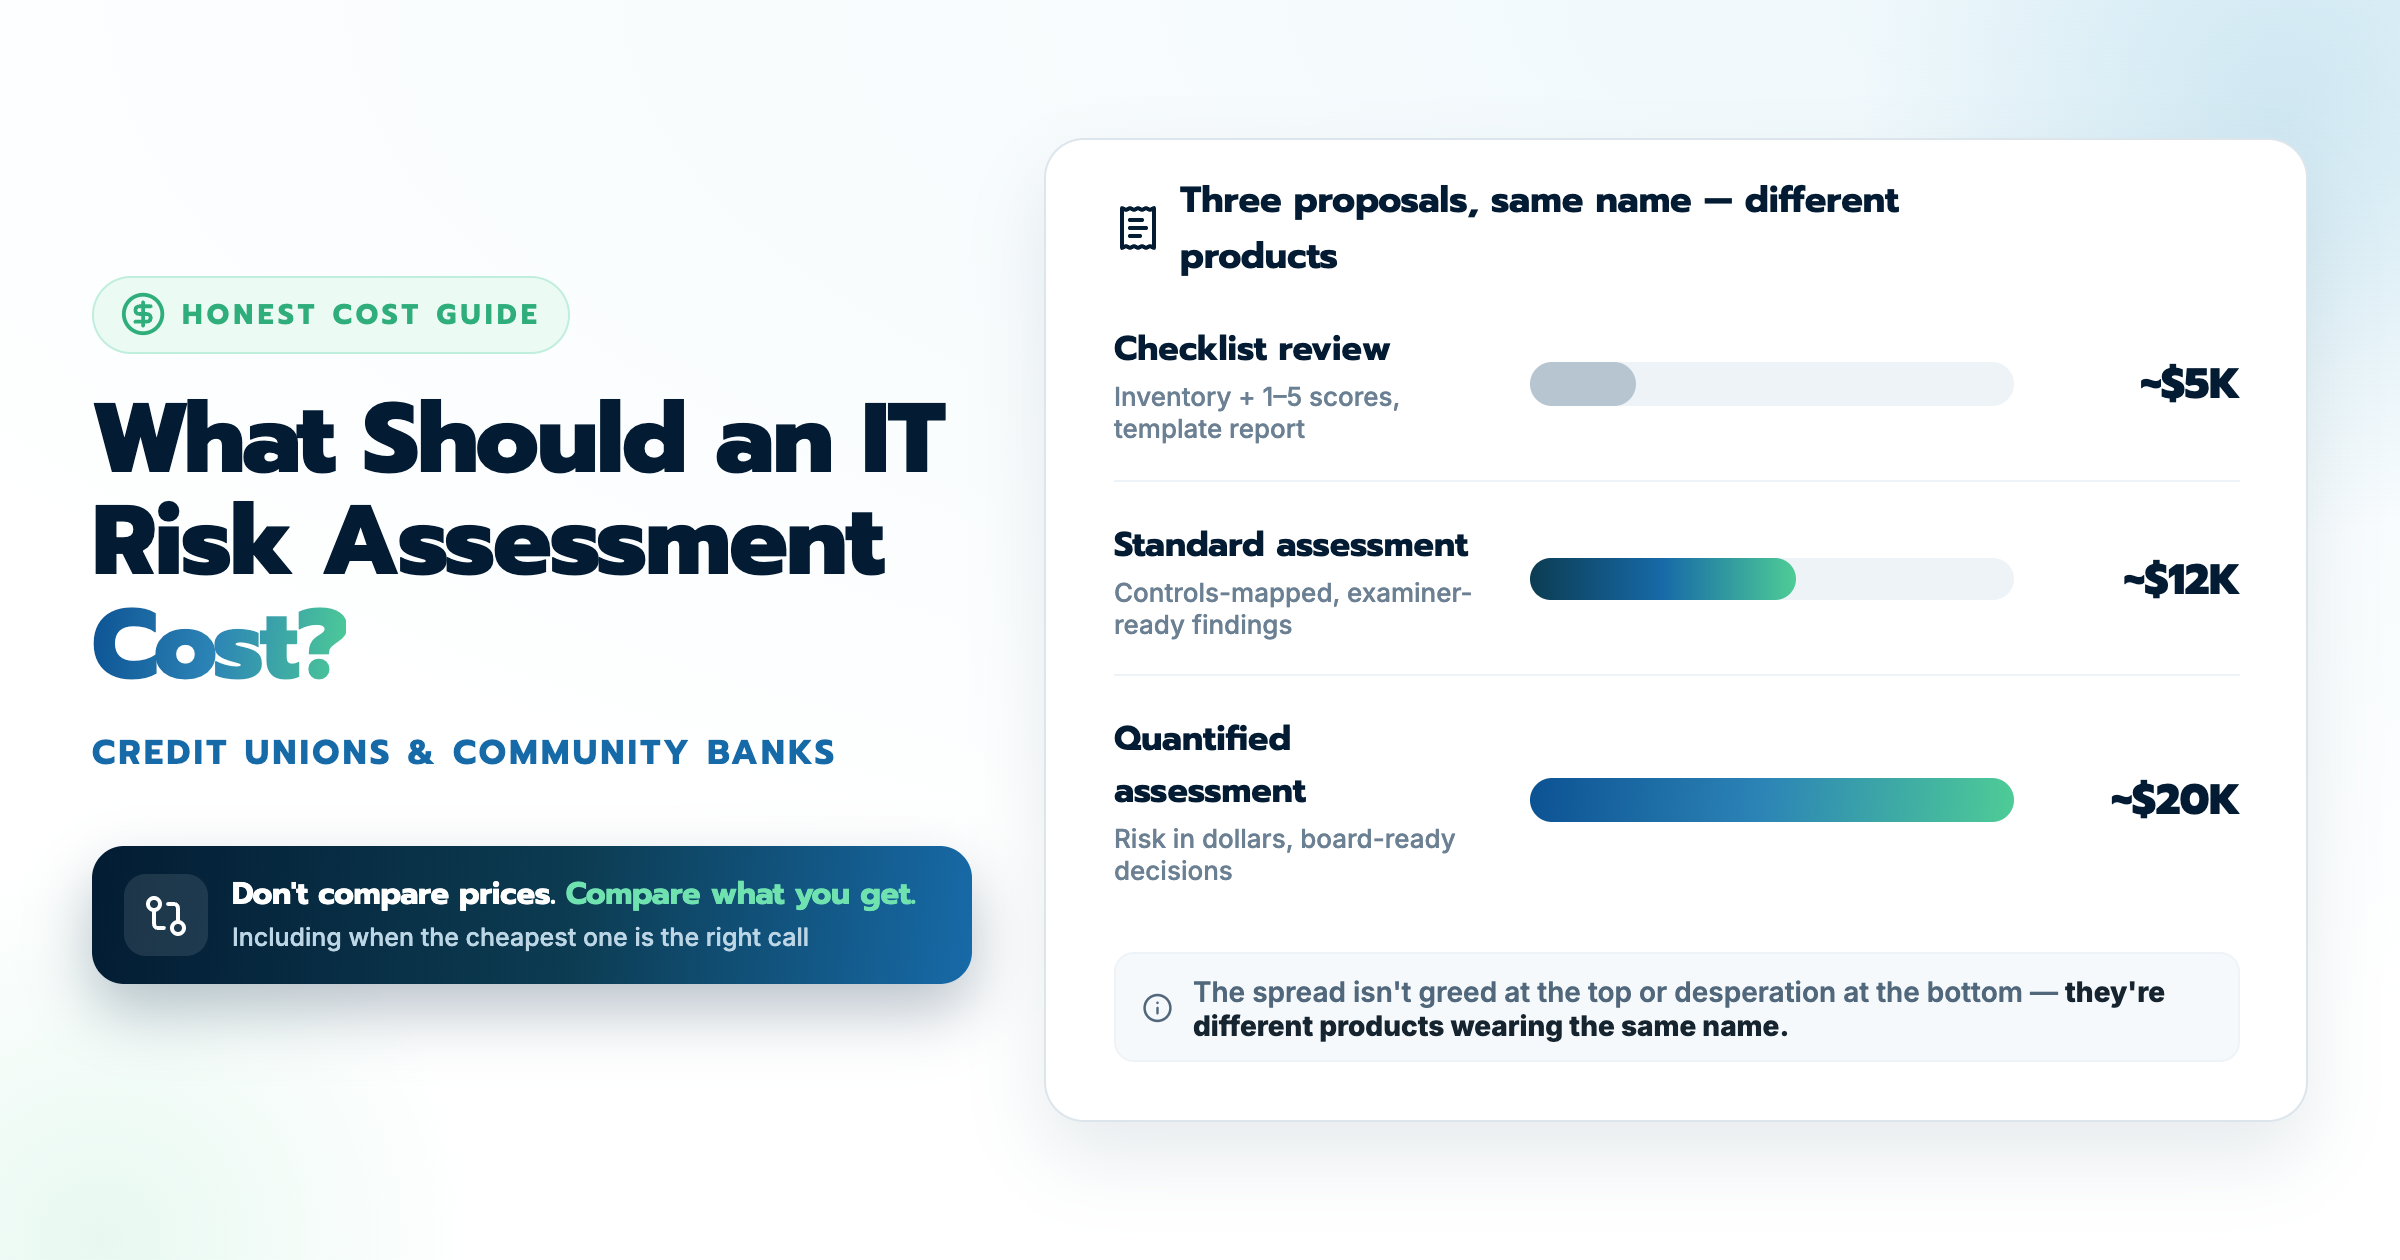
What Should a Credit Union IT Risk Assessment Cost?

You have three proposals on your desk and the numbers are thousands of dollars apart for what each vendor calls the same thing: an IT risk...

Read More

8 min read

Risk in Dollars, Not Colors: A Complete Guide to Board Reporting

A security officer at a credit union told me that in his entire time at the institution, they had never once talked about risk in numbers. Colors,...

Read More

9 min read

How to Choose the Right vCISO: A Guide for Highly Regulated Organizations

Quick answer: Choose a vCISO who acts as a strategic security leader, not an operator. The right one owns risk, governance, board reporting, and the...

Read More

9 min read

NIST AI RMF: Where to Start with AI Governance

Quick Answer: AI governance starts with the Govern function of the NIST AI RMF. That means establishing an AI policy, updating existing cybersecurity...

Read More

4 min read

Risk Assessment vs. Risk Analysis

Risk assessment and risk analysis are distinct but complementary, and understanding the difference helps organizations avoid blind spots in security...

Read More
How to Create a Cybersecurity Program - Rivial Security

3 min read

How to Create a Cybersecurity Program

Here are the key takeaways from this blog: Start with a self-assessment: Understand what data you're storing, audit systems and devices, and evaluate...

Read More