Skip to the main content.
Watch Demo Meet With Our Team
Rivial’s Cybersecurity blog

The Savvy CISO

Cybersecurity management insights, tips, and trends for security leaders, CISOs, vCISOs, and MSSPs who want to work smarter, not harder.

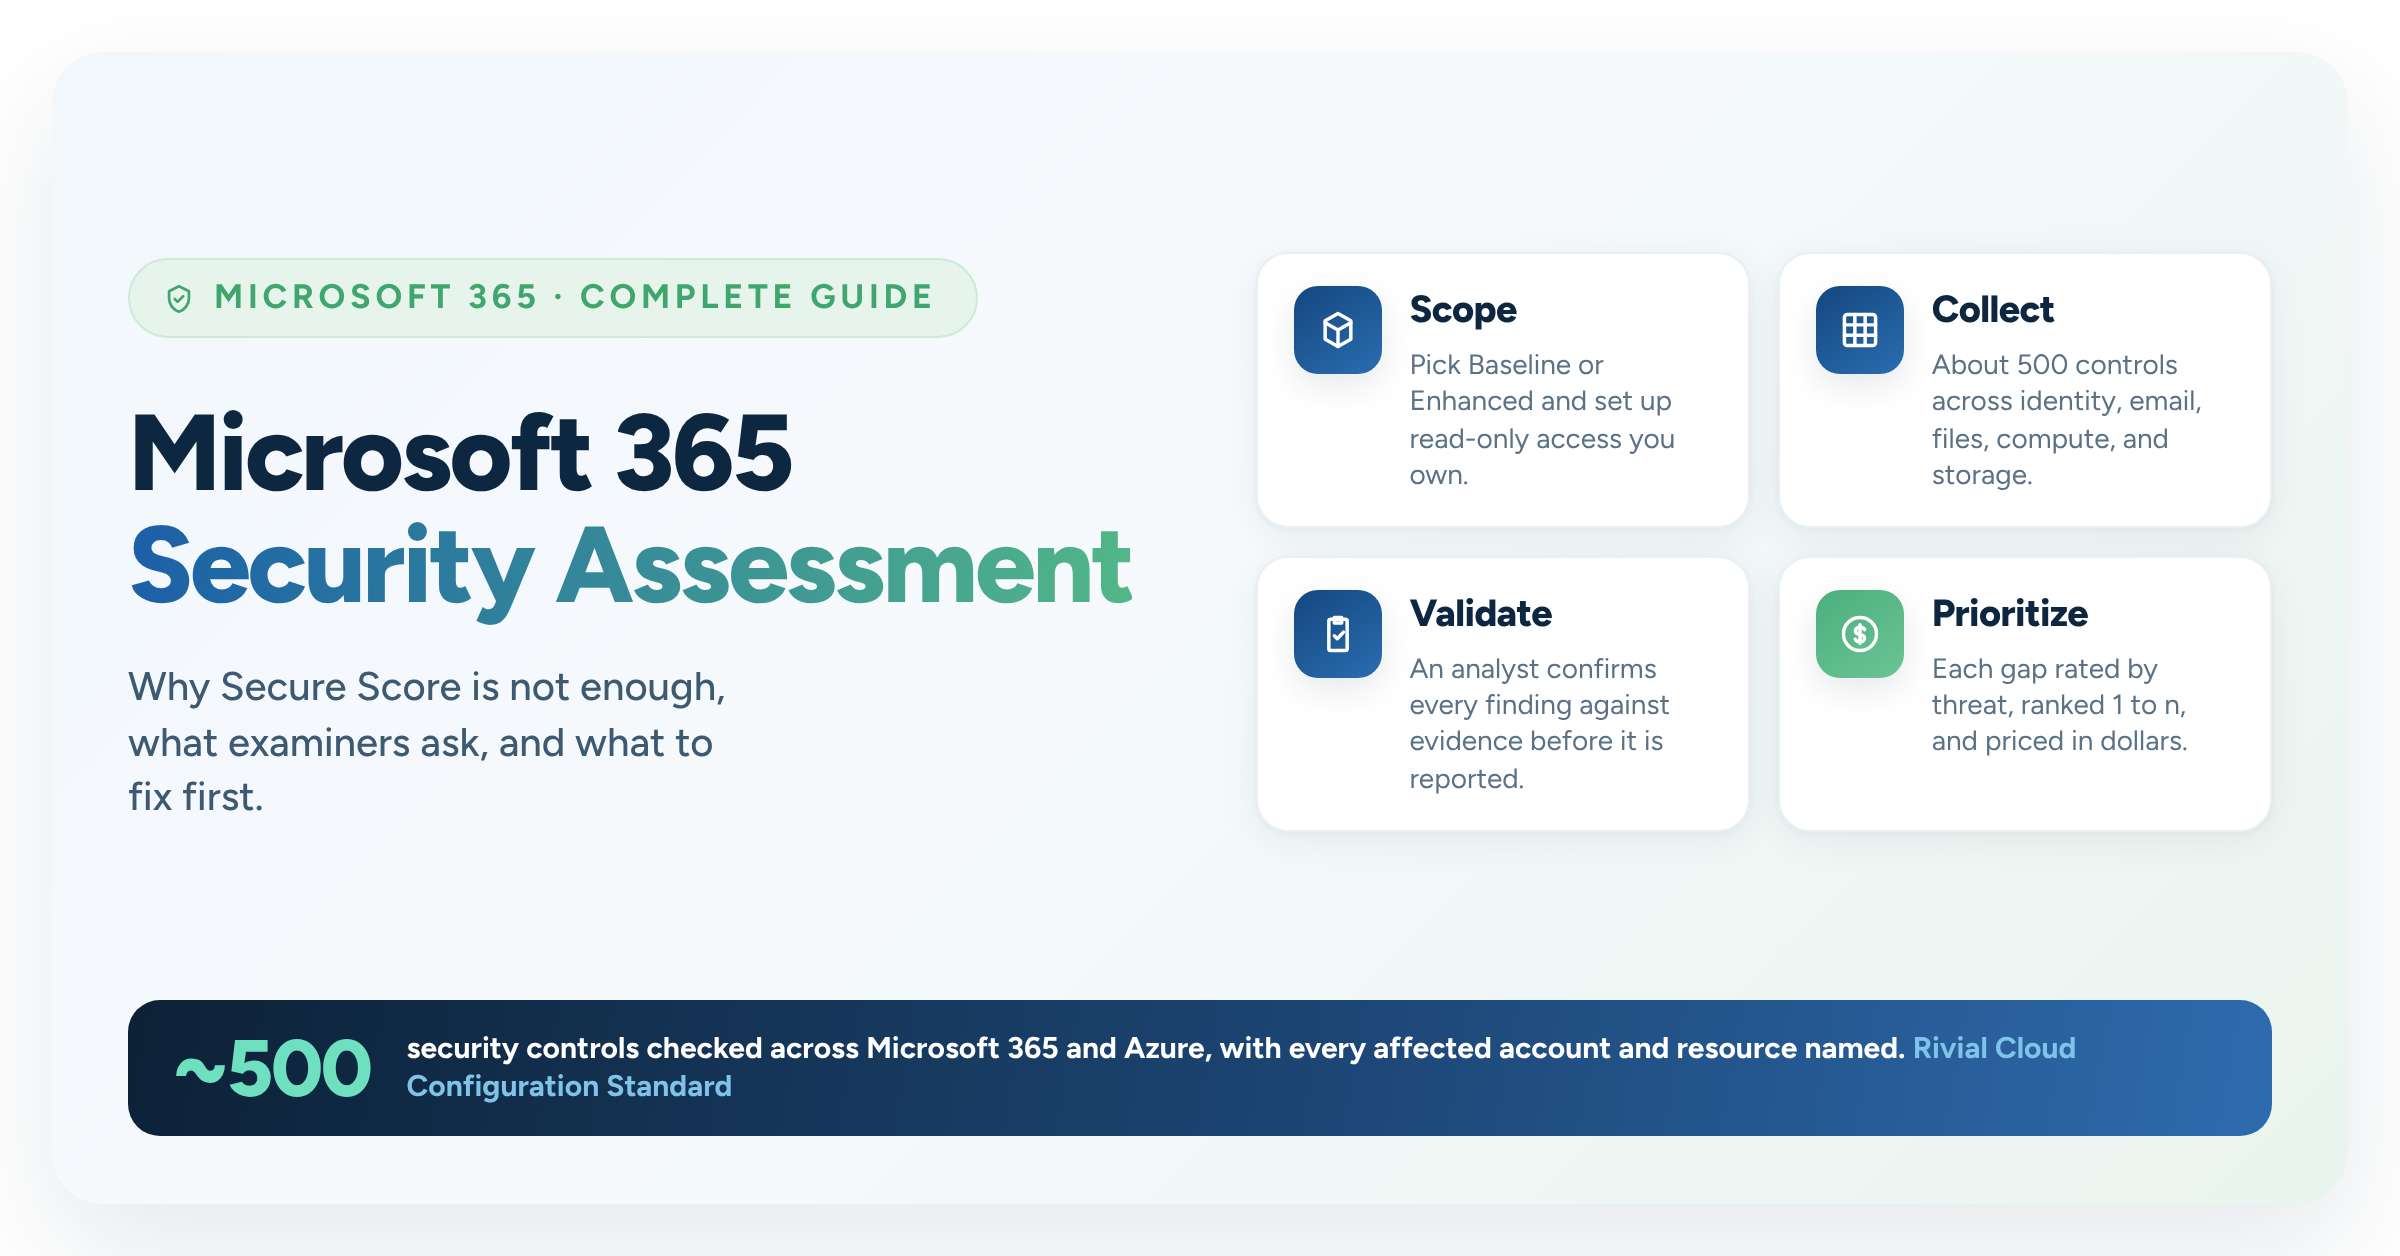
Microsoft 365 security assessment guide graphic showing the four steps: scope, collect, validate, and prioritize

8 min read

Microsoft 365 Security Assessment 101: A Complete Guide

Most organizations I talk to moved to Microsoft 365 five, six, or seven years ago. A vendor set up the conditional access policies during the migration, everyone moved on, and those policies have not been touched since. Meanwhile, Microsoft has...

Read More
5 min read

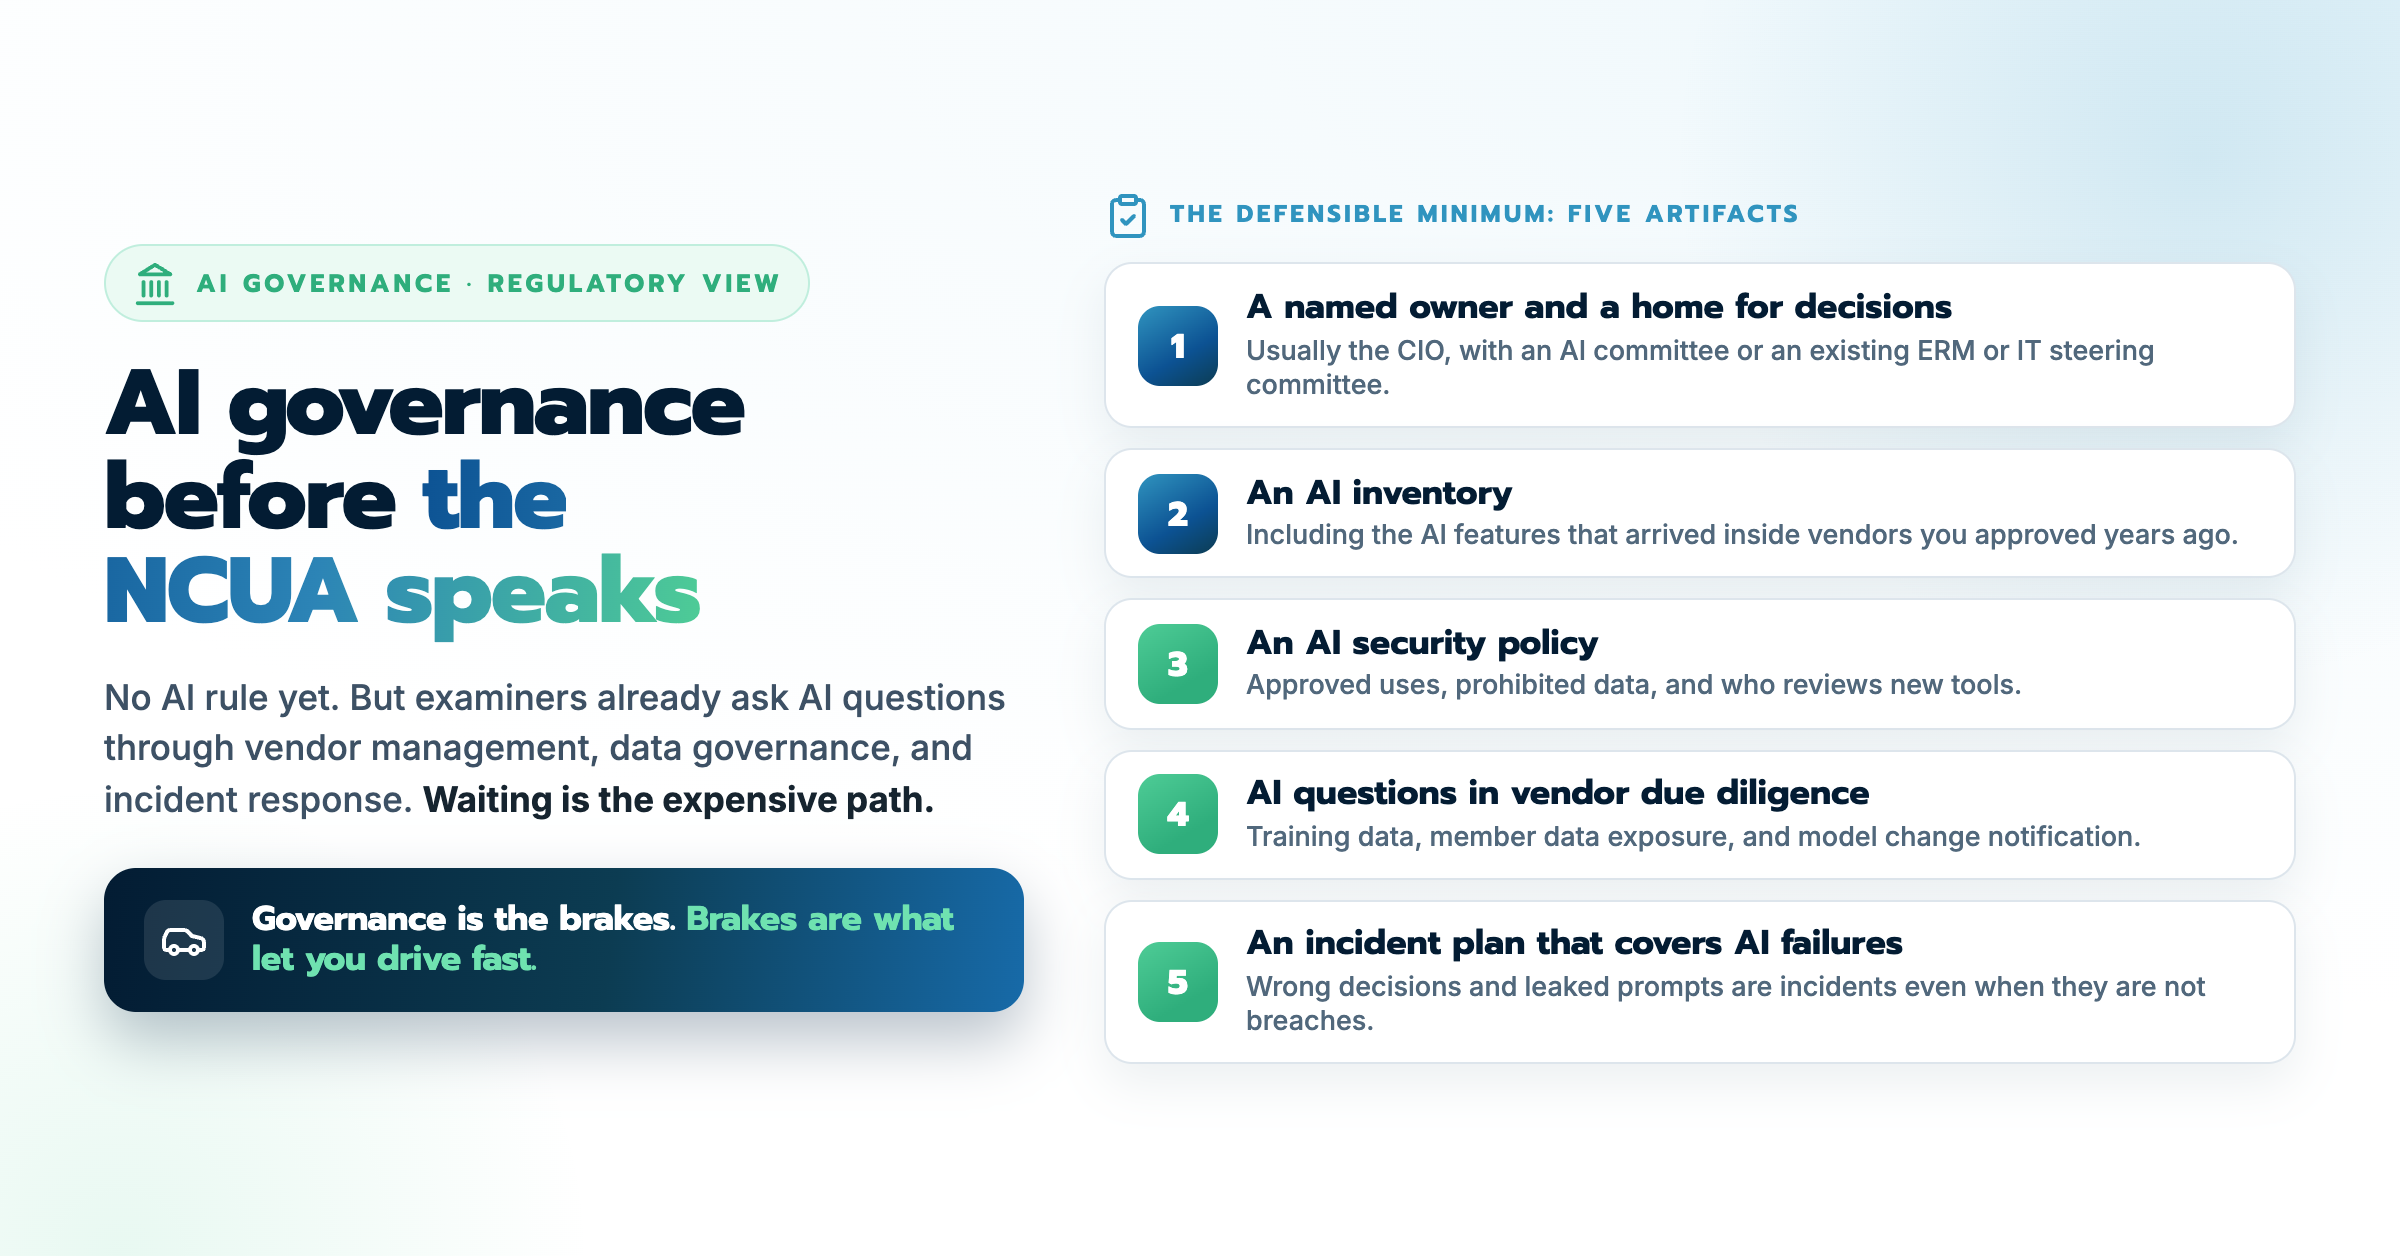
AI Governance When the Regulator Is Silent: What to Do Before the NCUA Speaks

I keep hearing the same sentence on calls with credit union leaders, and I understand exactly why they say it: "The NCUA hasn't told us what to do...

Read More

5 min read

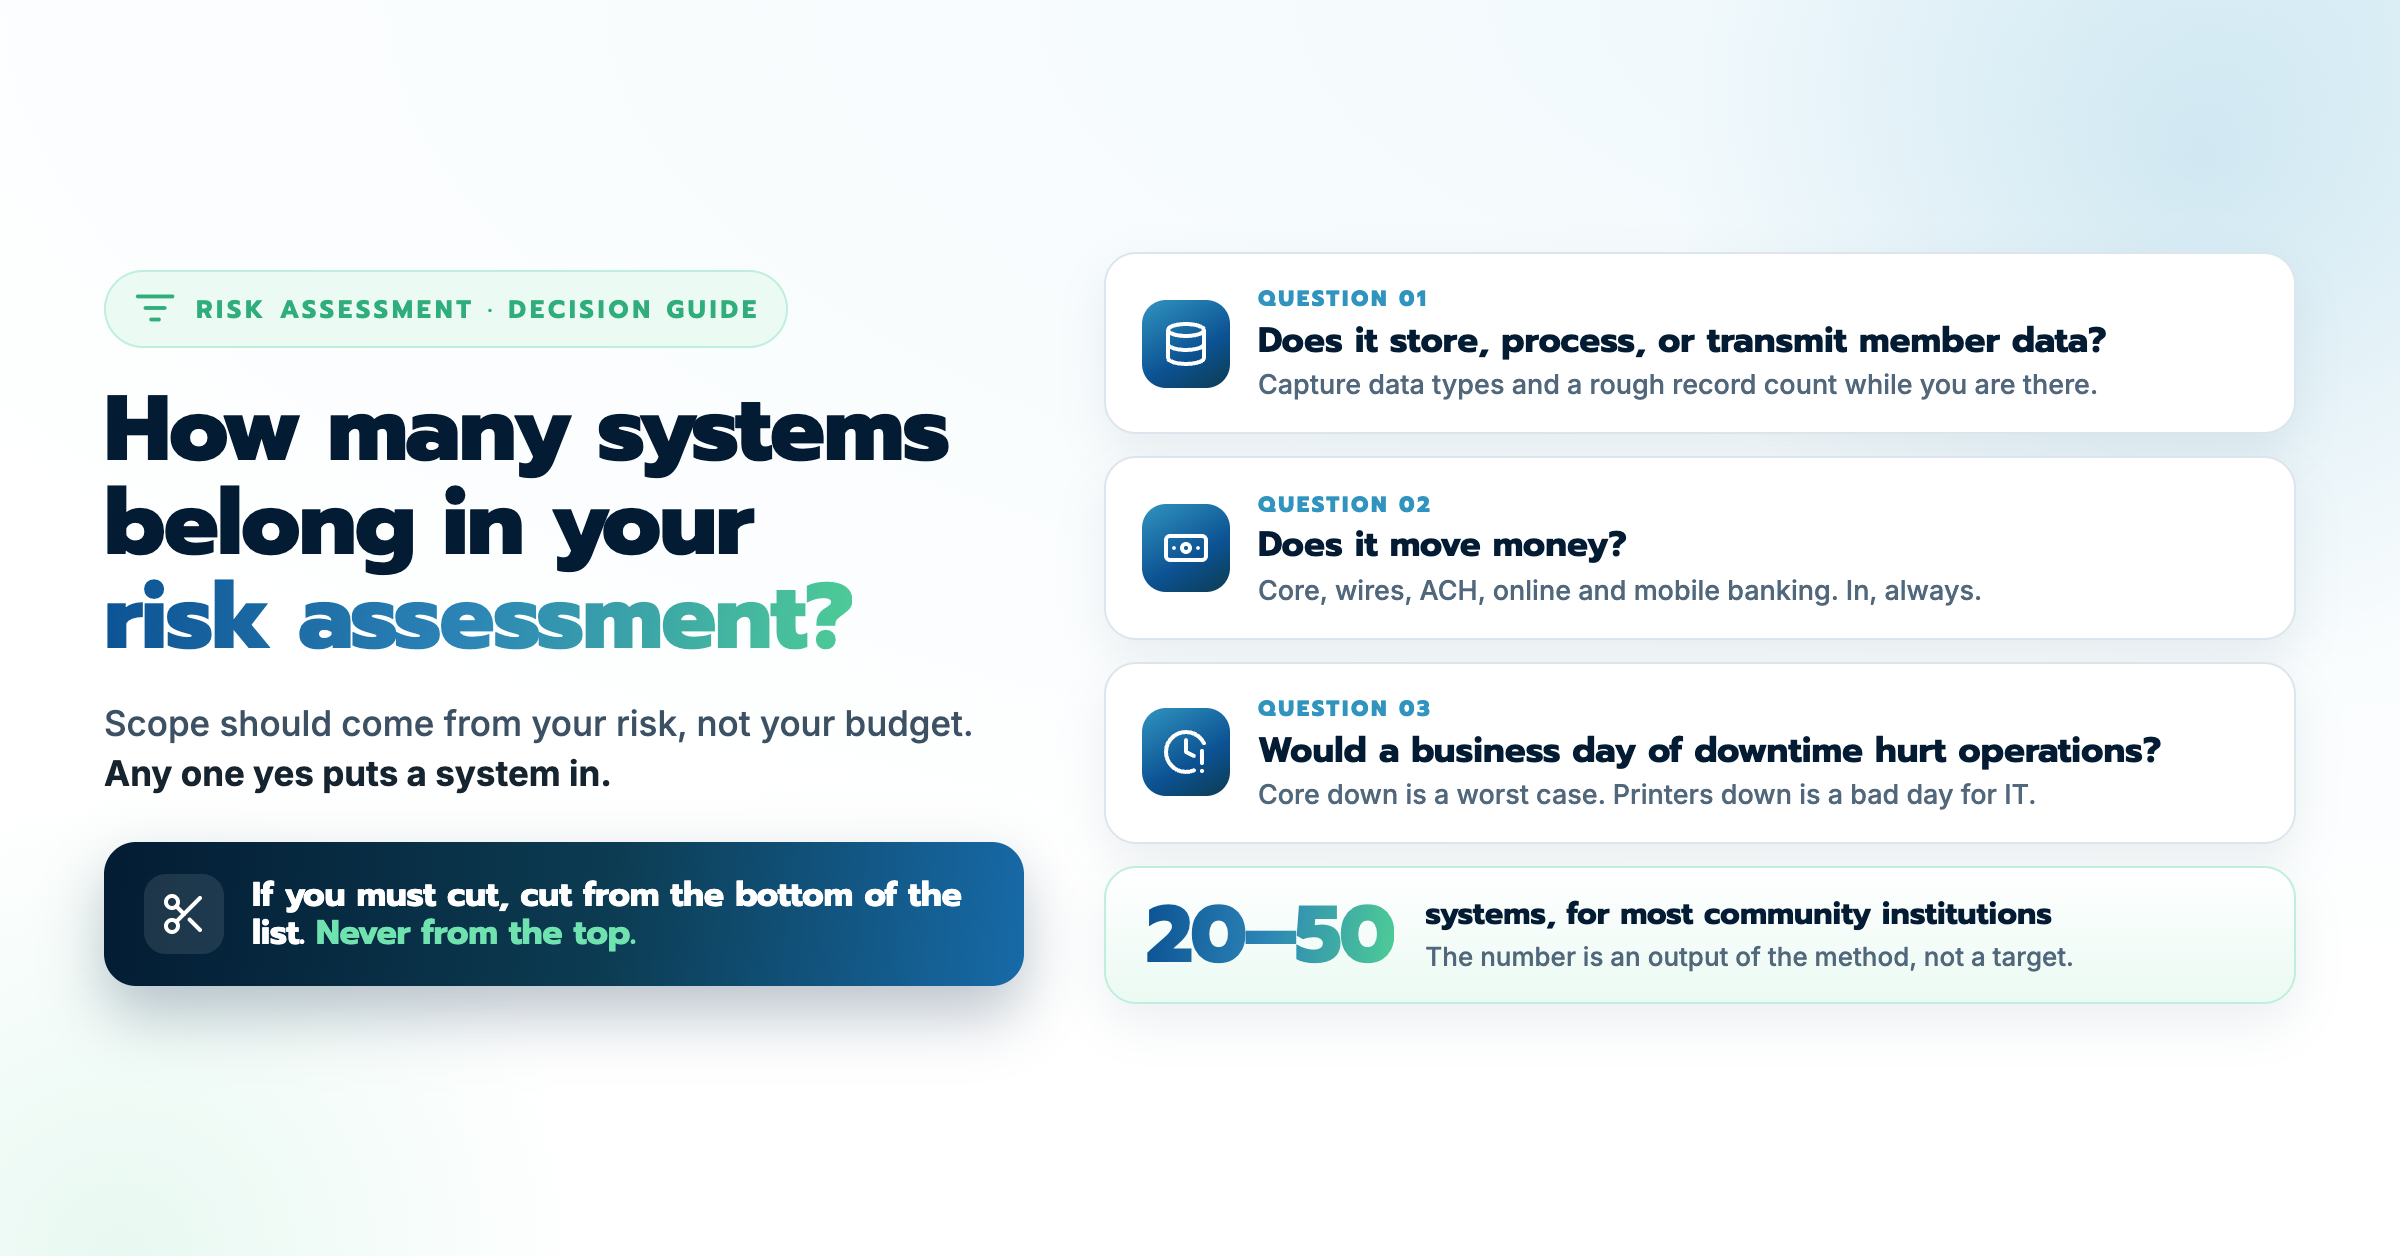
How Many Systems Belong in Your IT Risk Assessment?

Somewhere in almost every risk assessment proposal, the same quiet negotiation happens. The list starts at 60 systems, someone winces at the price,...

Read More

5 min read

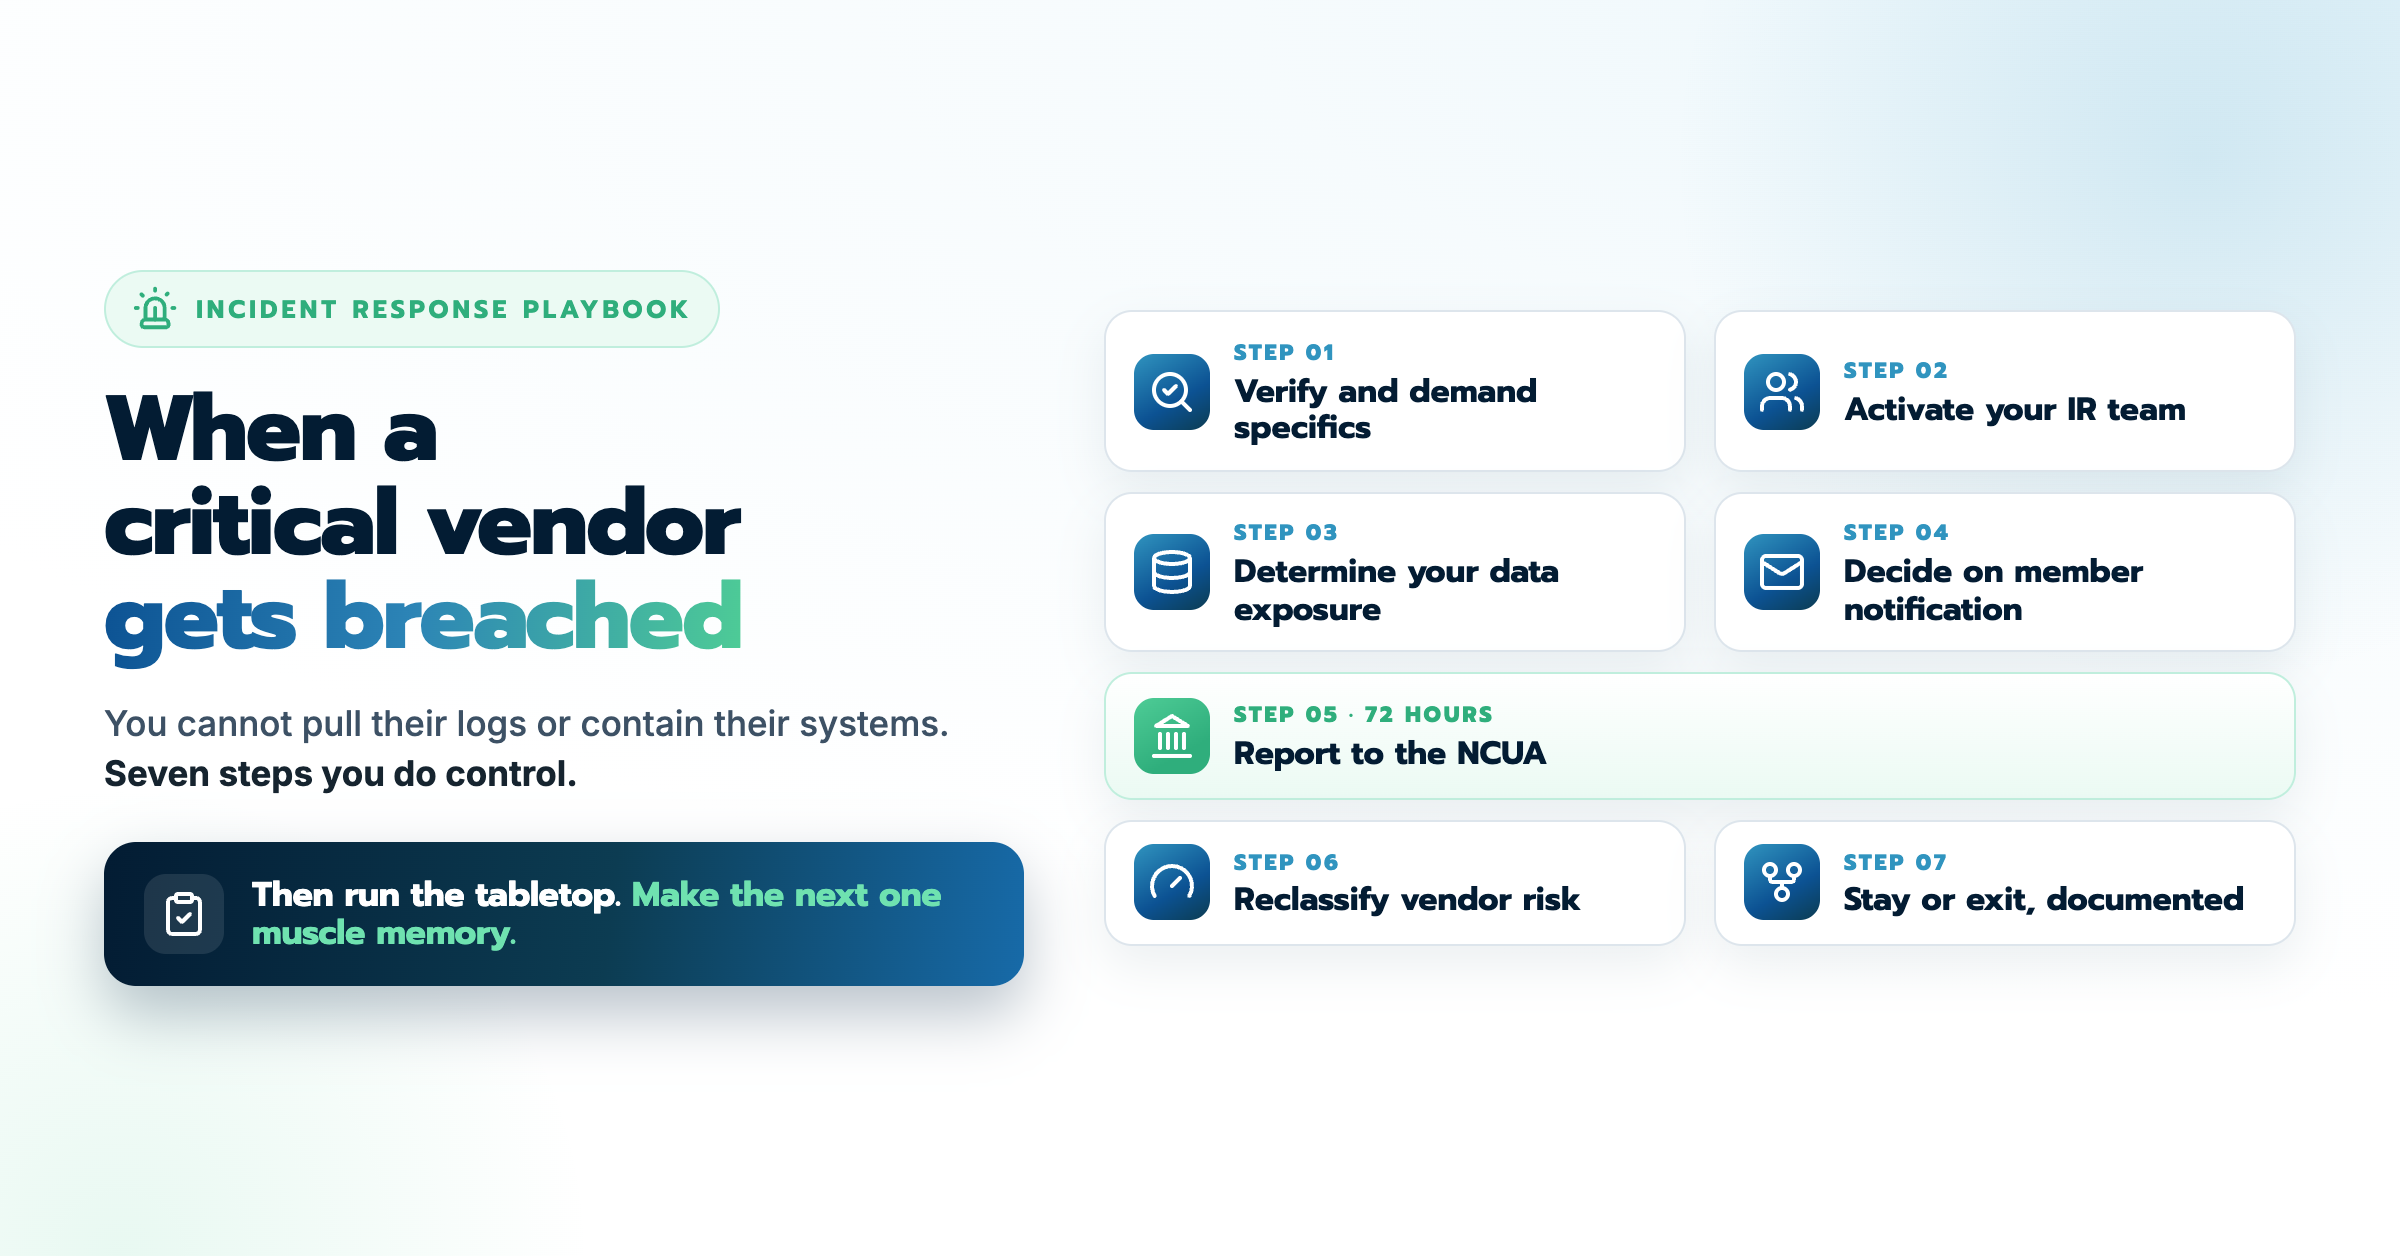
Incident Response Playbook: When a Critical Vendor Gets Breached

If you work at a credit union, the last few months have made one thing hard to ignore: your next incident probably will not start on your network. It...

Read More

4 min read

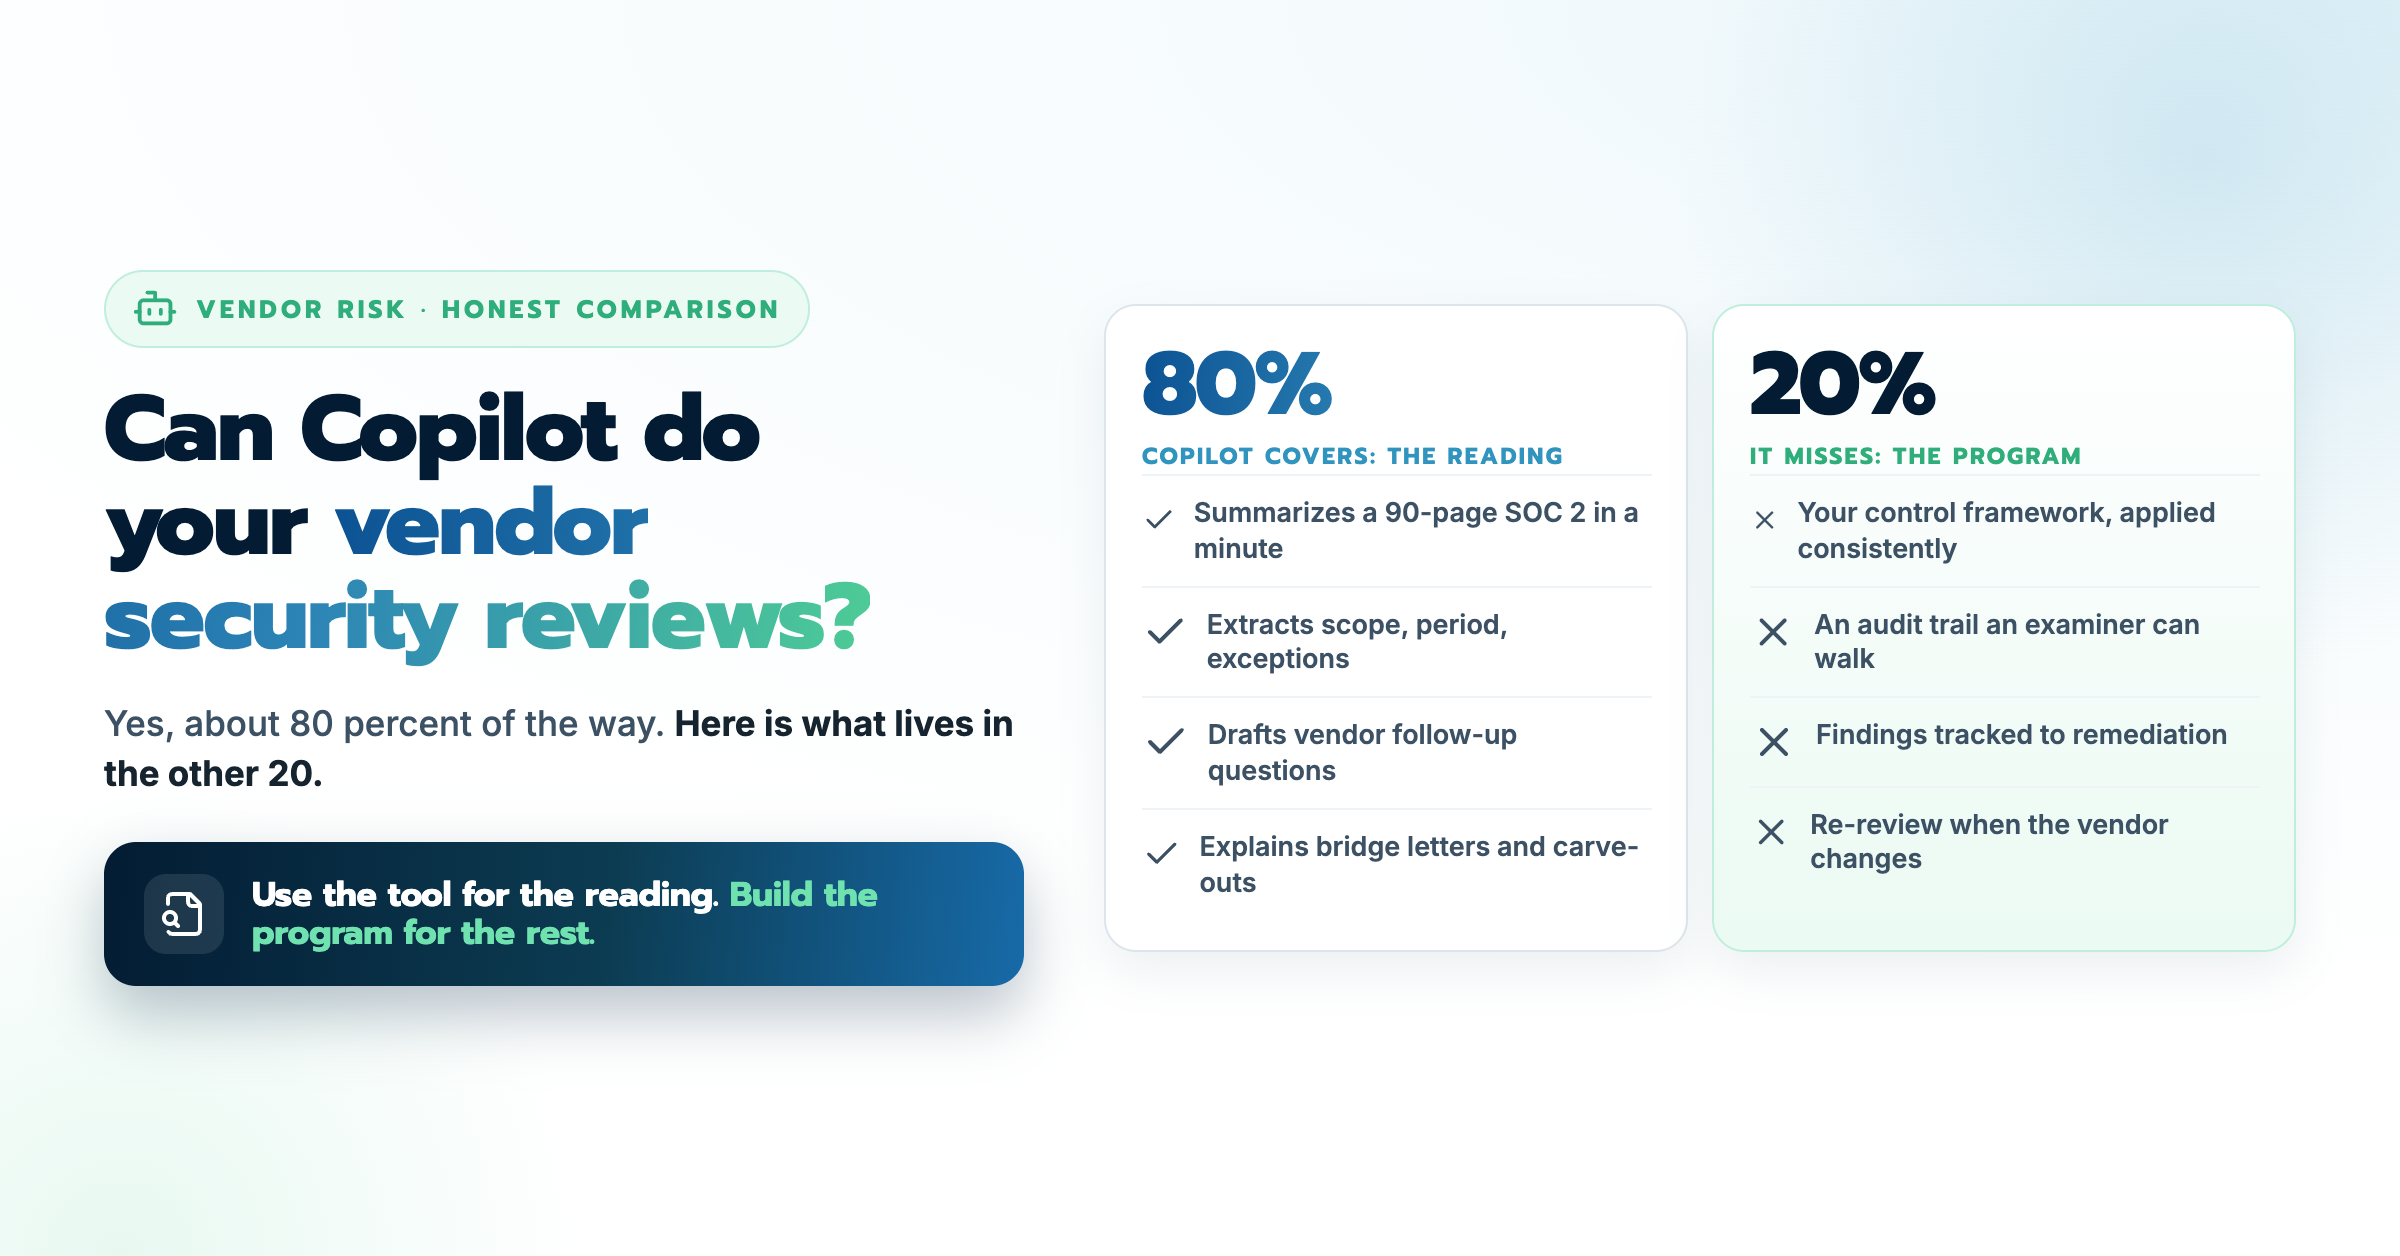
Can Copilot Do Your Vendor Security Reviews? An Honest Answer

A risk leader at a financial institution told us on a call this year, plainly, that Copilot already gets his team about 80 percent of the way through...

Read More

6 min read

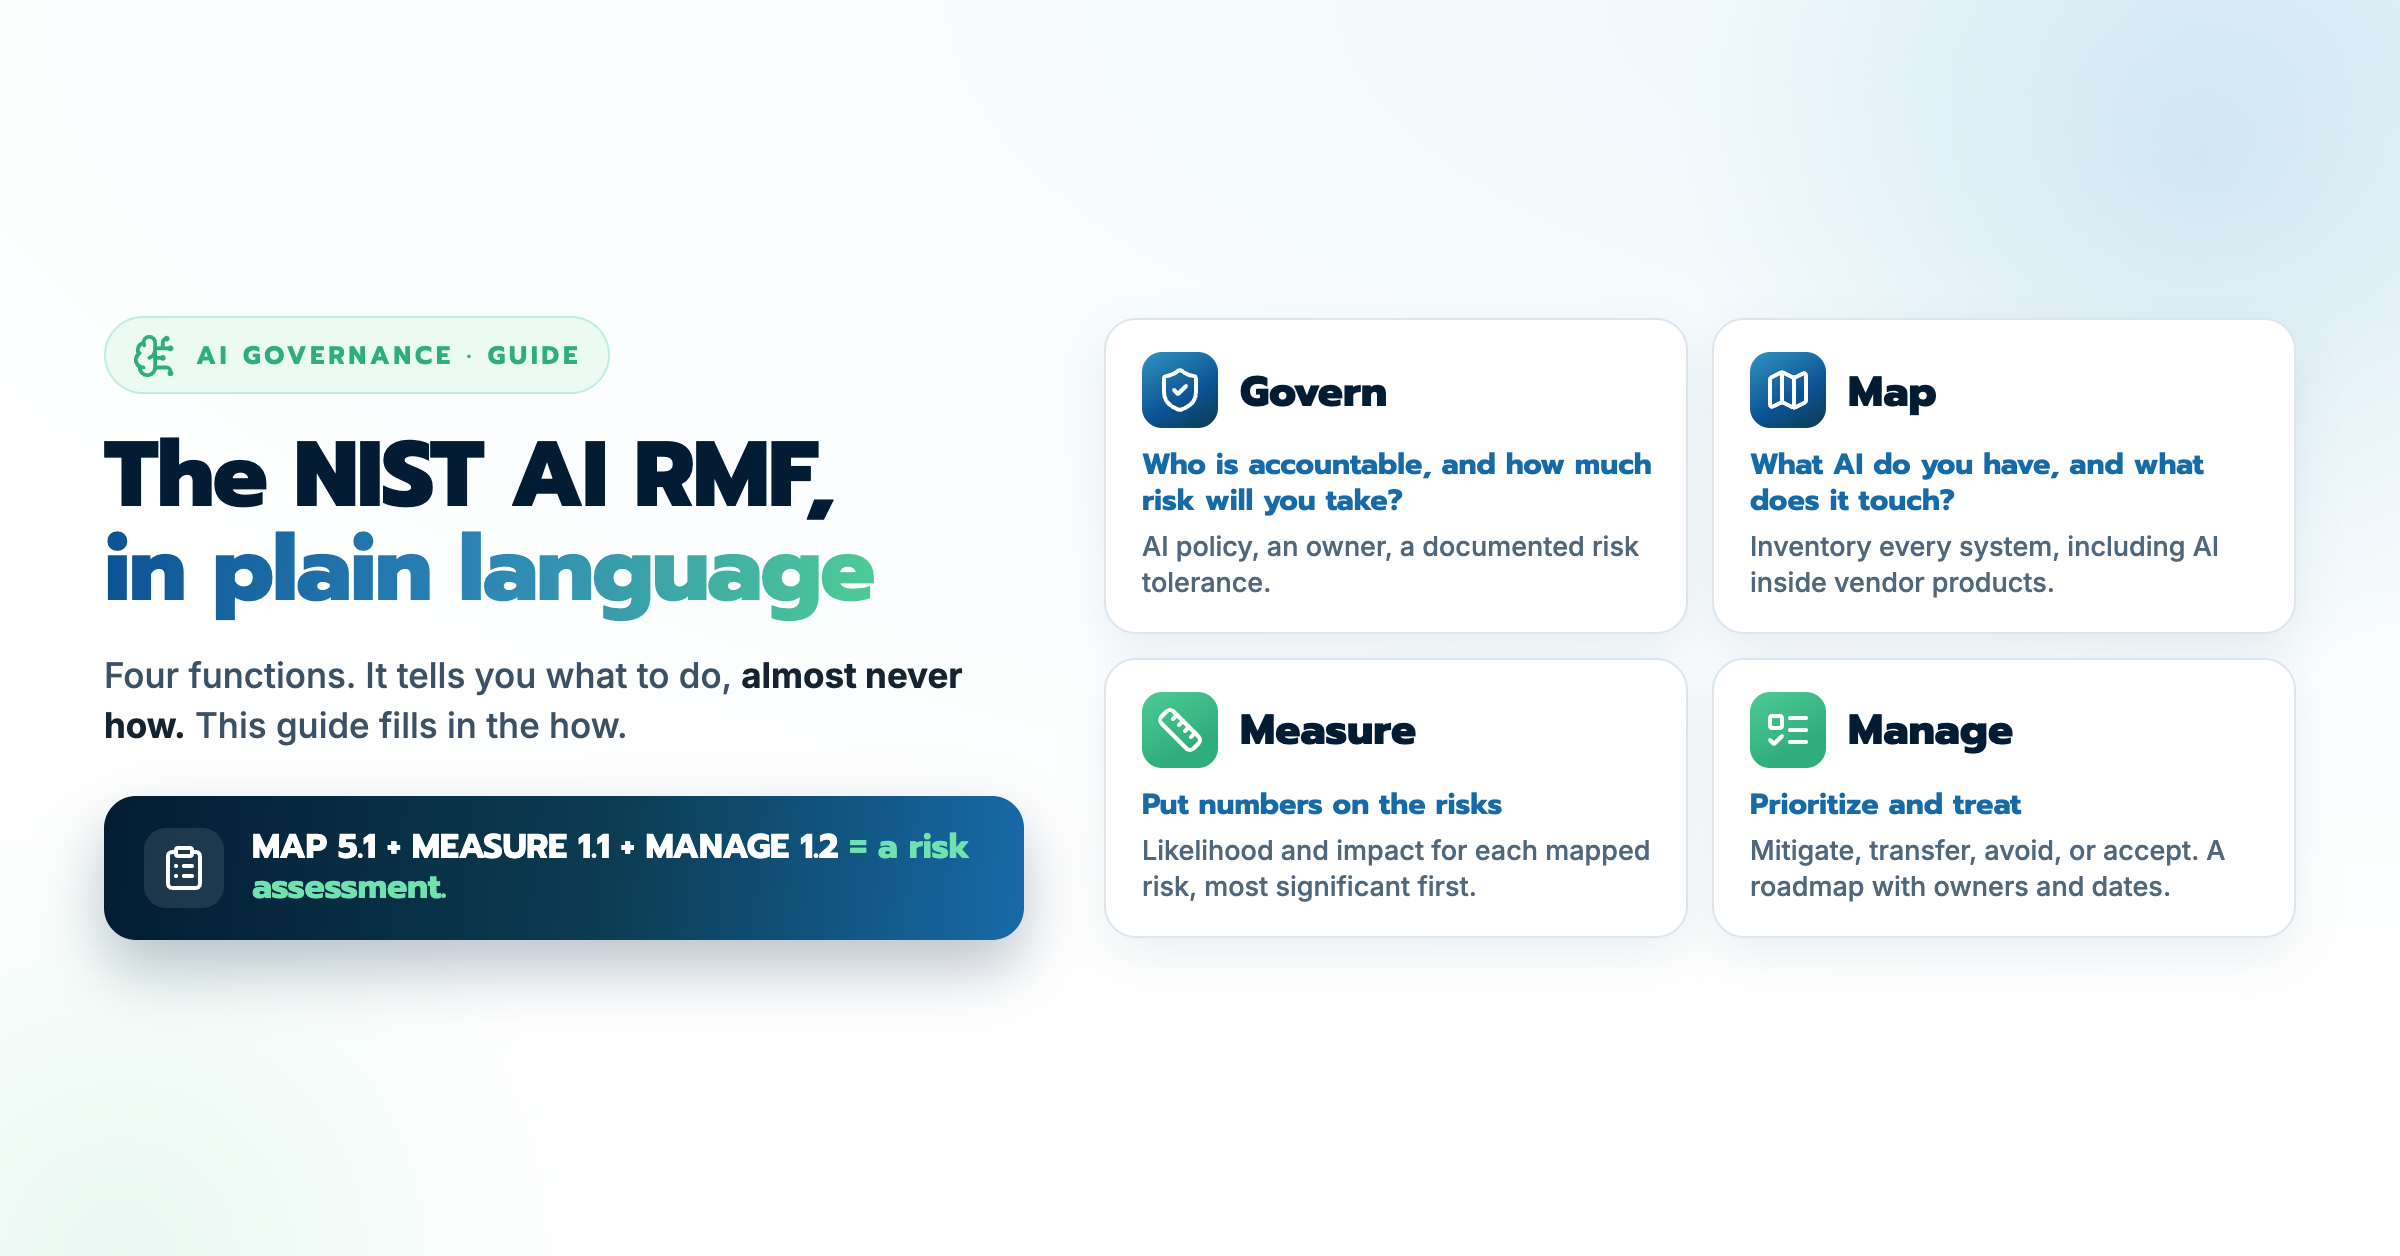
NIST AI RMF for Financial Institutions: A Complete Guide

Financial institutions are adopting AI faster than they are governing it, and the request we now hear on calls is specific: "we need a credible AI...

Read More

4 min read

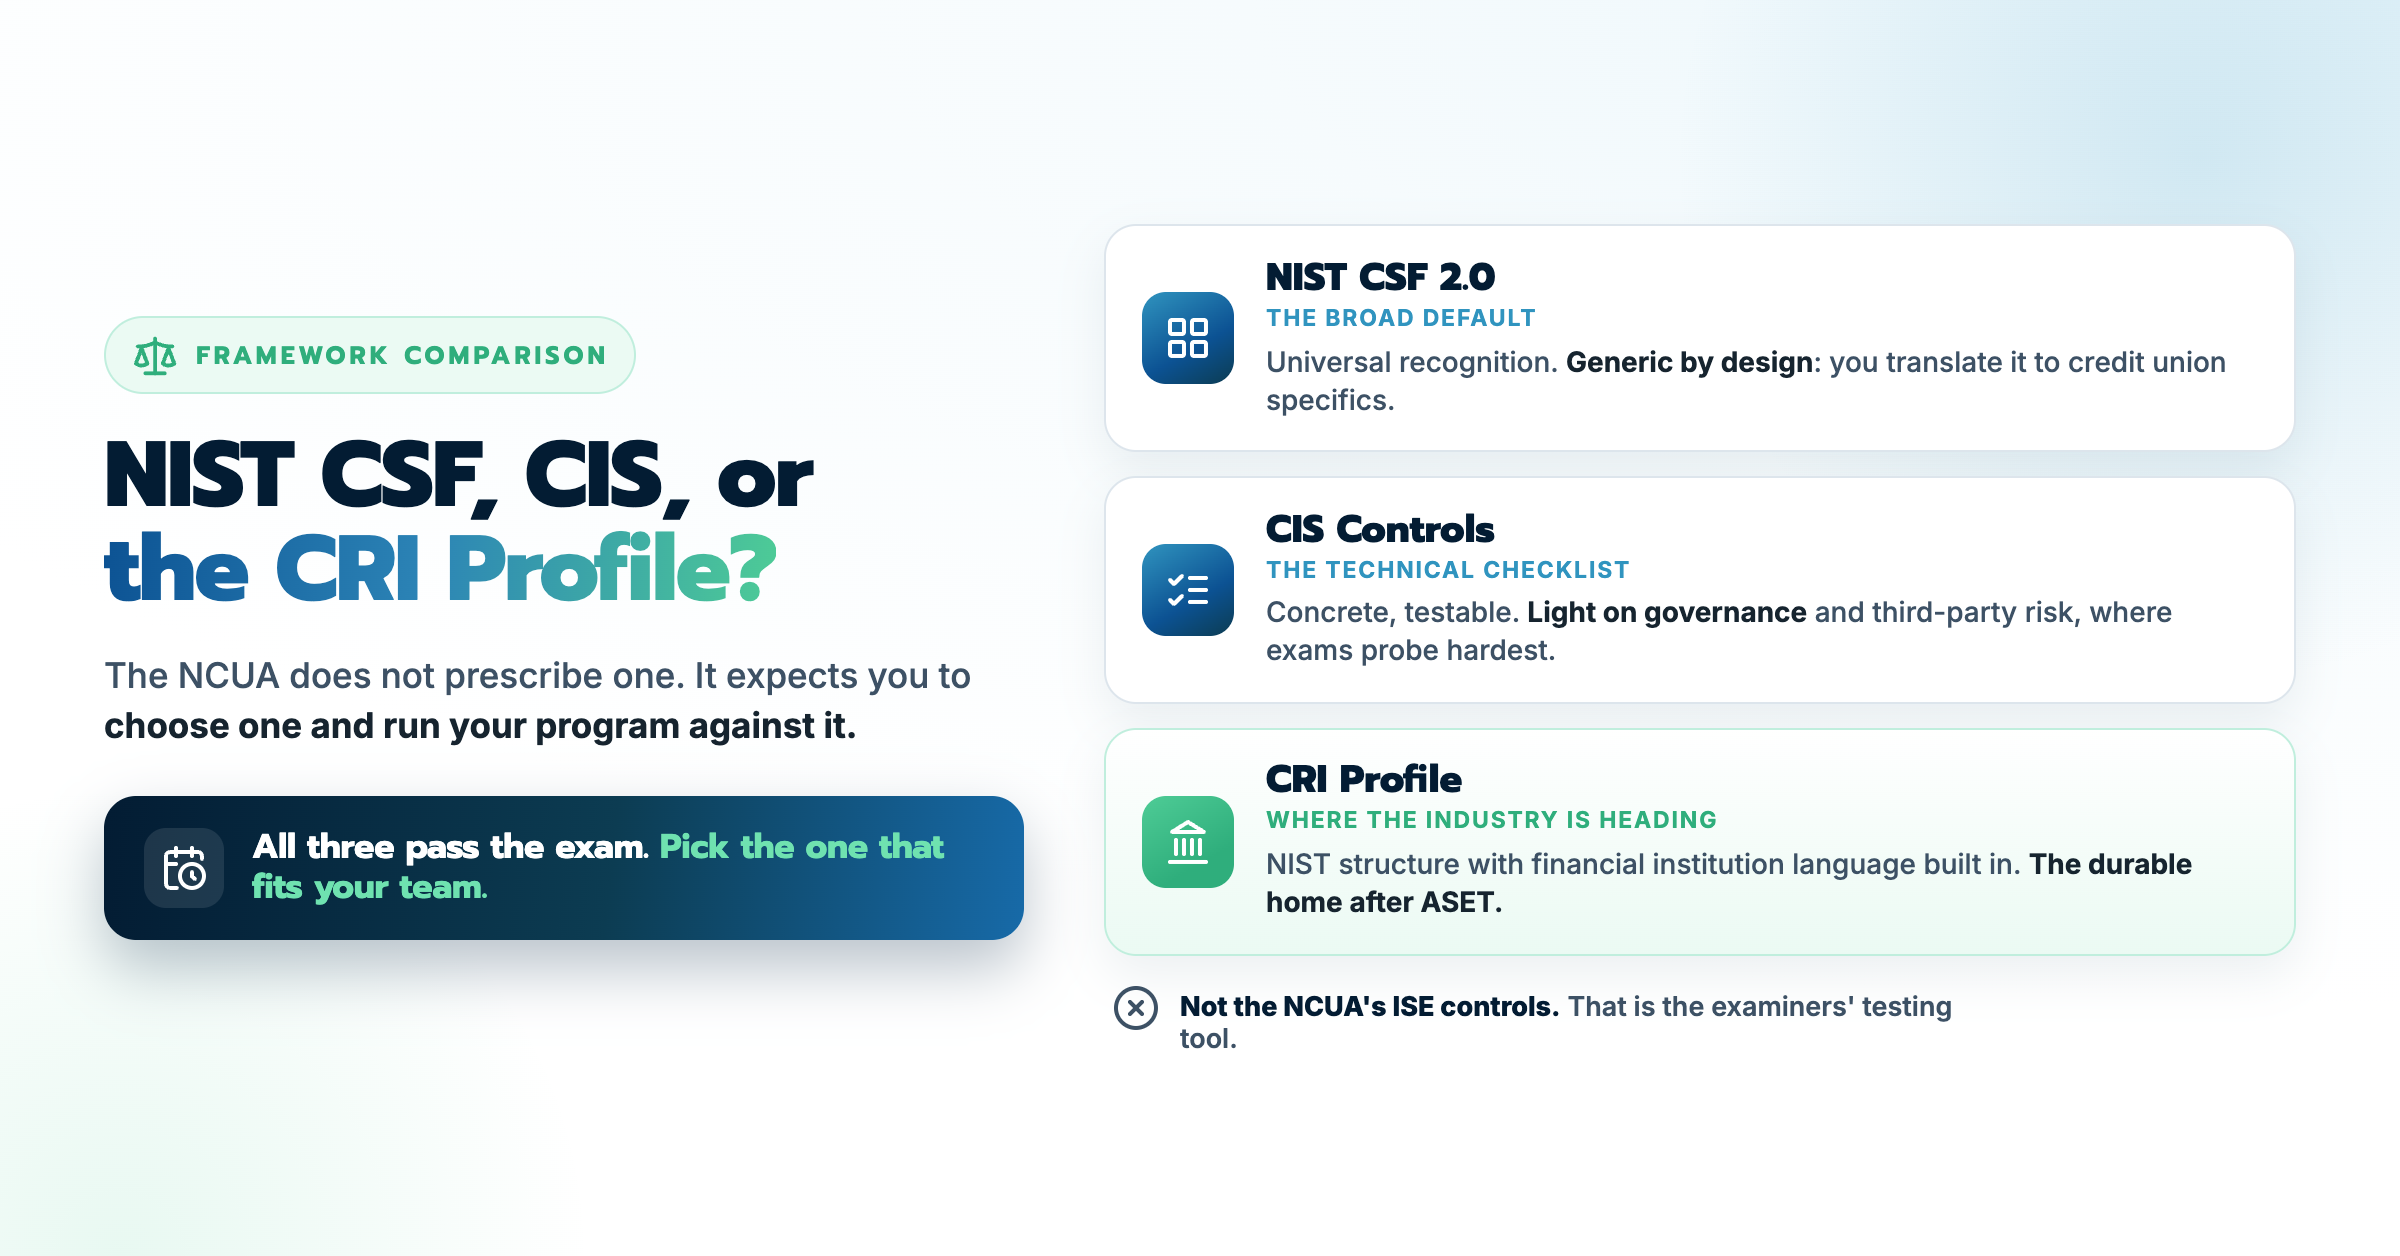
NIST CSF vs CIS vs CRI Profile: Which Framework Should Your Credit Union Choose?

Every credit union security leader eventually asks the same question, usually right before an exam or right after a merger: which framework does the...

Read More

4 min read

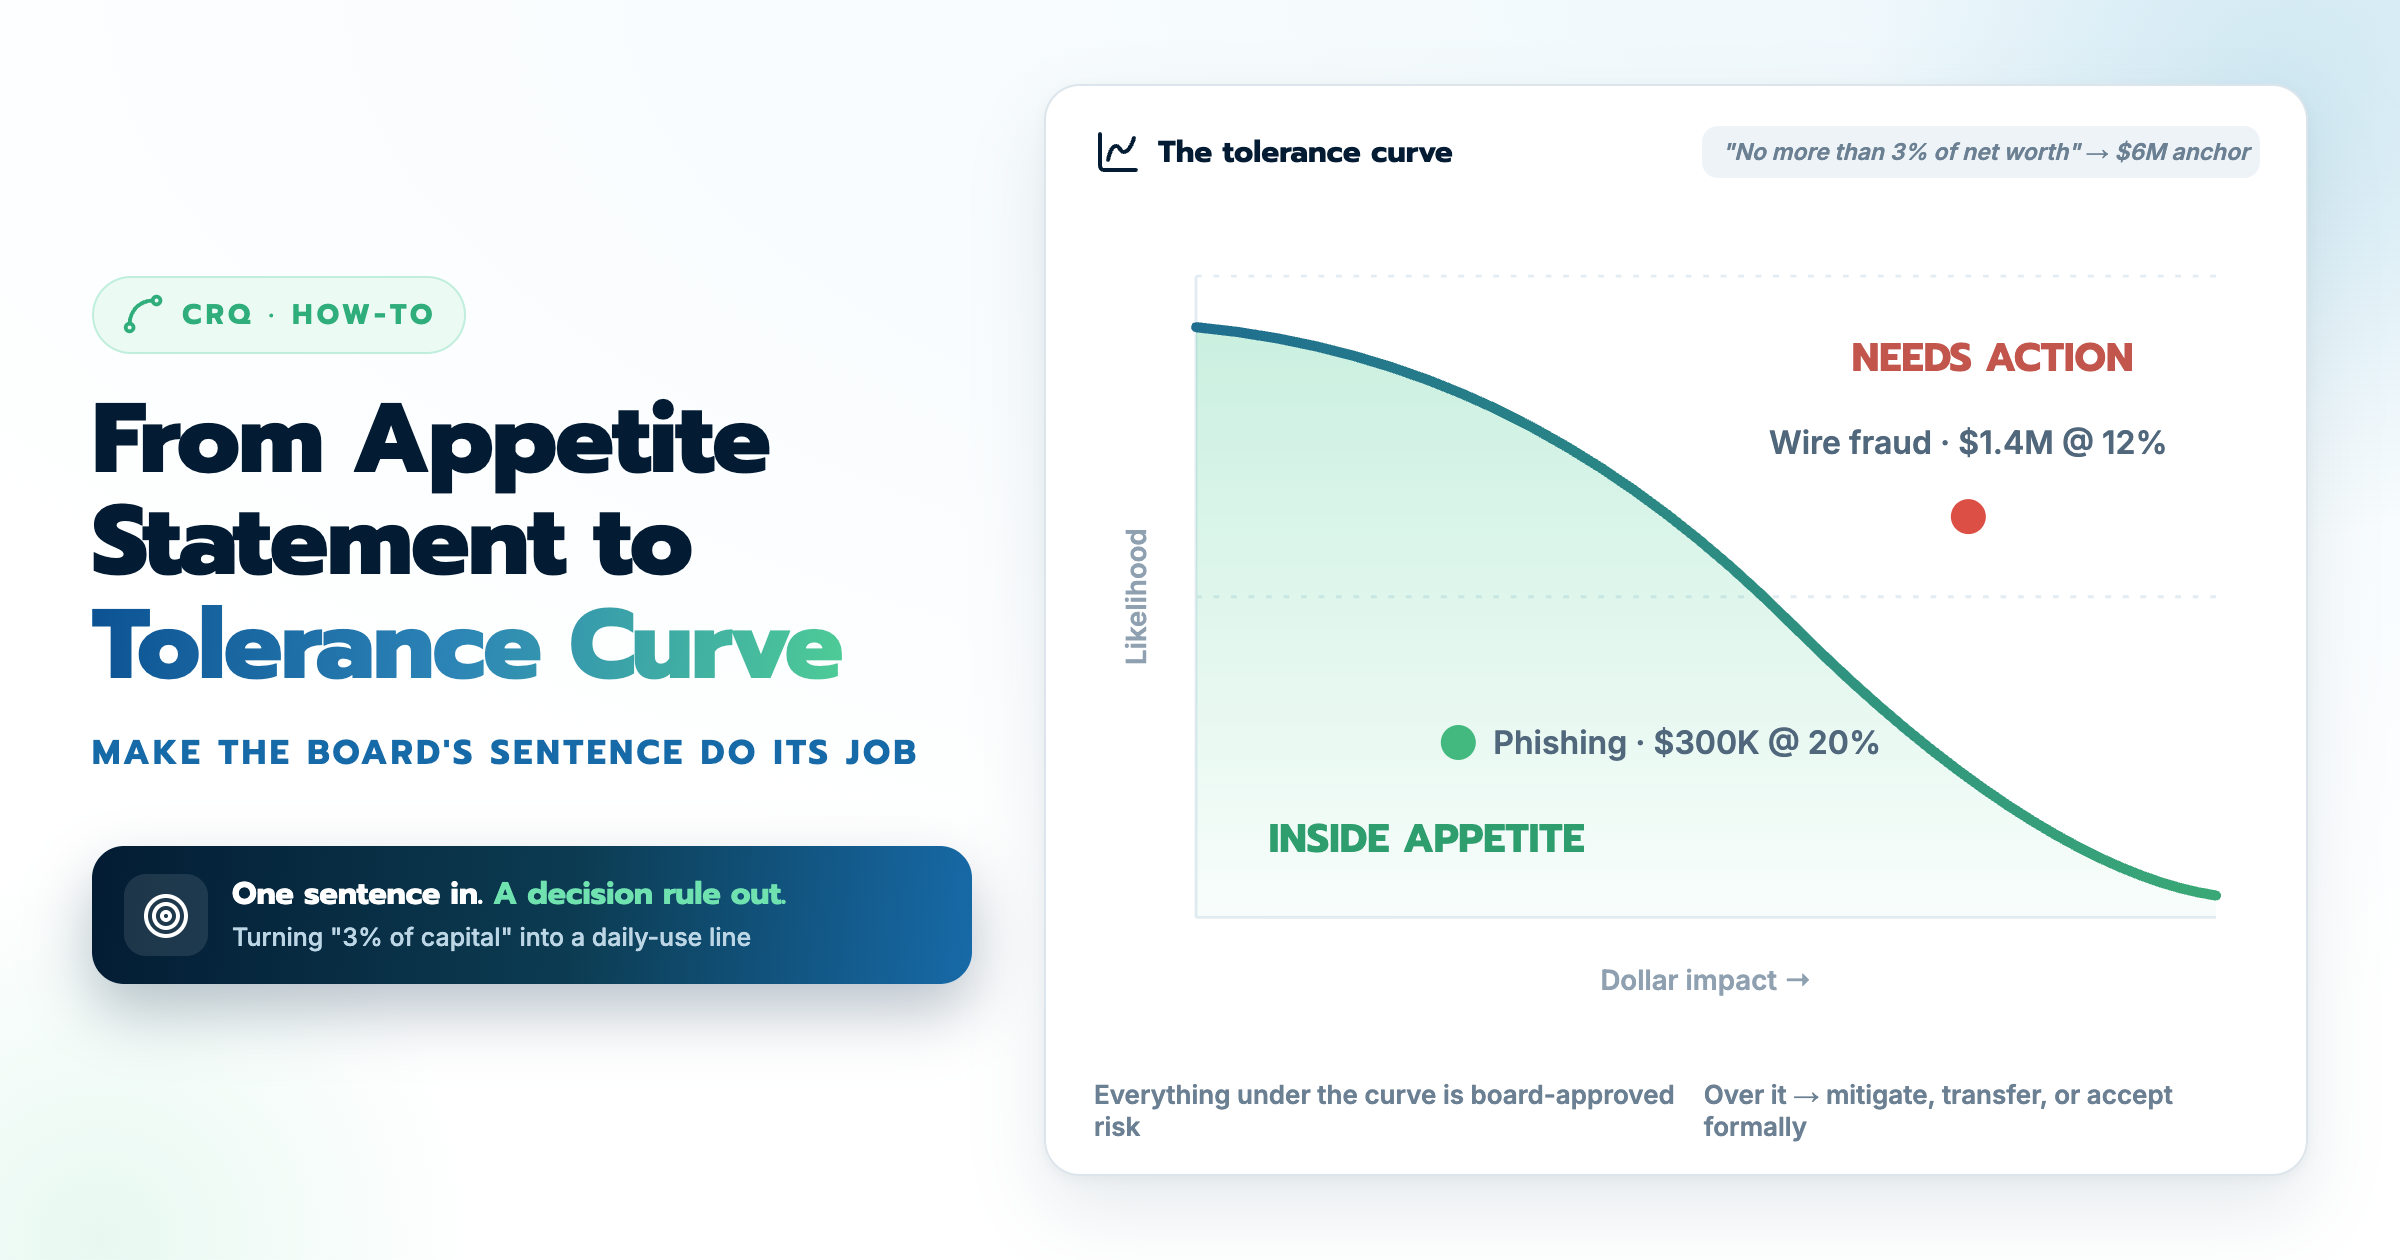
How to Turn a Risk Appetite Statement Into a Usable Curve

Somewhere in your board policy there is a sentence like this: "The credit union will not accept cyber risk exceeding 3 percent of net worth." The...

Read More

5 min read

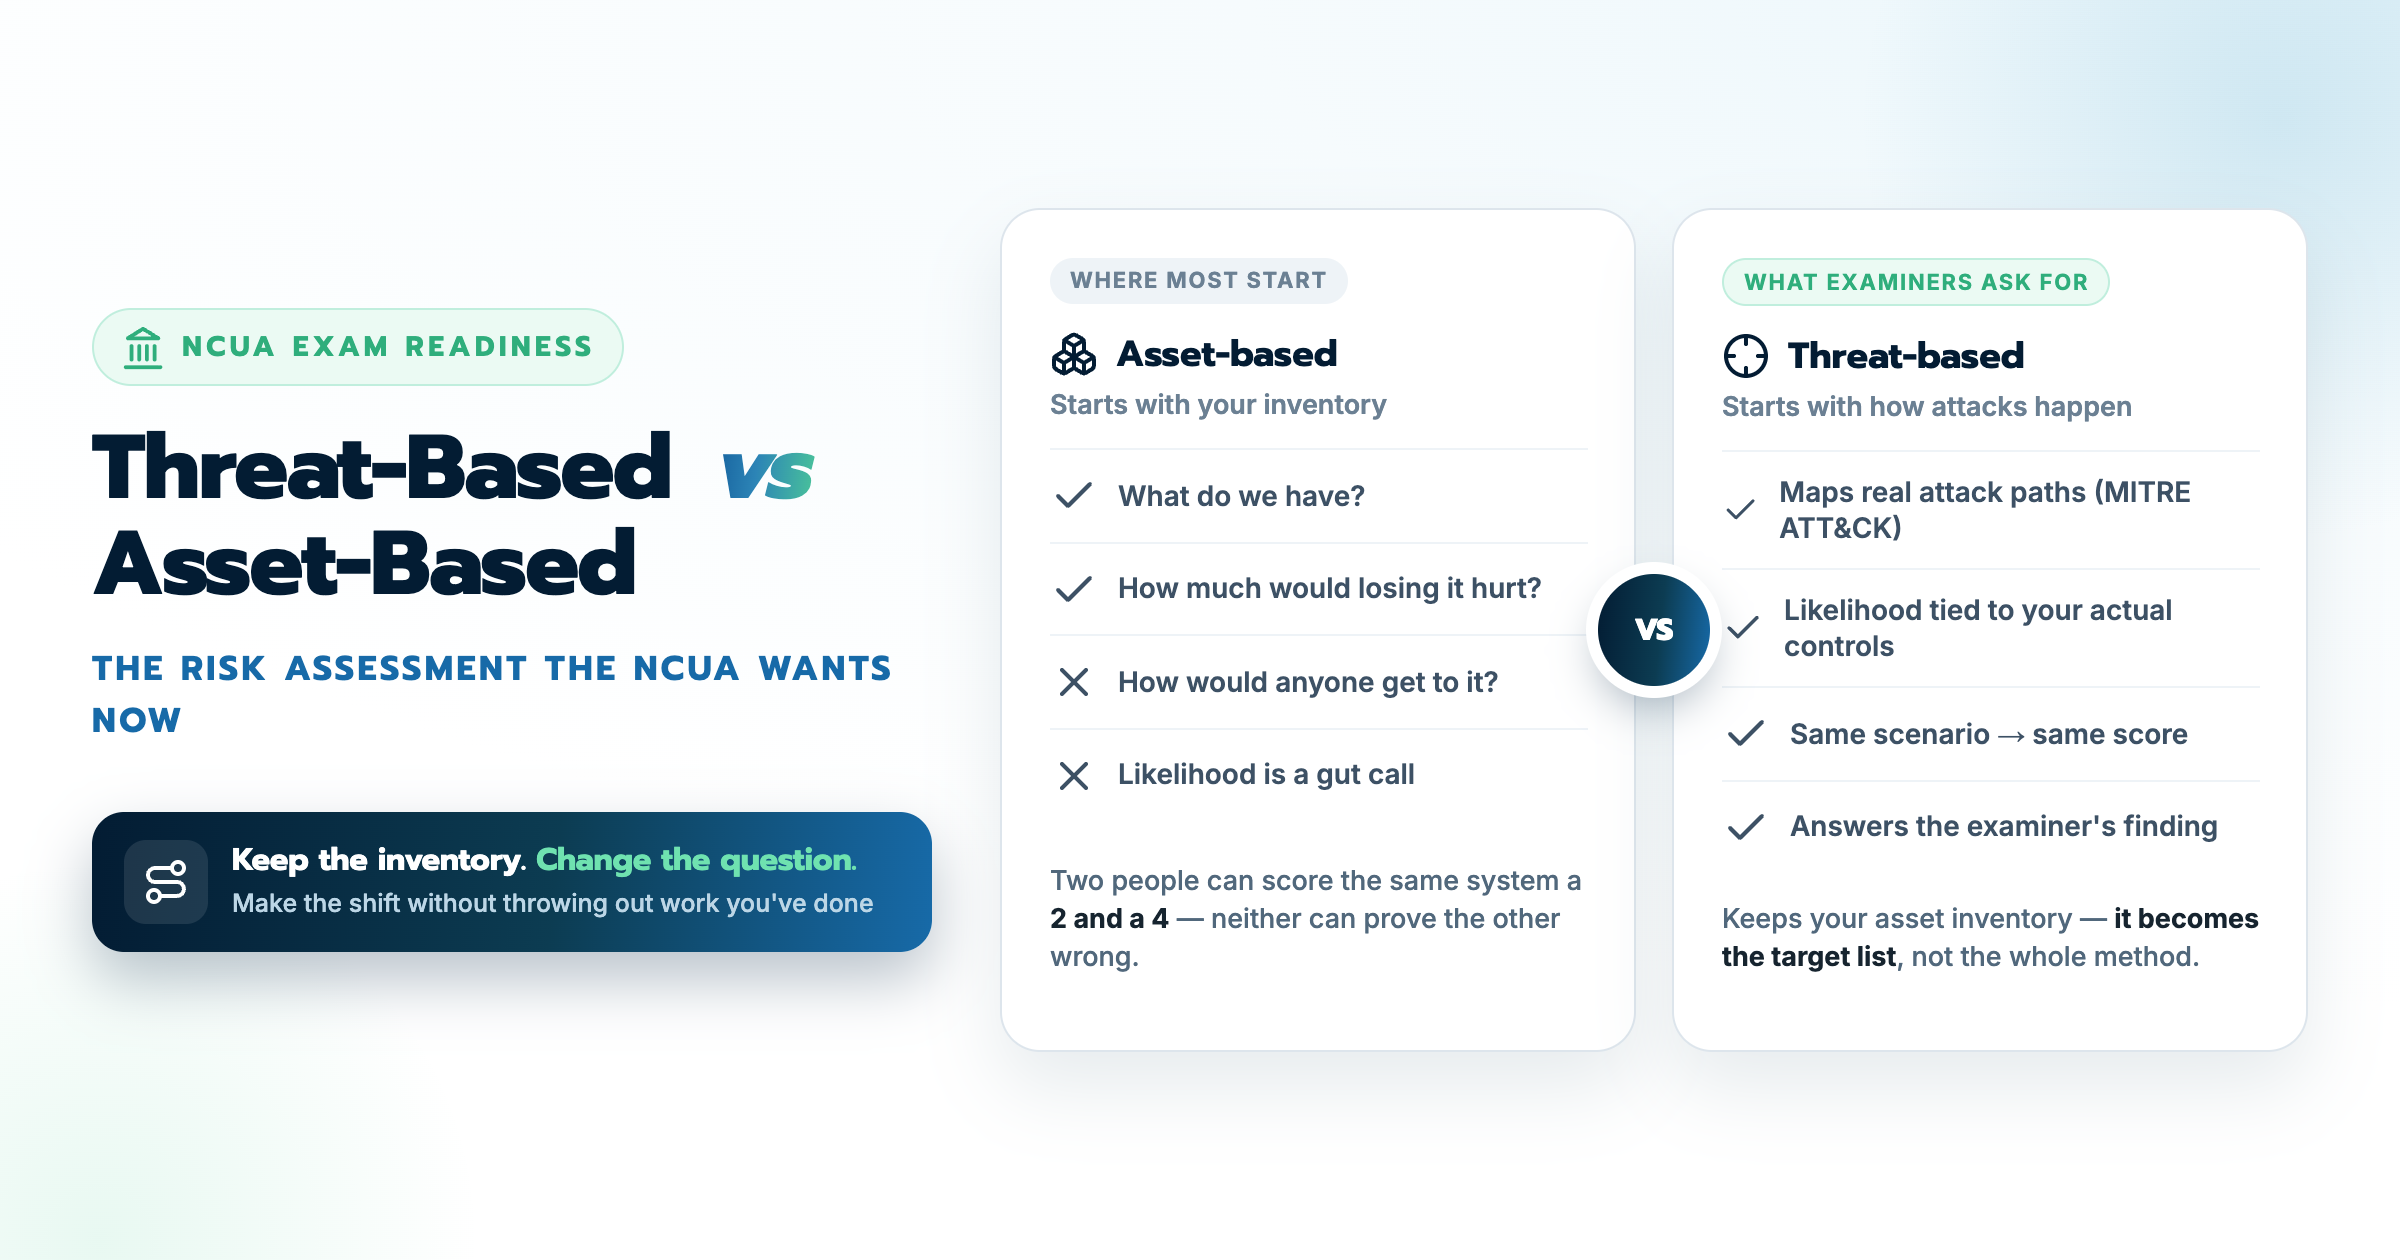
Threat-Based vs Asset-Based Risk Assessment: NCUA View

Pull up your current risk assessment and look at what the rows actually are. For most institutions, they are threats: ransomware, phishing, insider...

Read More

5 min read

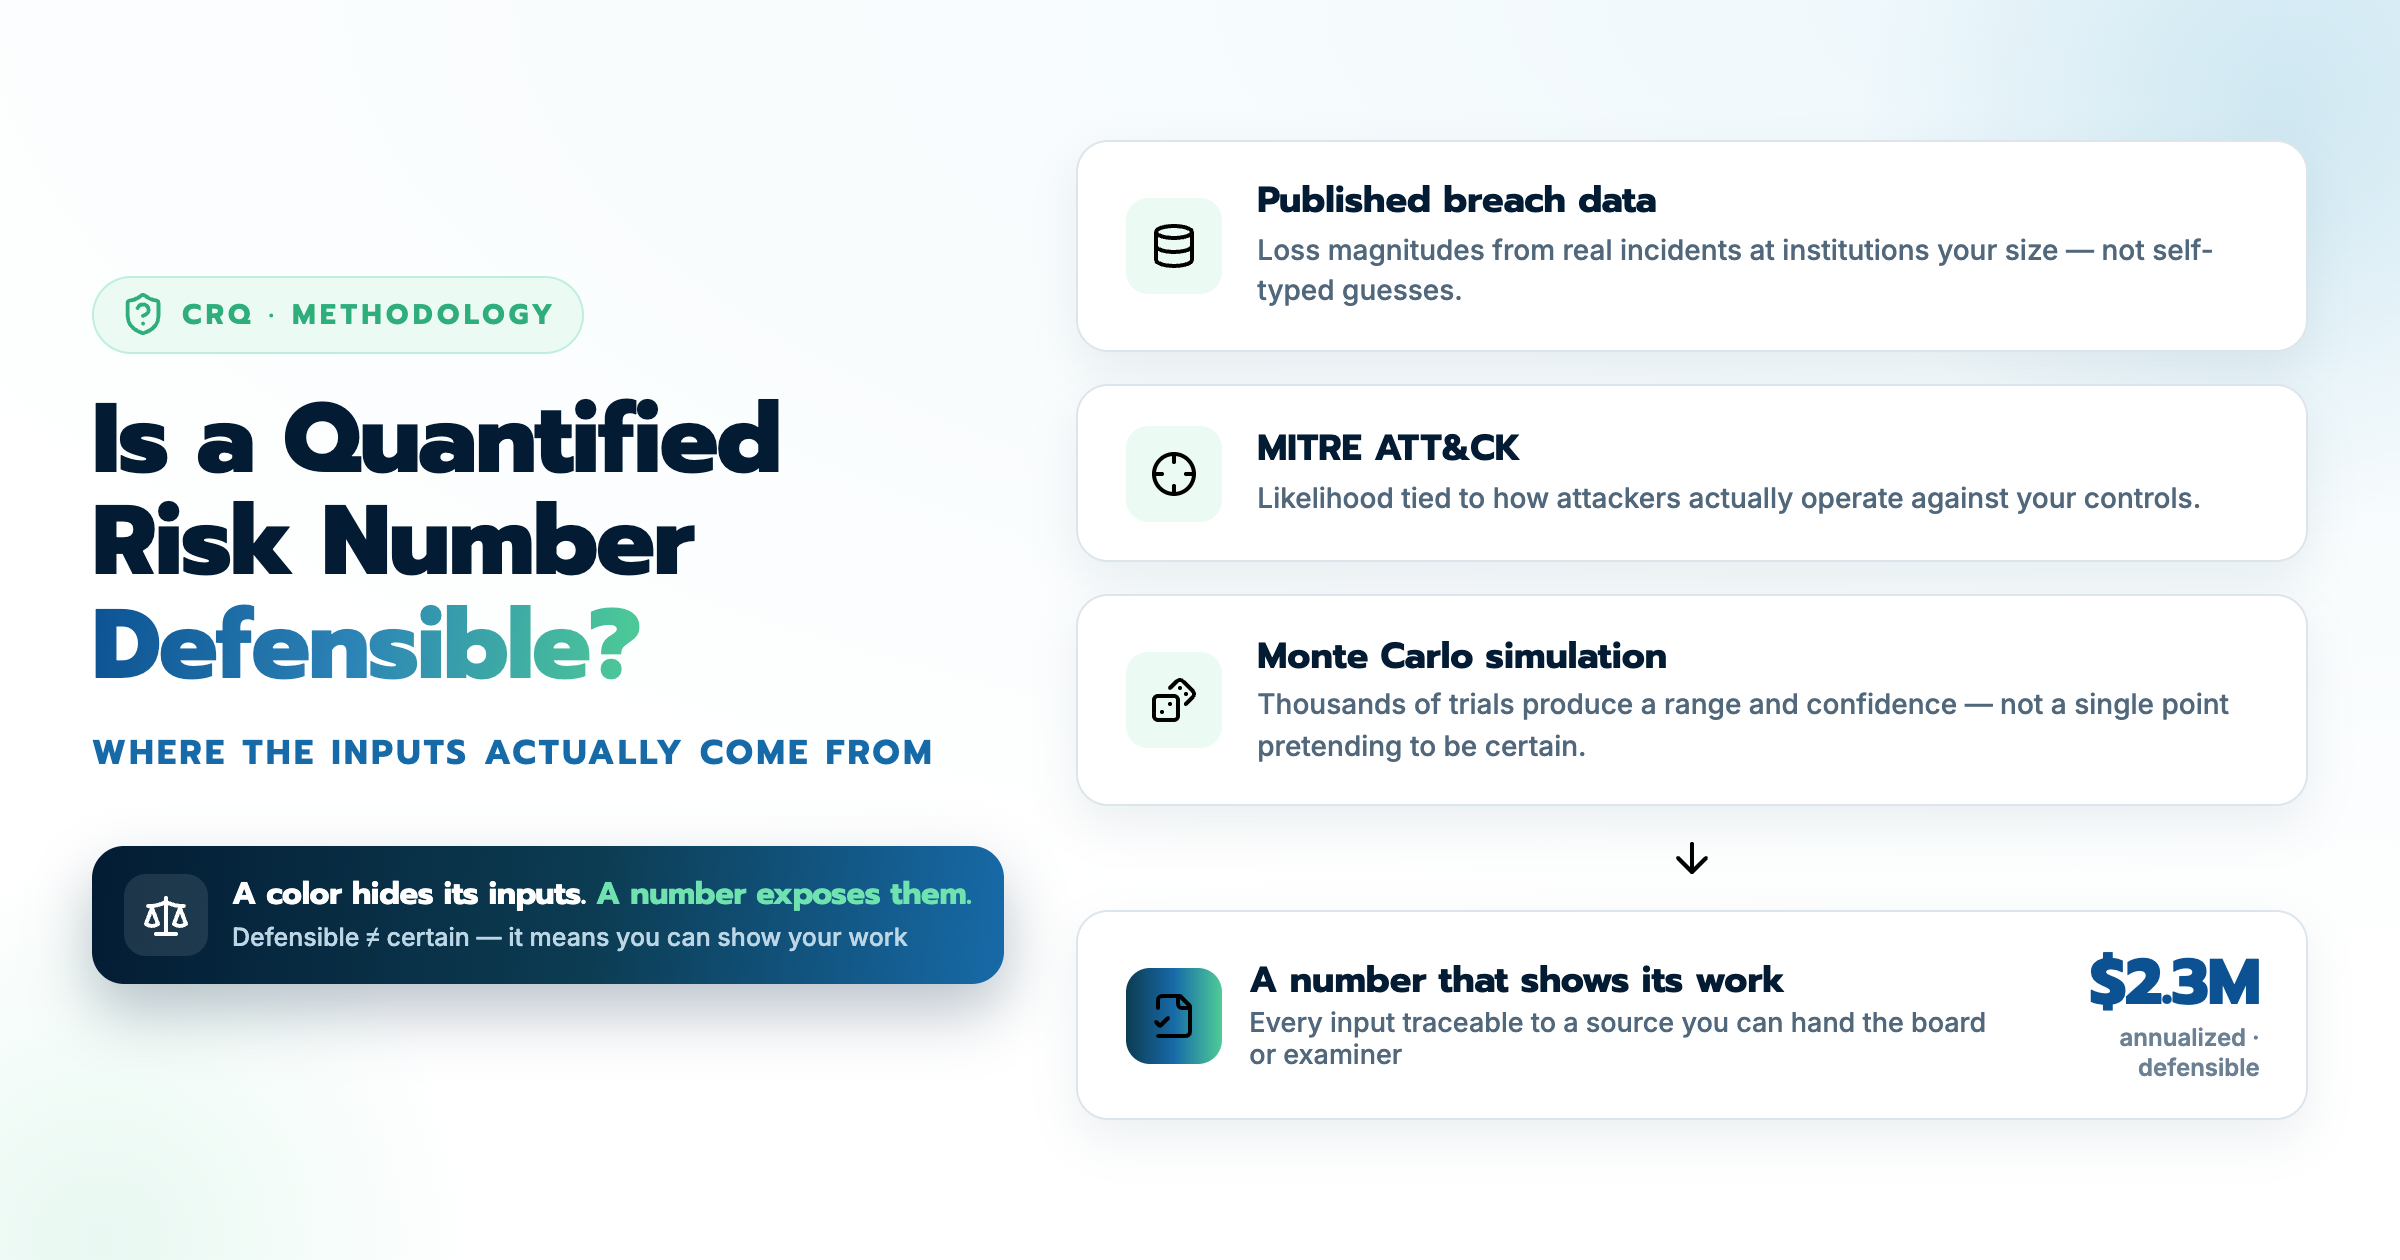
Is a Quantified Cyber Risk Number Defensible? The Inputs

The most common objection to cyber risk quantification does not come from boards. It comes from security leaders, and it goes like this: the number...

Read More