Skip to the main content.
Watch Demo Meet With Our Team
Rivial’s Cybersecurity blog

The Savvy CISO

Cybersecurity management insights, tips, and trends for security leaders, CISOs, vCISOs, and MSSPs who want to work smarter, not harder.

Cyber Risk Quantification

4 min read

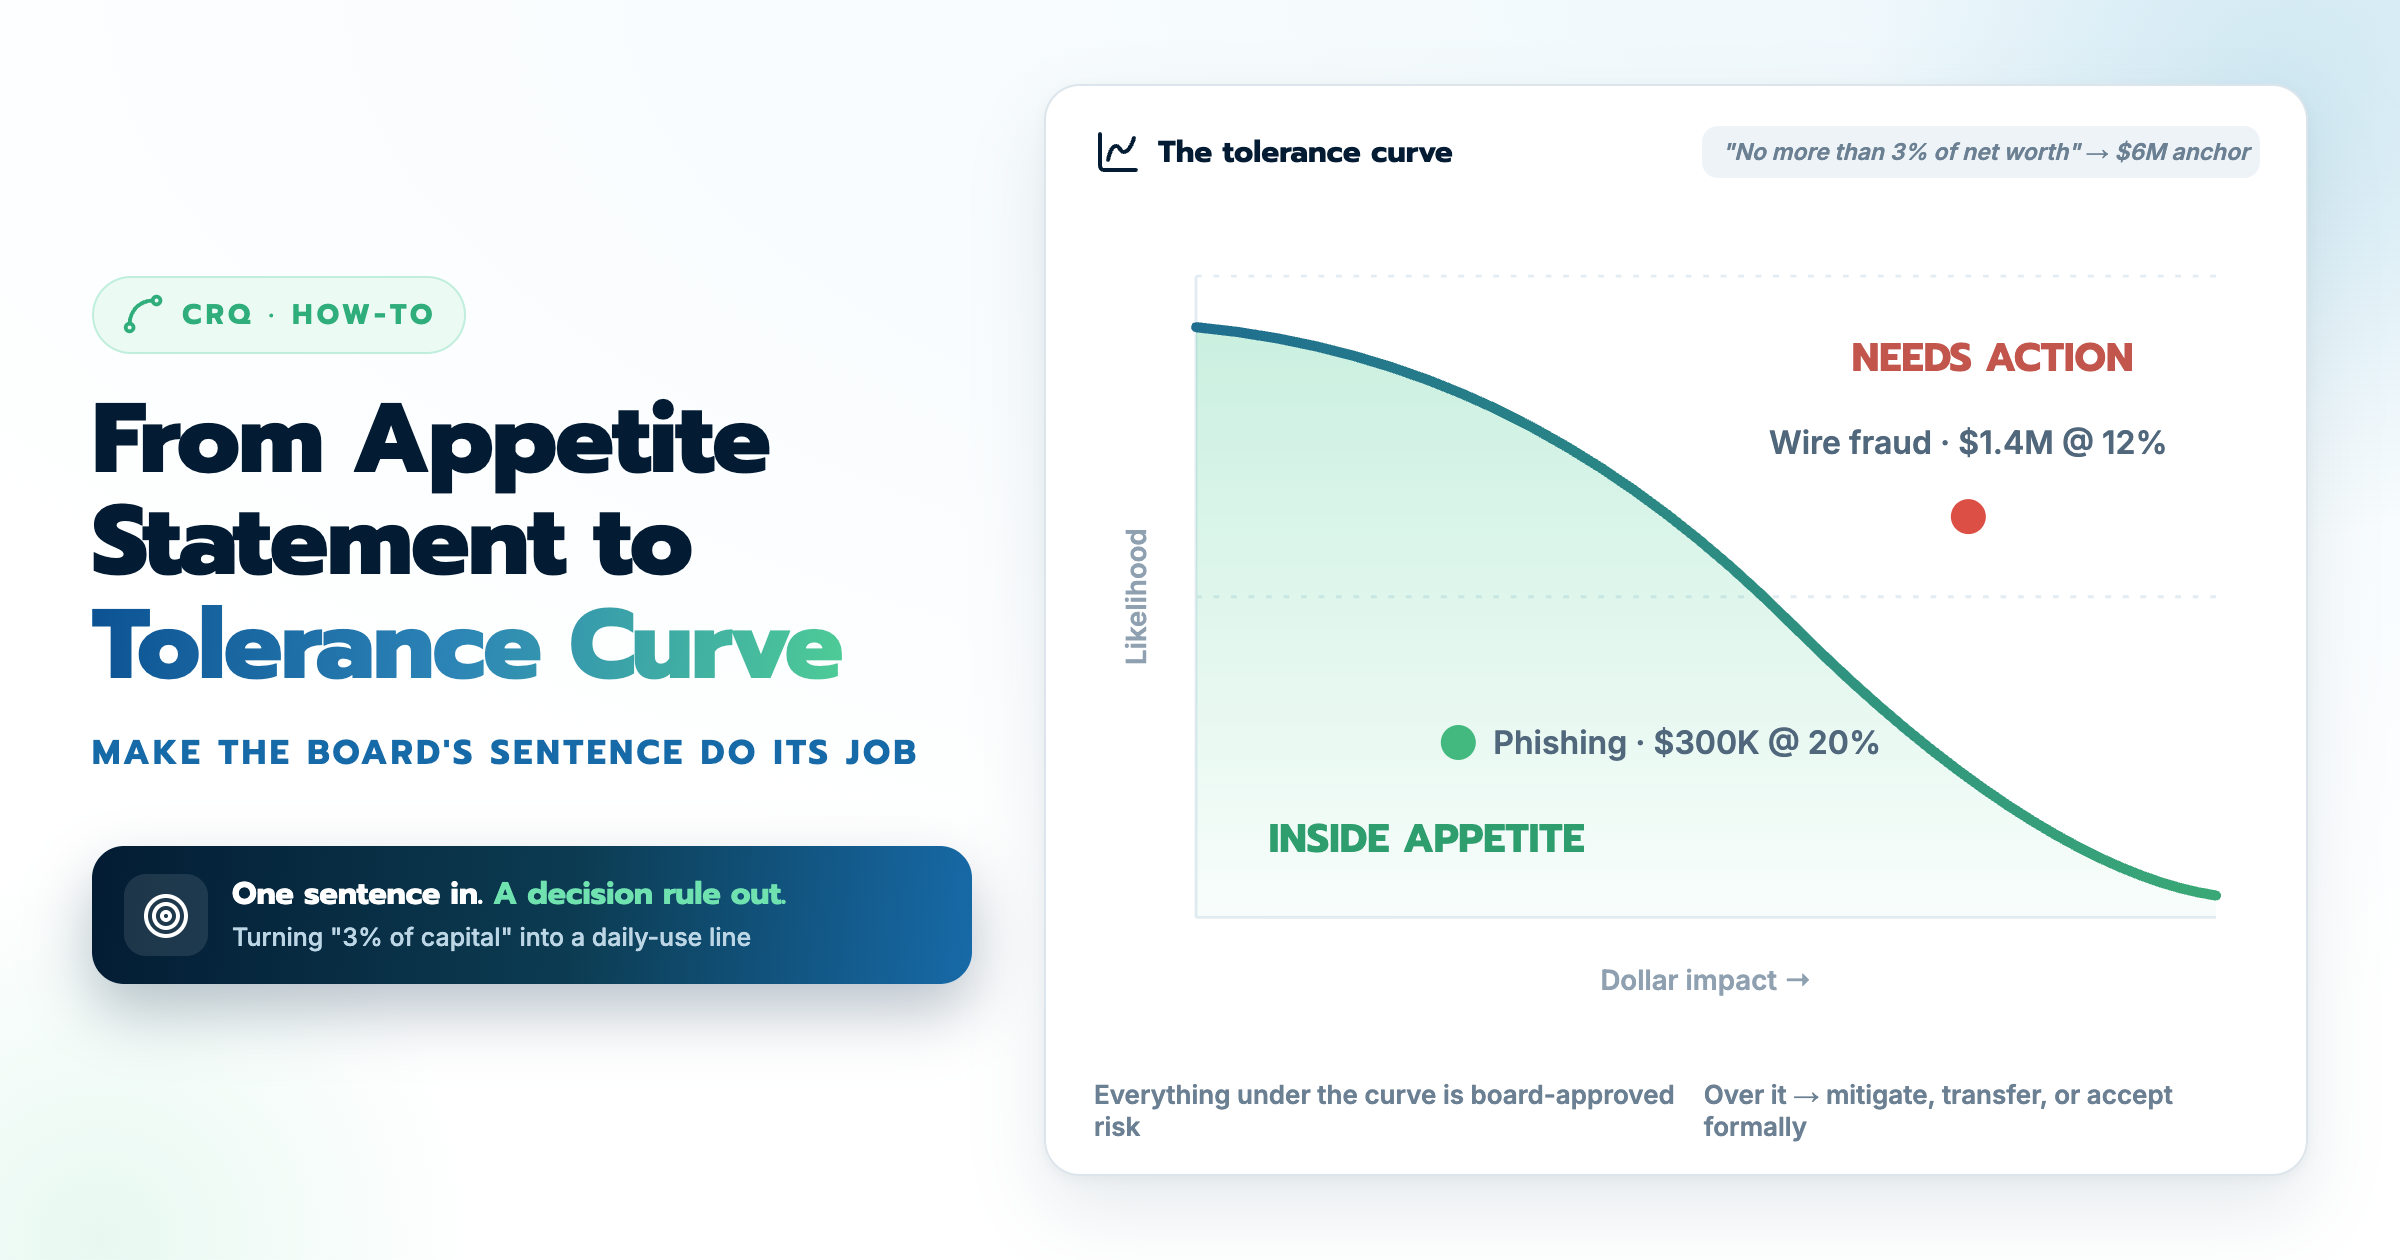
How to Turn a Risk Appetite Statement Into a Usable Curve

Somewhere in your board policy there is a sentence like this: "The credit union will not accept cyber risk exceeding 3 percent of net worth." The...
Read More

5 min read

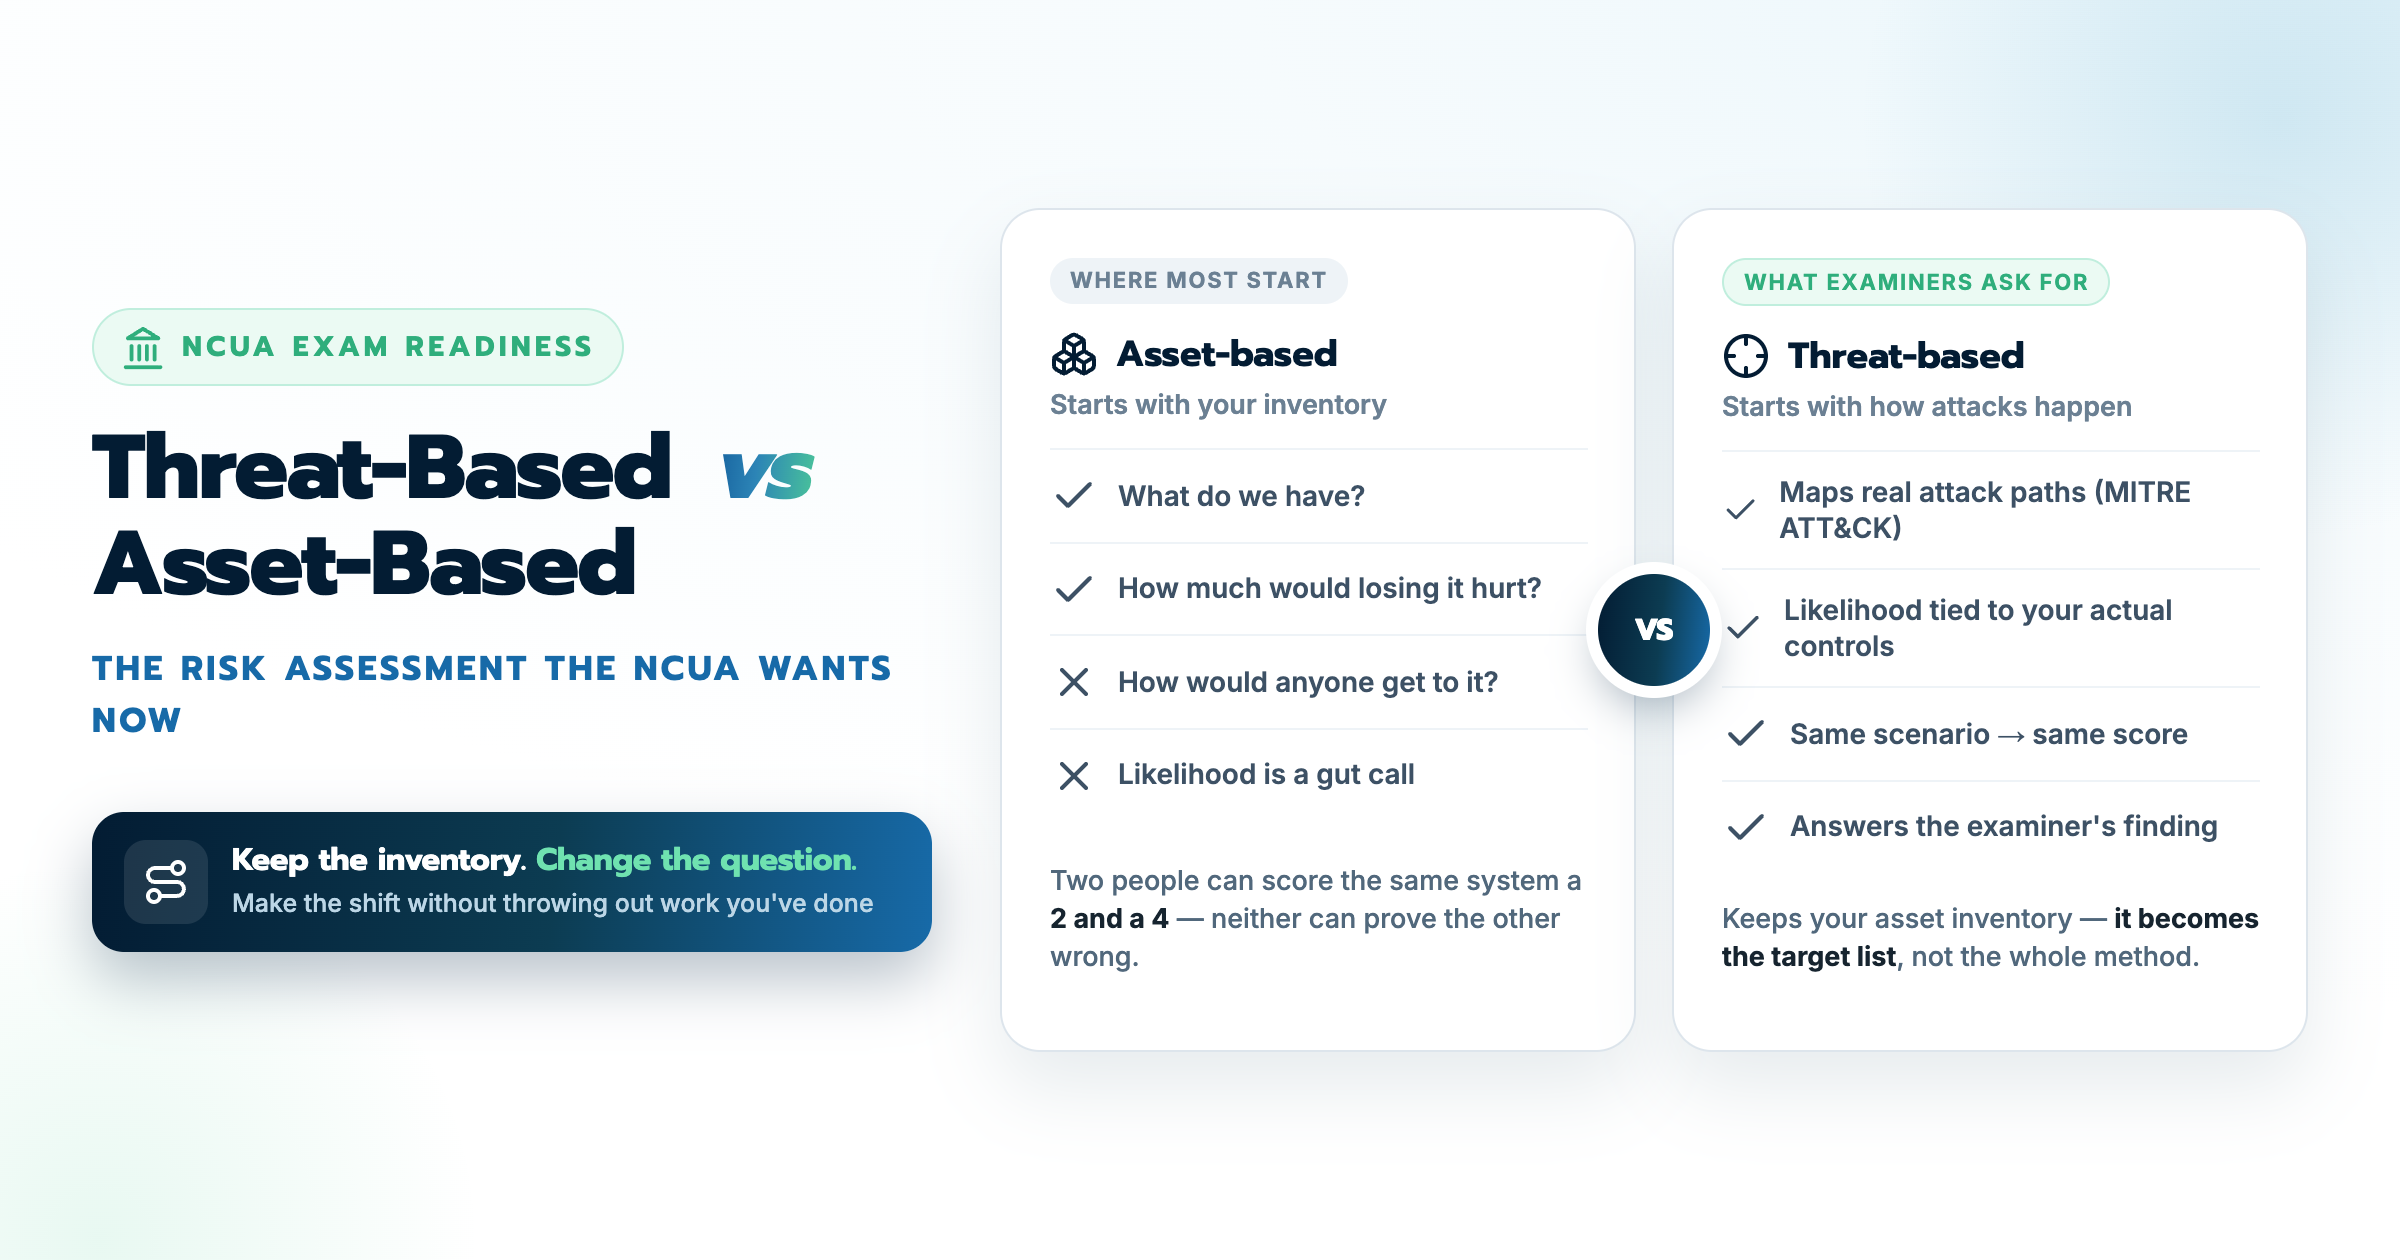
Threat-Based vs Asset-Based Risk Assessment: NCUA View

Pull up your current risk assessment and look at what the rows actually are. For most institutions, they are threats: ransomware, phishing, insider...

Read More

5 min read

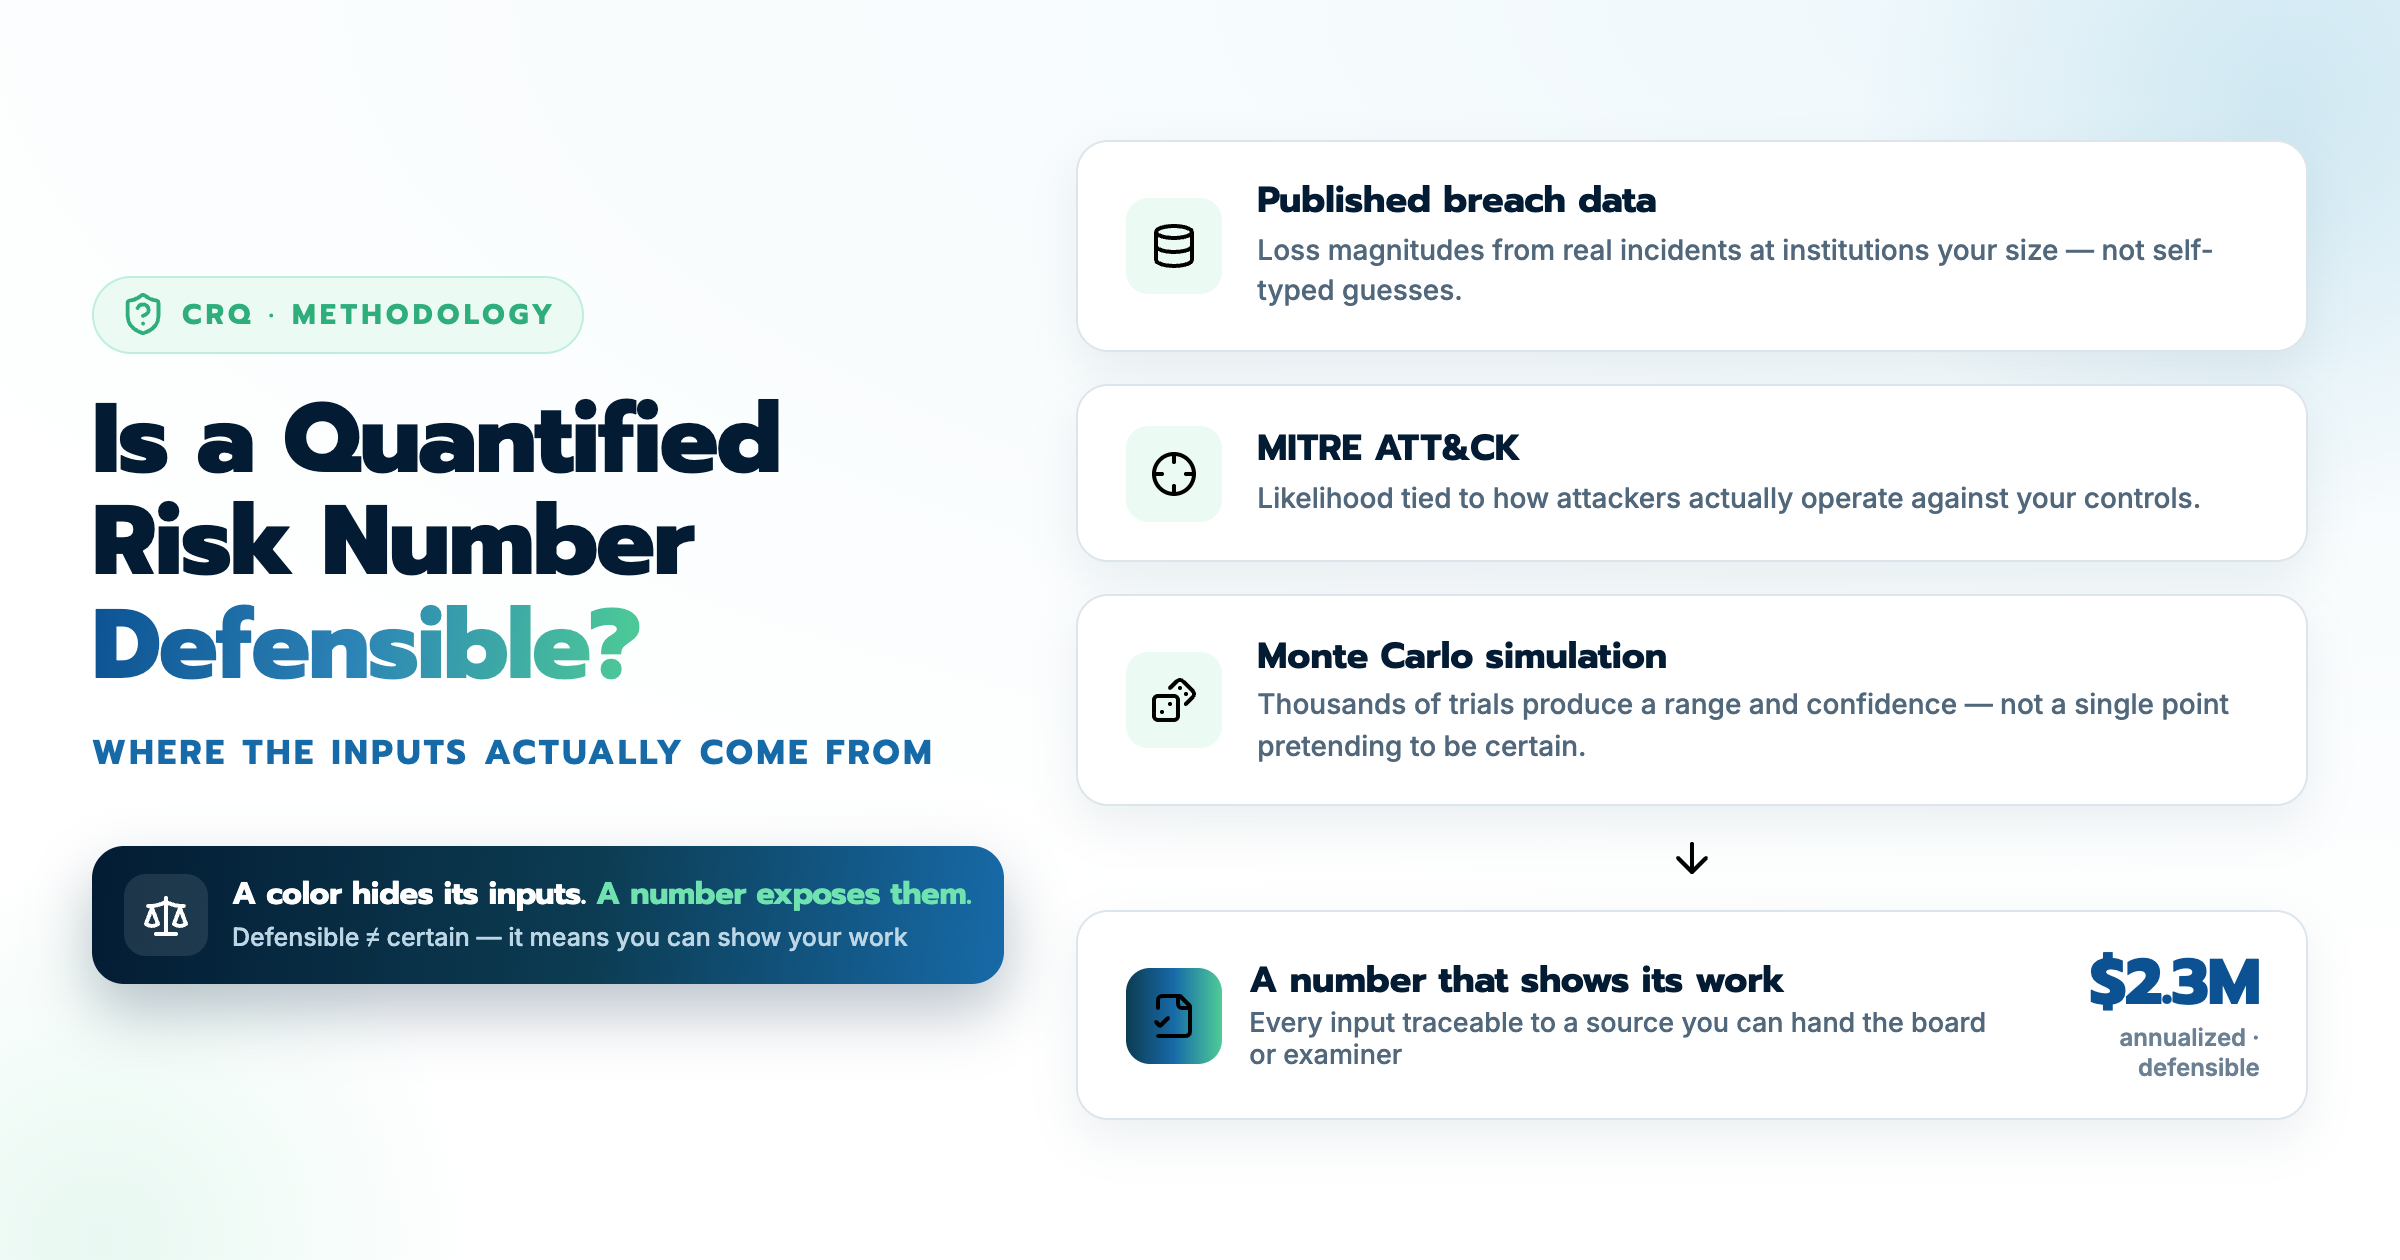
Is a Quantified Cyber Risk Number Defensible? The Inputs

The most common objection to cyber risk quantification does not come from boards. It comes from security leaders, and it goes like this: the number...

Read More

4 min read

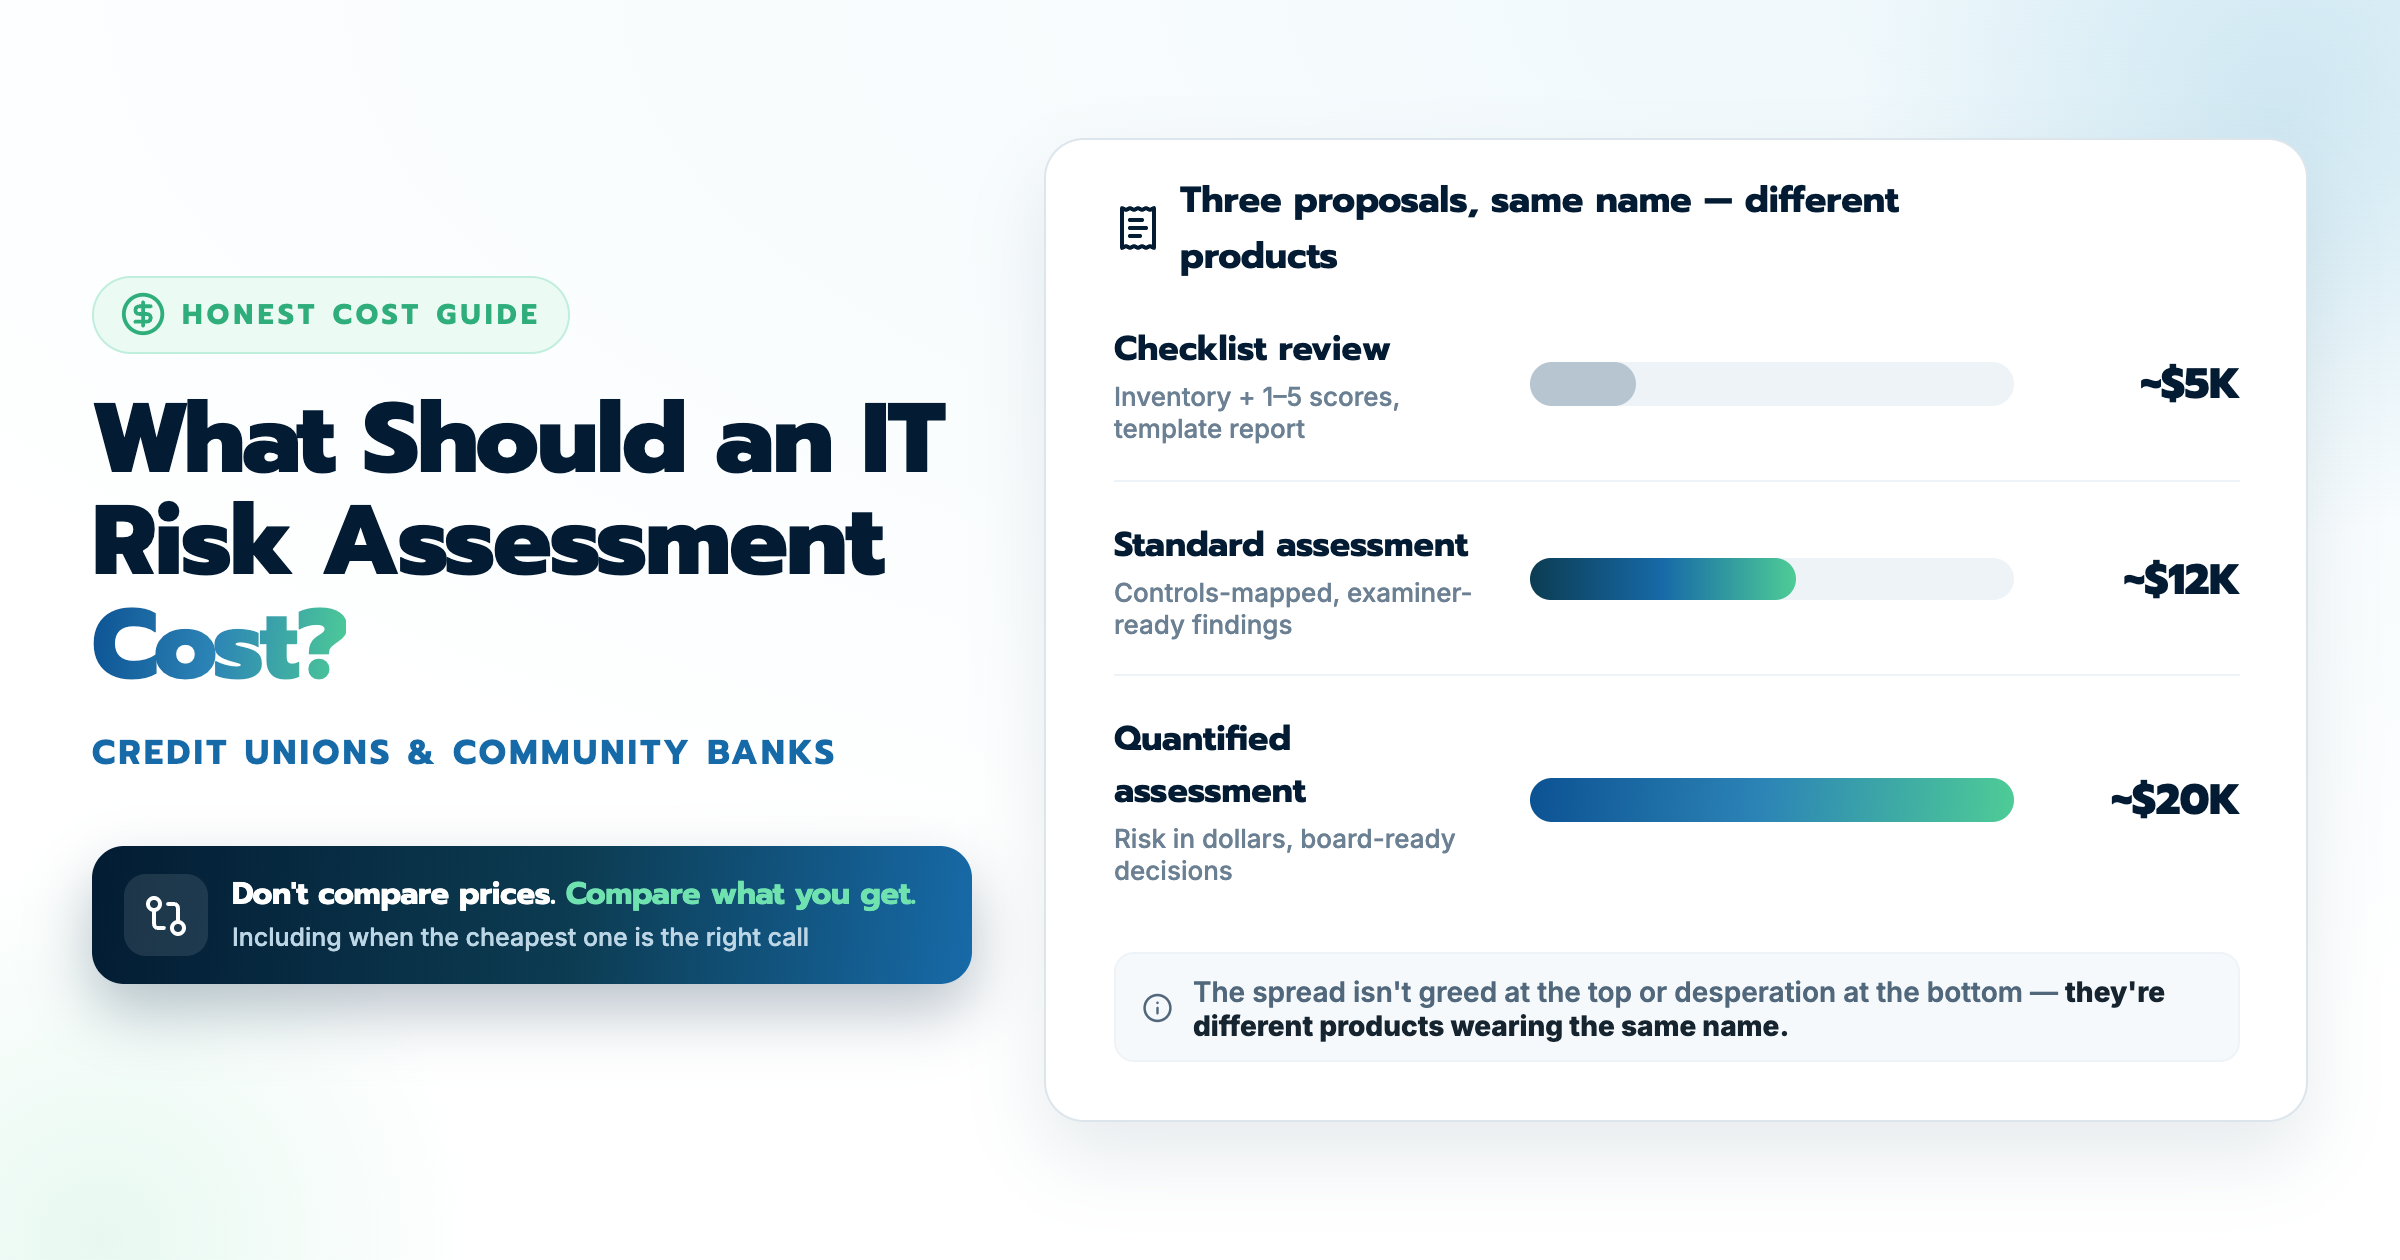
What Should a Credit Union IT Risk Assessment Cost?

You have three proposals on your desk and the numbers are thousands of dollars apart for what each vendor calls the same thing: an IT risk...

Read More

8 min read

Risk in Dollars, Not Colors: A Complete Guide to Board Reporting

A security officer at a credit union told me that in his entire time at the institution, they had never once talked about risk in numbers. Colors,...

Read More