4 min read
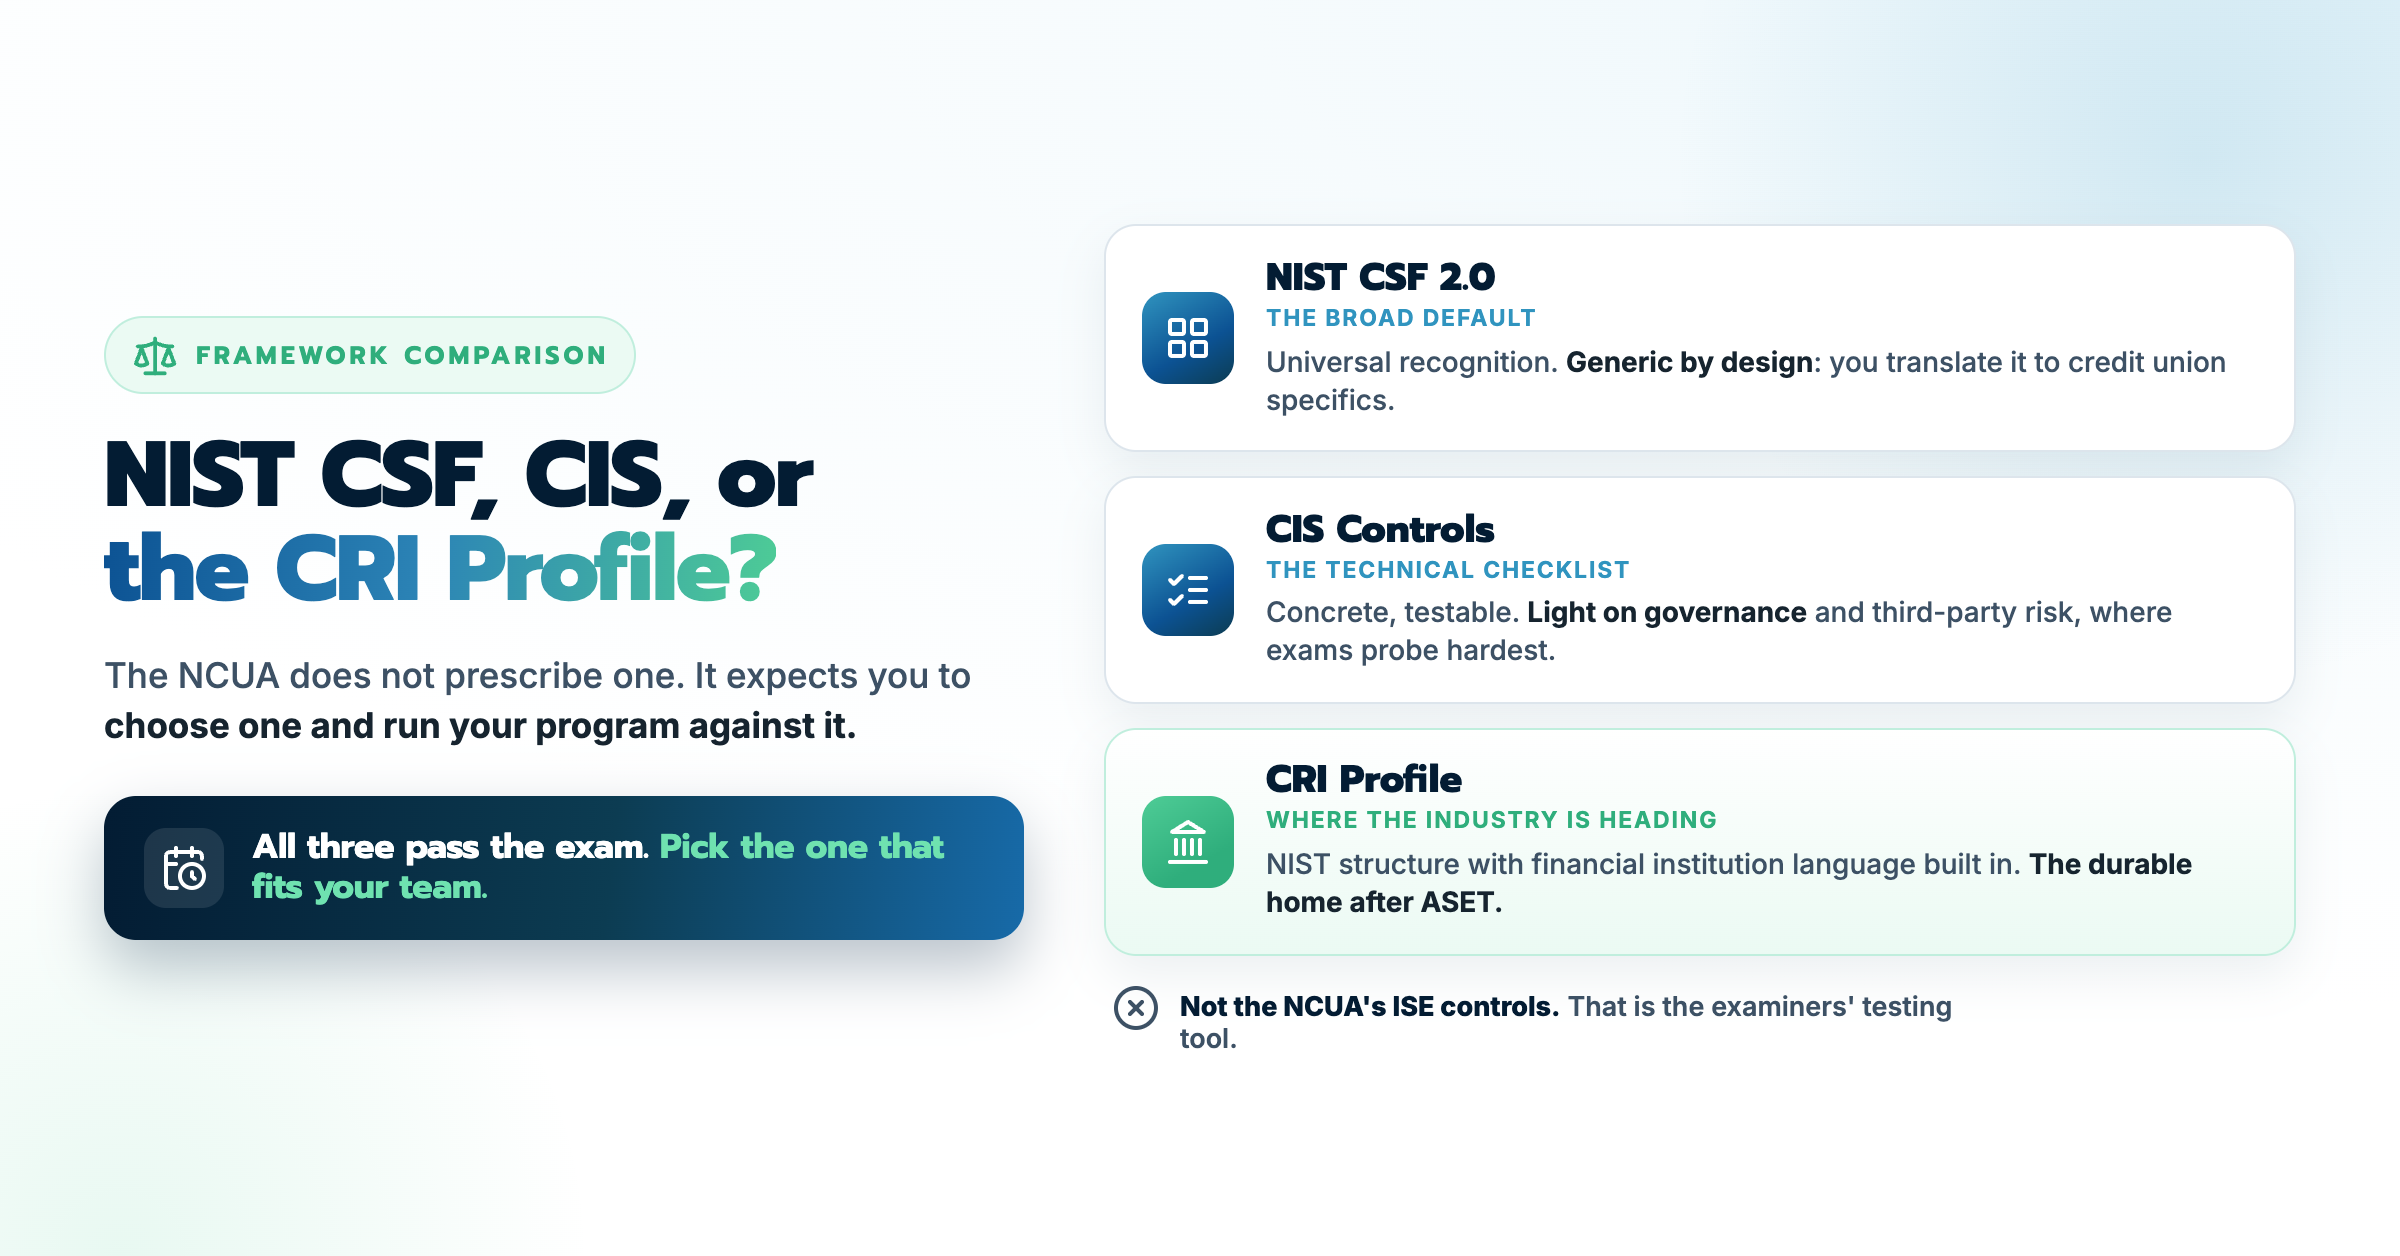
NIST CSF vs CIS vs CRI Profile: Which Framework Should Your Credit Union Choose?
Every credit union security leader eventually asks the same question, usually right before an exam or right after a merger: which framework does the...
Cybersecurity management insights, tips, and trends for security leaders, CISOs, vCISOs, and MSSPs who want to work smarter, not harder.
4 min read
Every credit union security leader eventually asks the same question, usually right before an exam or right after a merger: which framework does the...
4 min read
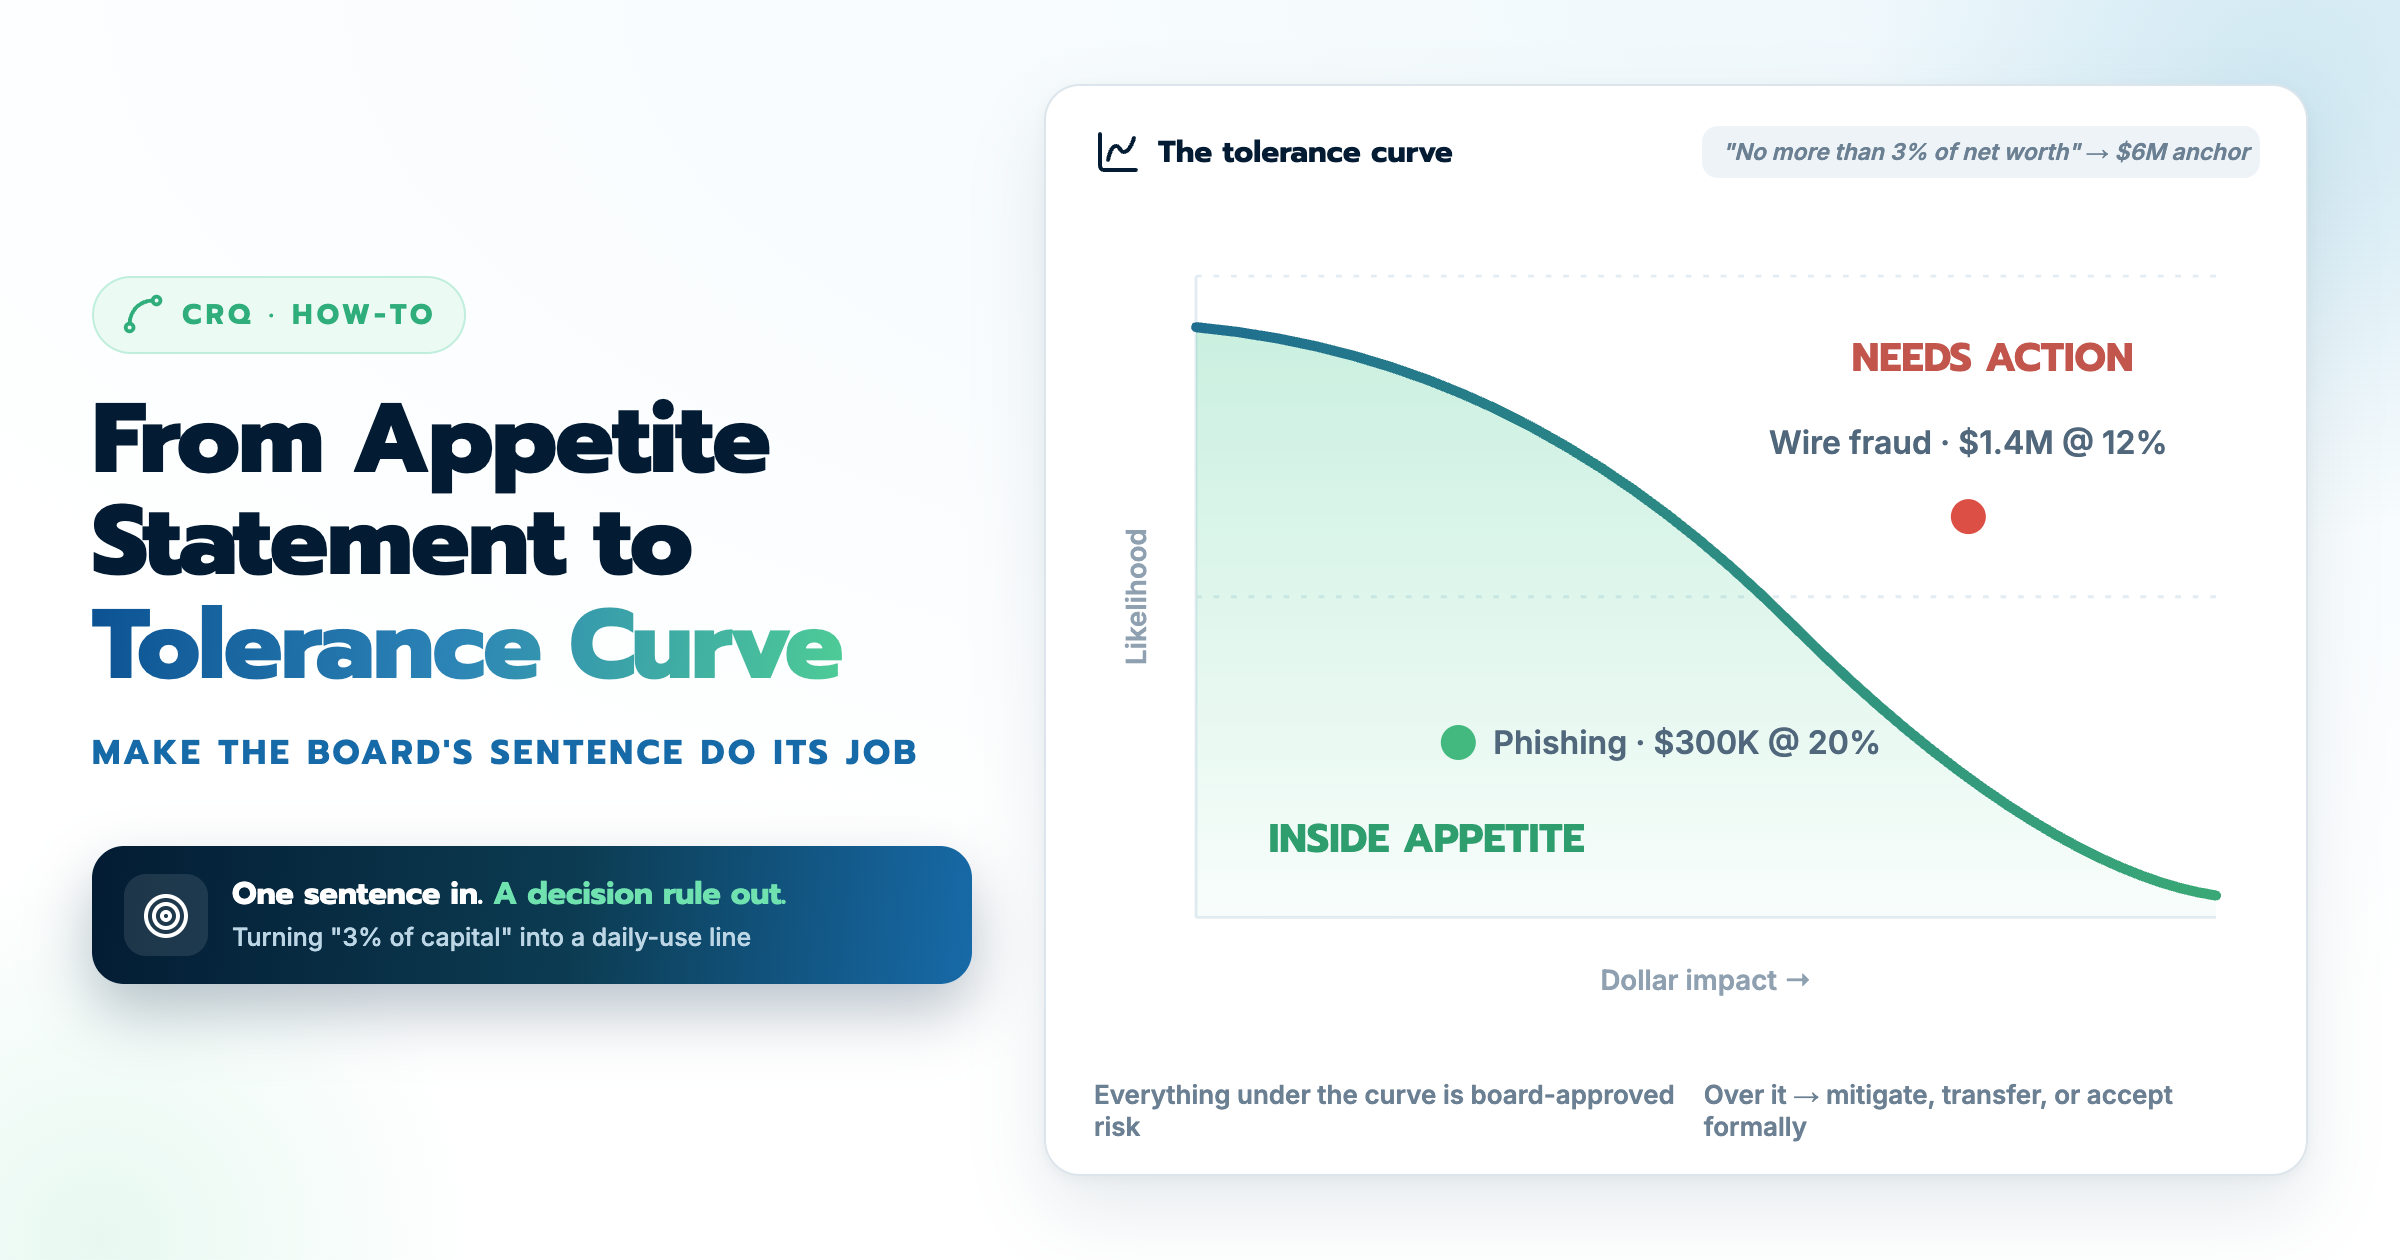
Somewhere in your board policy there is a sentence like this: "The credit union will not accept cyber risk exceeding 3 percent of net worth." The...
5 min read
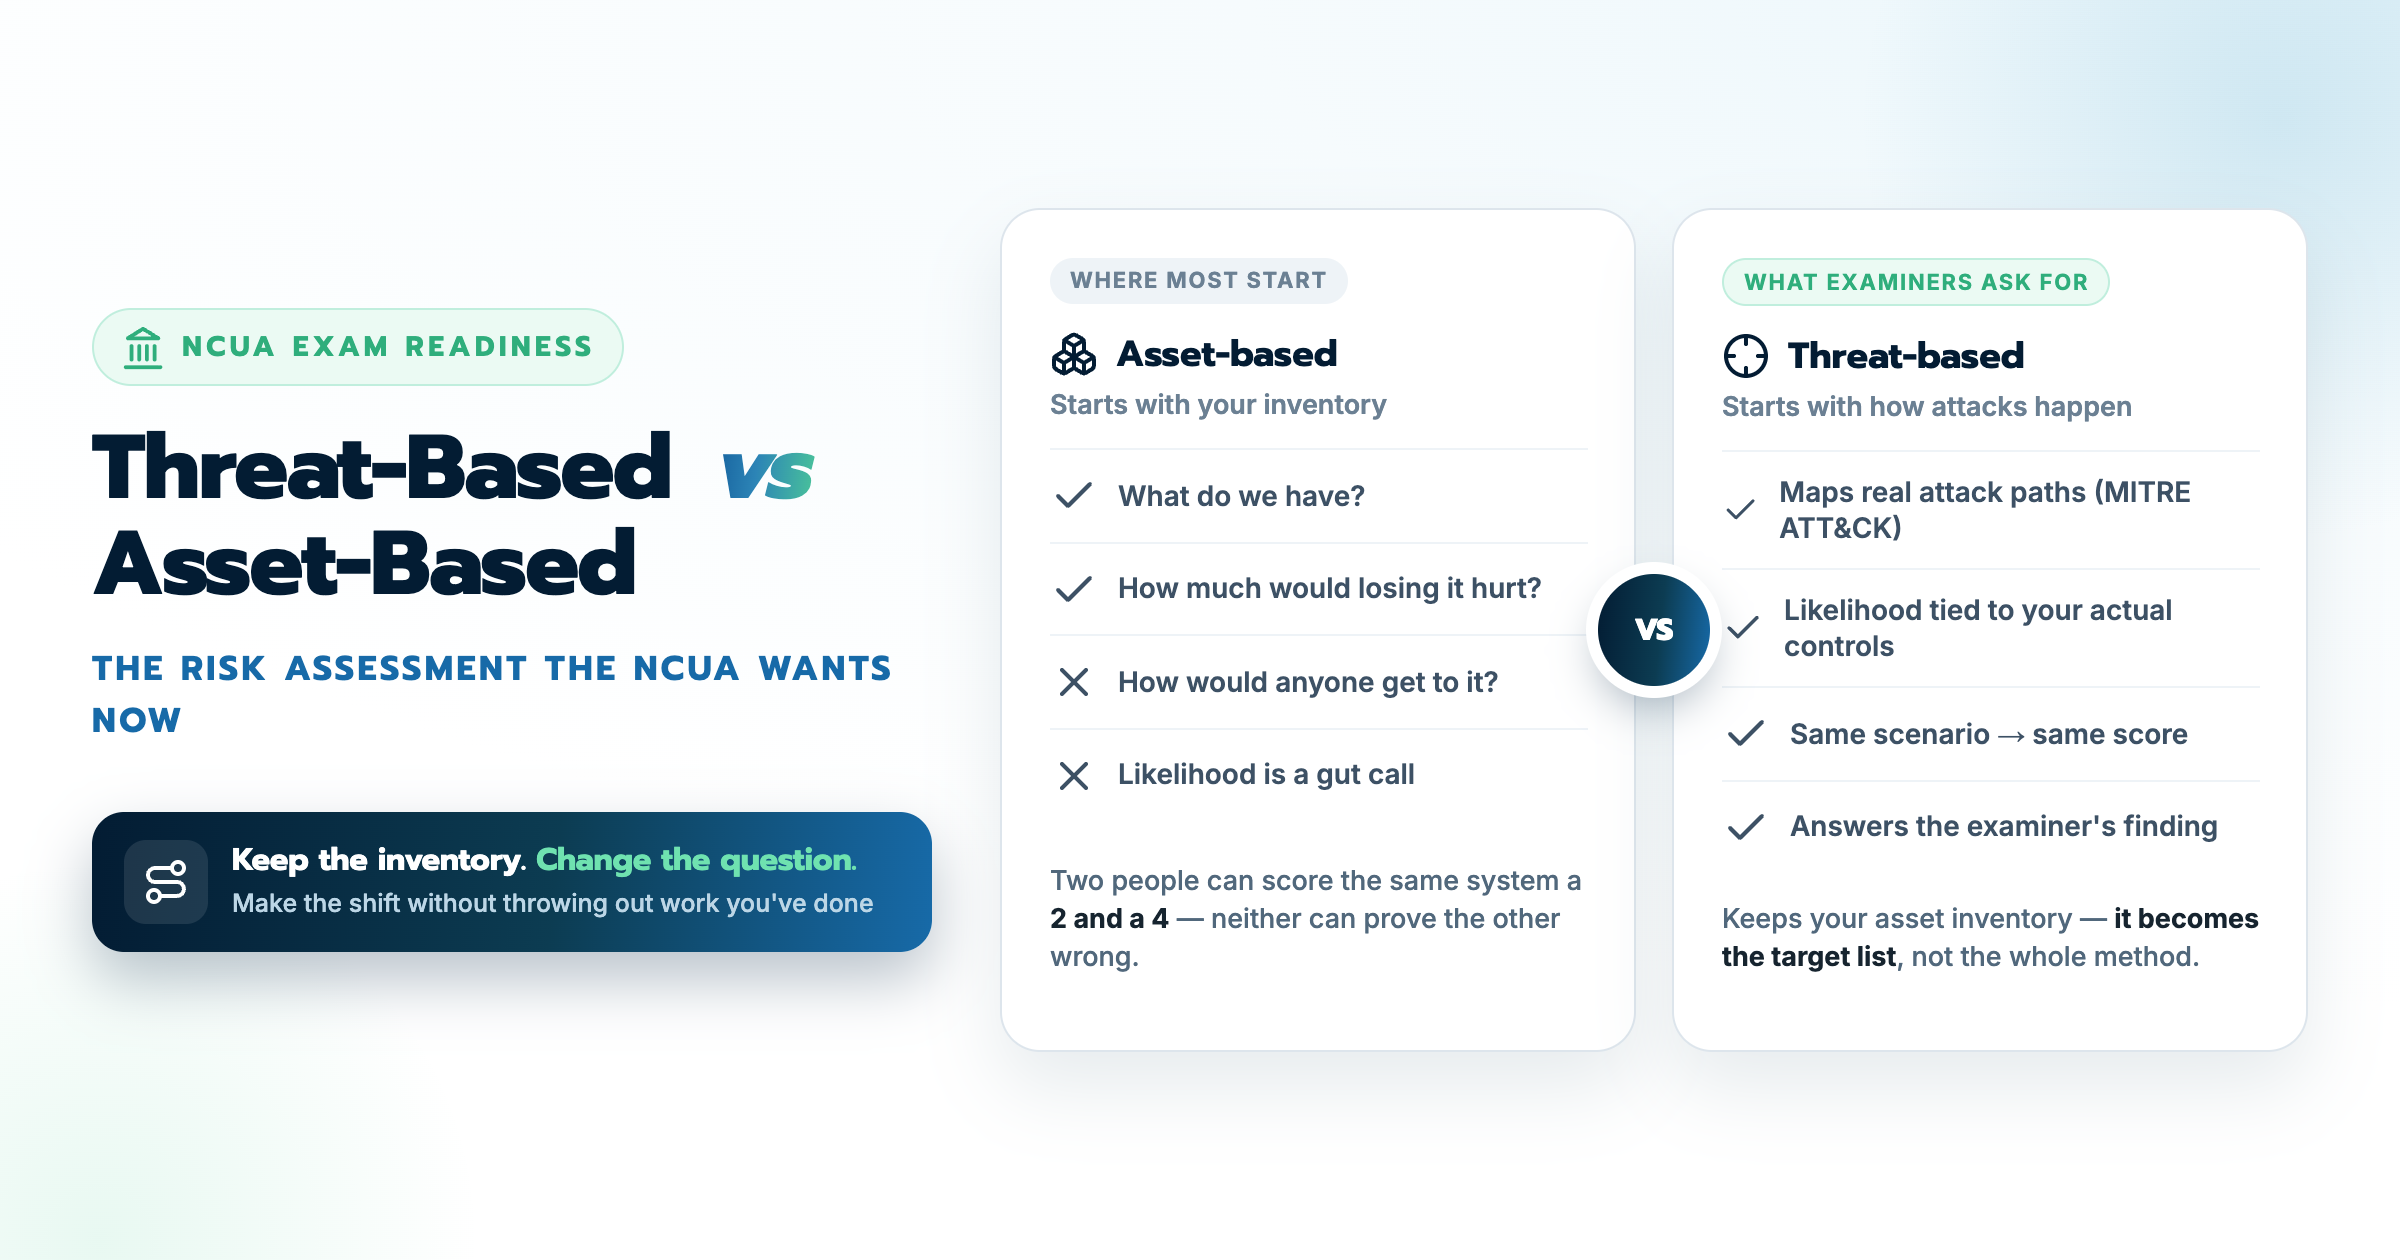
Pull up your current risk assessment and look at what the rows actually are. For most institutions, they are threats: ransomware, phishing, insider...
5 min read
The most common objection to cyber risk quantification does not come from boards. It comes from security leaders, and it goes like this: the number...
4 min read
Regulators and boards increasingly expect organizations to quantify cyber risk, turning abstract security concerns into defensible financial data as...
4 min read
Here are the key takeaways from the blog: Advanced techniques streamline IT risk assessments: The firm's innovative approach reduces client effort,...
3 min read
Here are the key takeaways from the blog: Risk-based, outcome-focused metrics: NIST 800-55 shifts the focus from compliance to measuring the...
4 min read
For security leaders responsible for safeguarding critical business data, choosing the right vCISO (Virtual Chief Information Security Officer)...
7 min read
Here are key takeaways from the blog: Traditional Risk Assessments Fall Short: Most IT risk assessments overlook real-world adversary behavior....
4 min read
Here are the key takeaways from this blog: AI Introduces New, Critical Risks: From data privacy breaches to algorithmic bias, AI systems in financial...