Skip to the main content.
Watch Demo Meet With Our Team

Lucas Hathaway

Lucas Hathaway has 10+ years of experience in information security. He is the Chief Revenue Officer at Rivial Data Security. He has worked with Rivial clients for years leading the consulting team and now leads the growth team with a focus on client success ensuring that Rivial’s platform exceeds client expectations.

5 min read

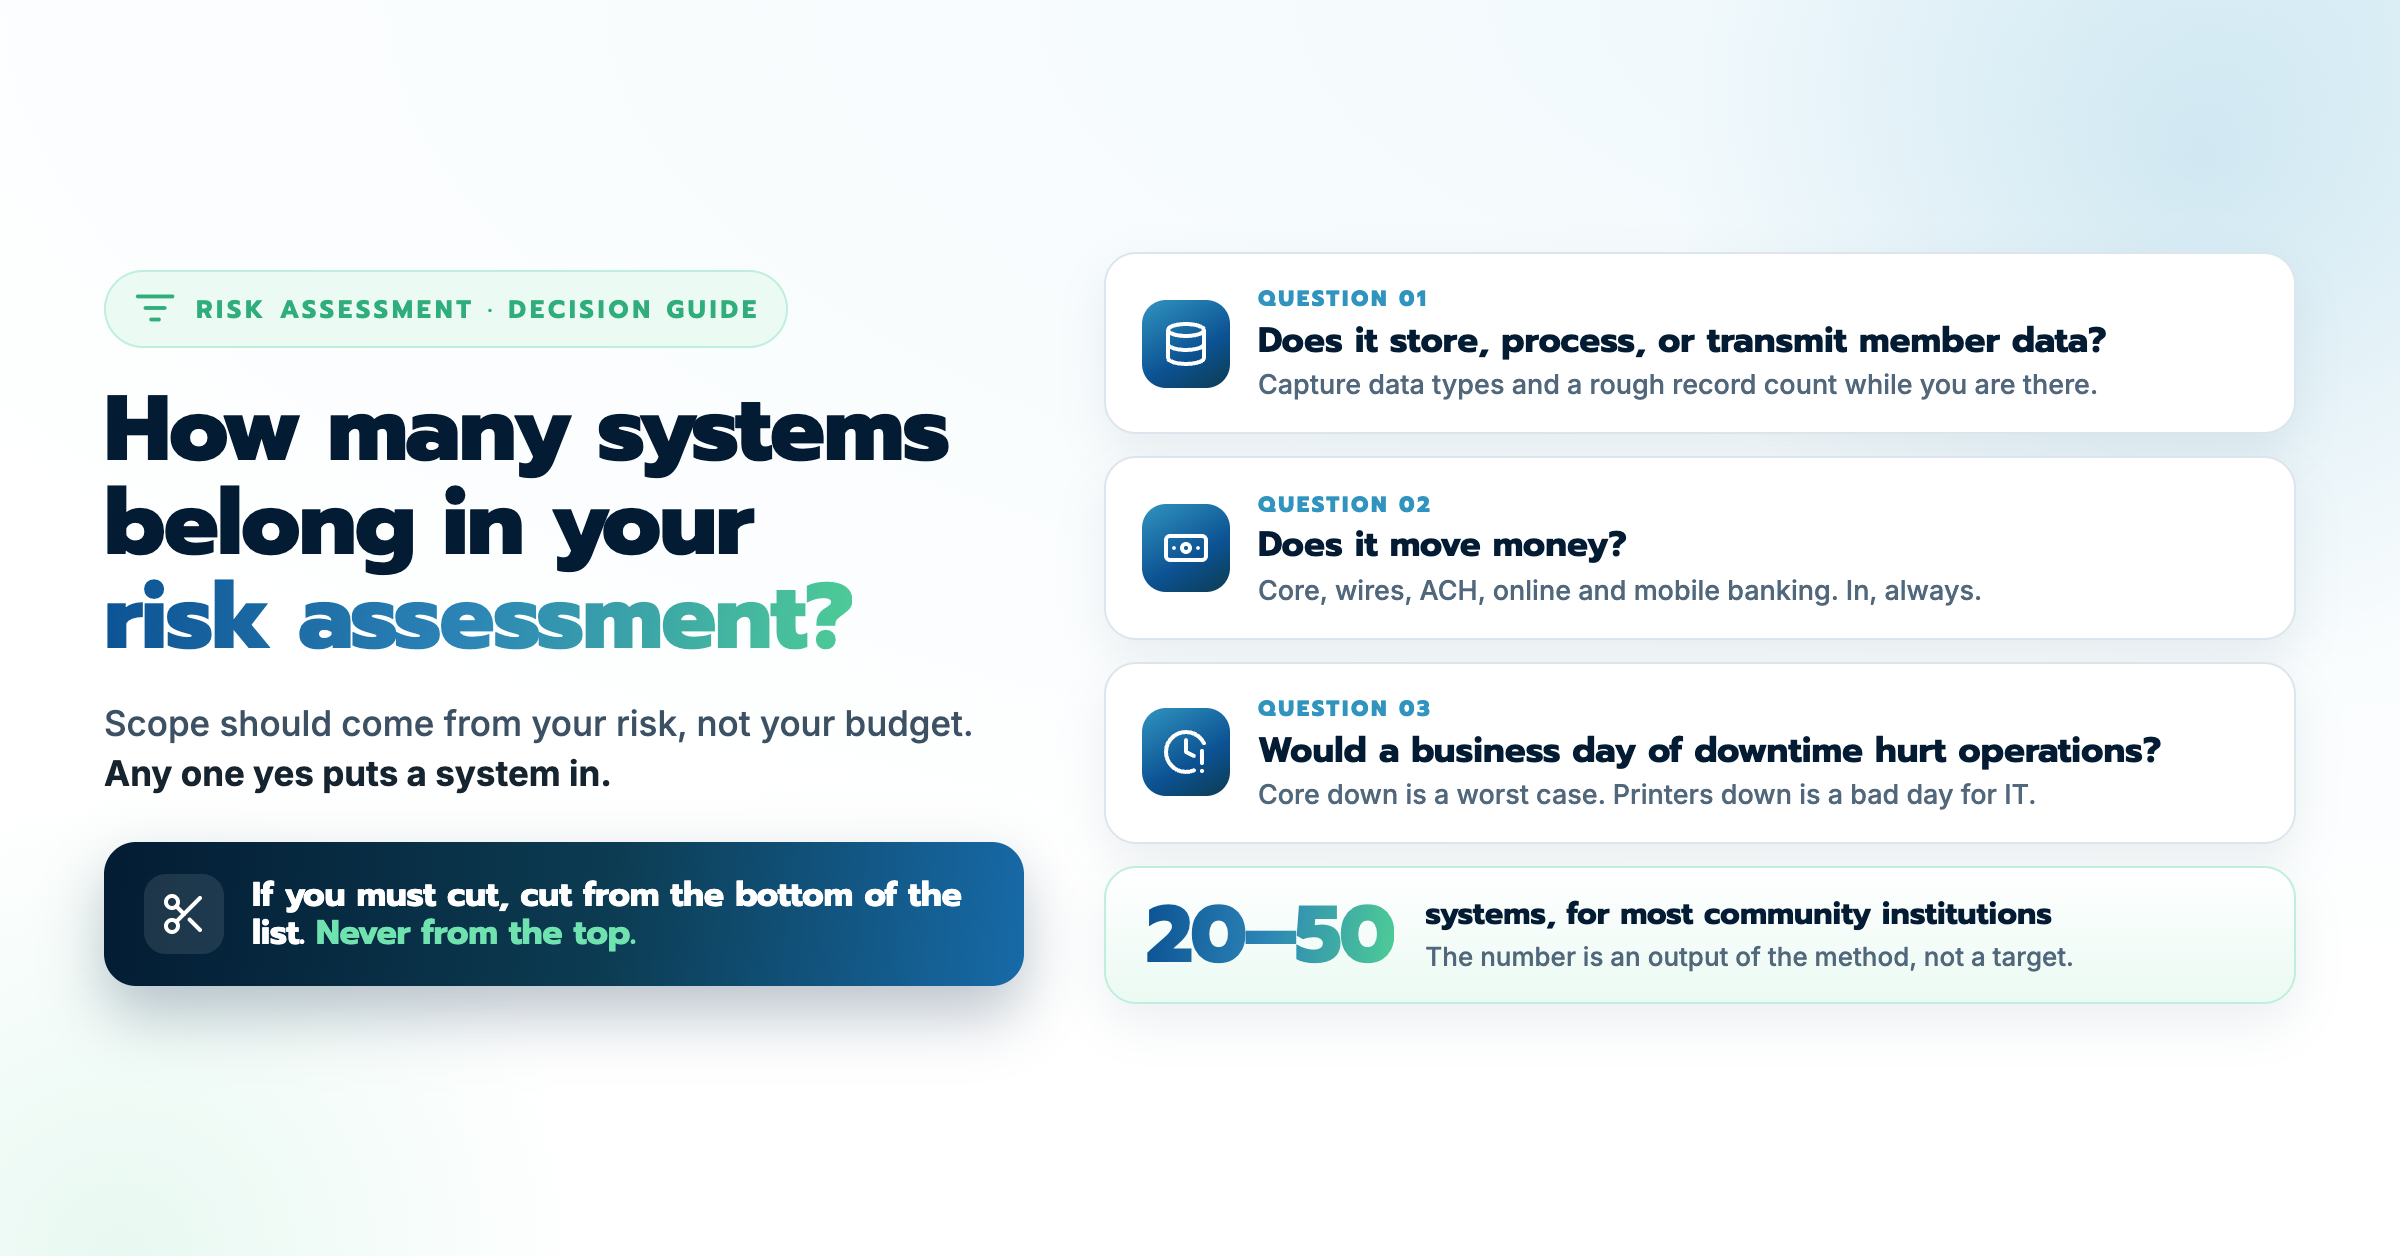
How Many Systems Belong in Your IT Risk Assessment?

Somewhere in almost every risk assessment proposal, the same quiet negotiation happens. The list starts at 60 systems, someone winces at the price, and it gets trimmed to 40. Another institution insists 20 is plenty. A third is sure the answer is...

Read More
5 min read

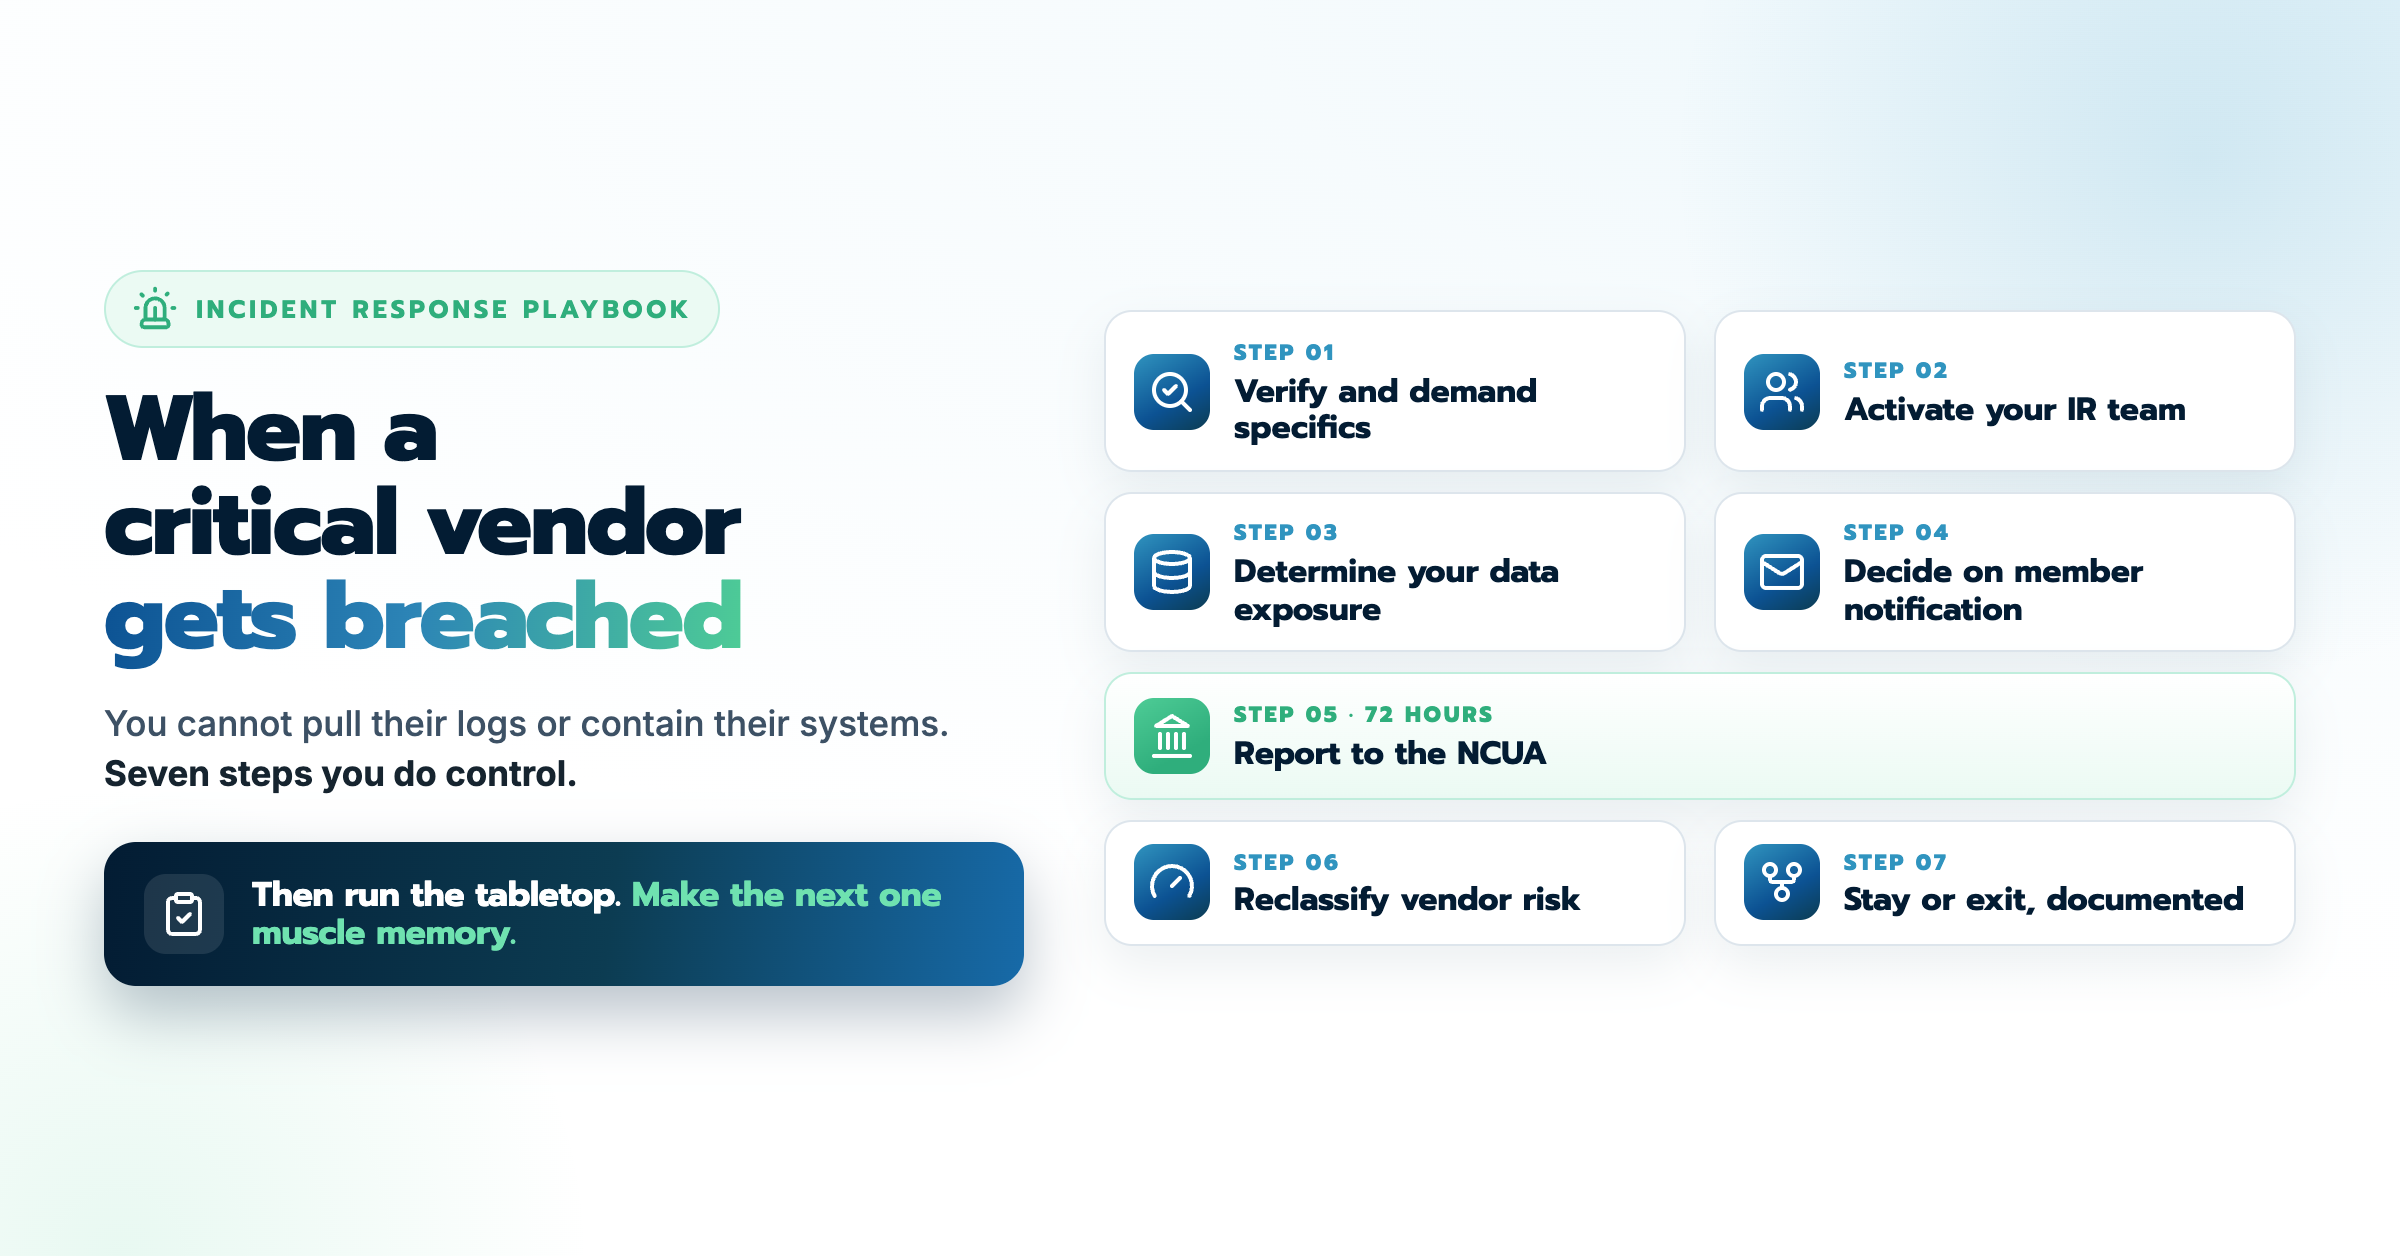
Incident Response Playbook: When a Critical Vendor Gets Breached

If you work at a credit union, the last few months have made one thing hard to ignore: your next incident probably will not start on your network. It...

Read More

4 min read

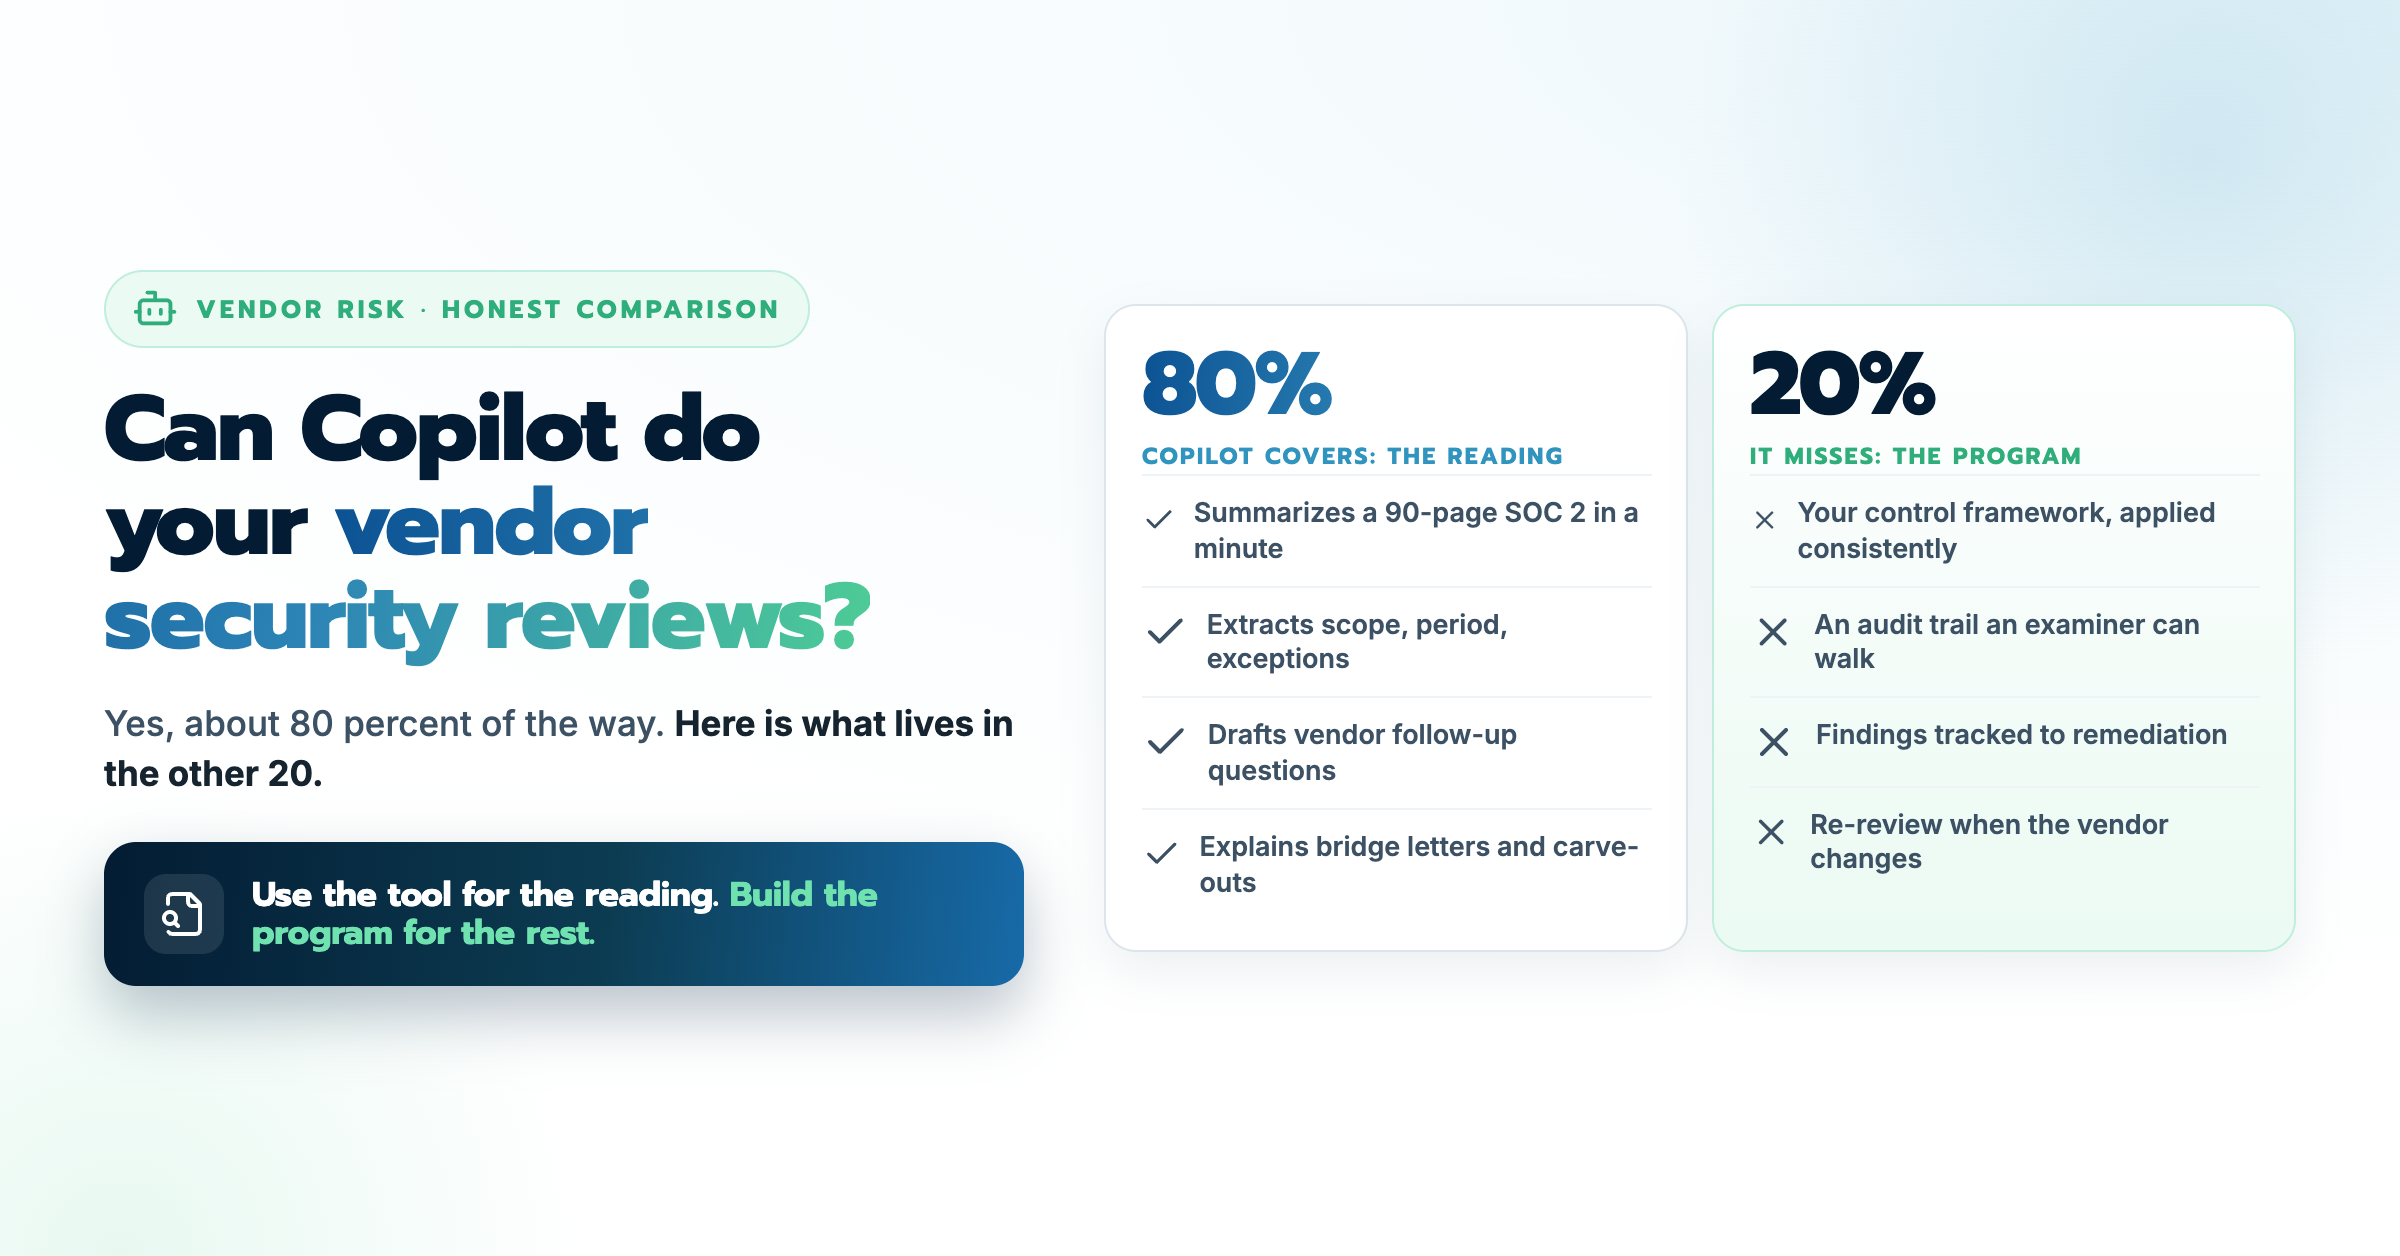
Can Copilot Do Your Vendor Security Reviews? An Honest Answer

A risk leader at a financial institution told us on a call this year, plainly, that Copilot already gets his team about 80 percent of the way through...

Read More

6 min read

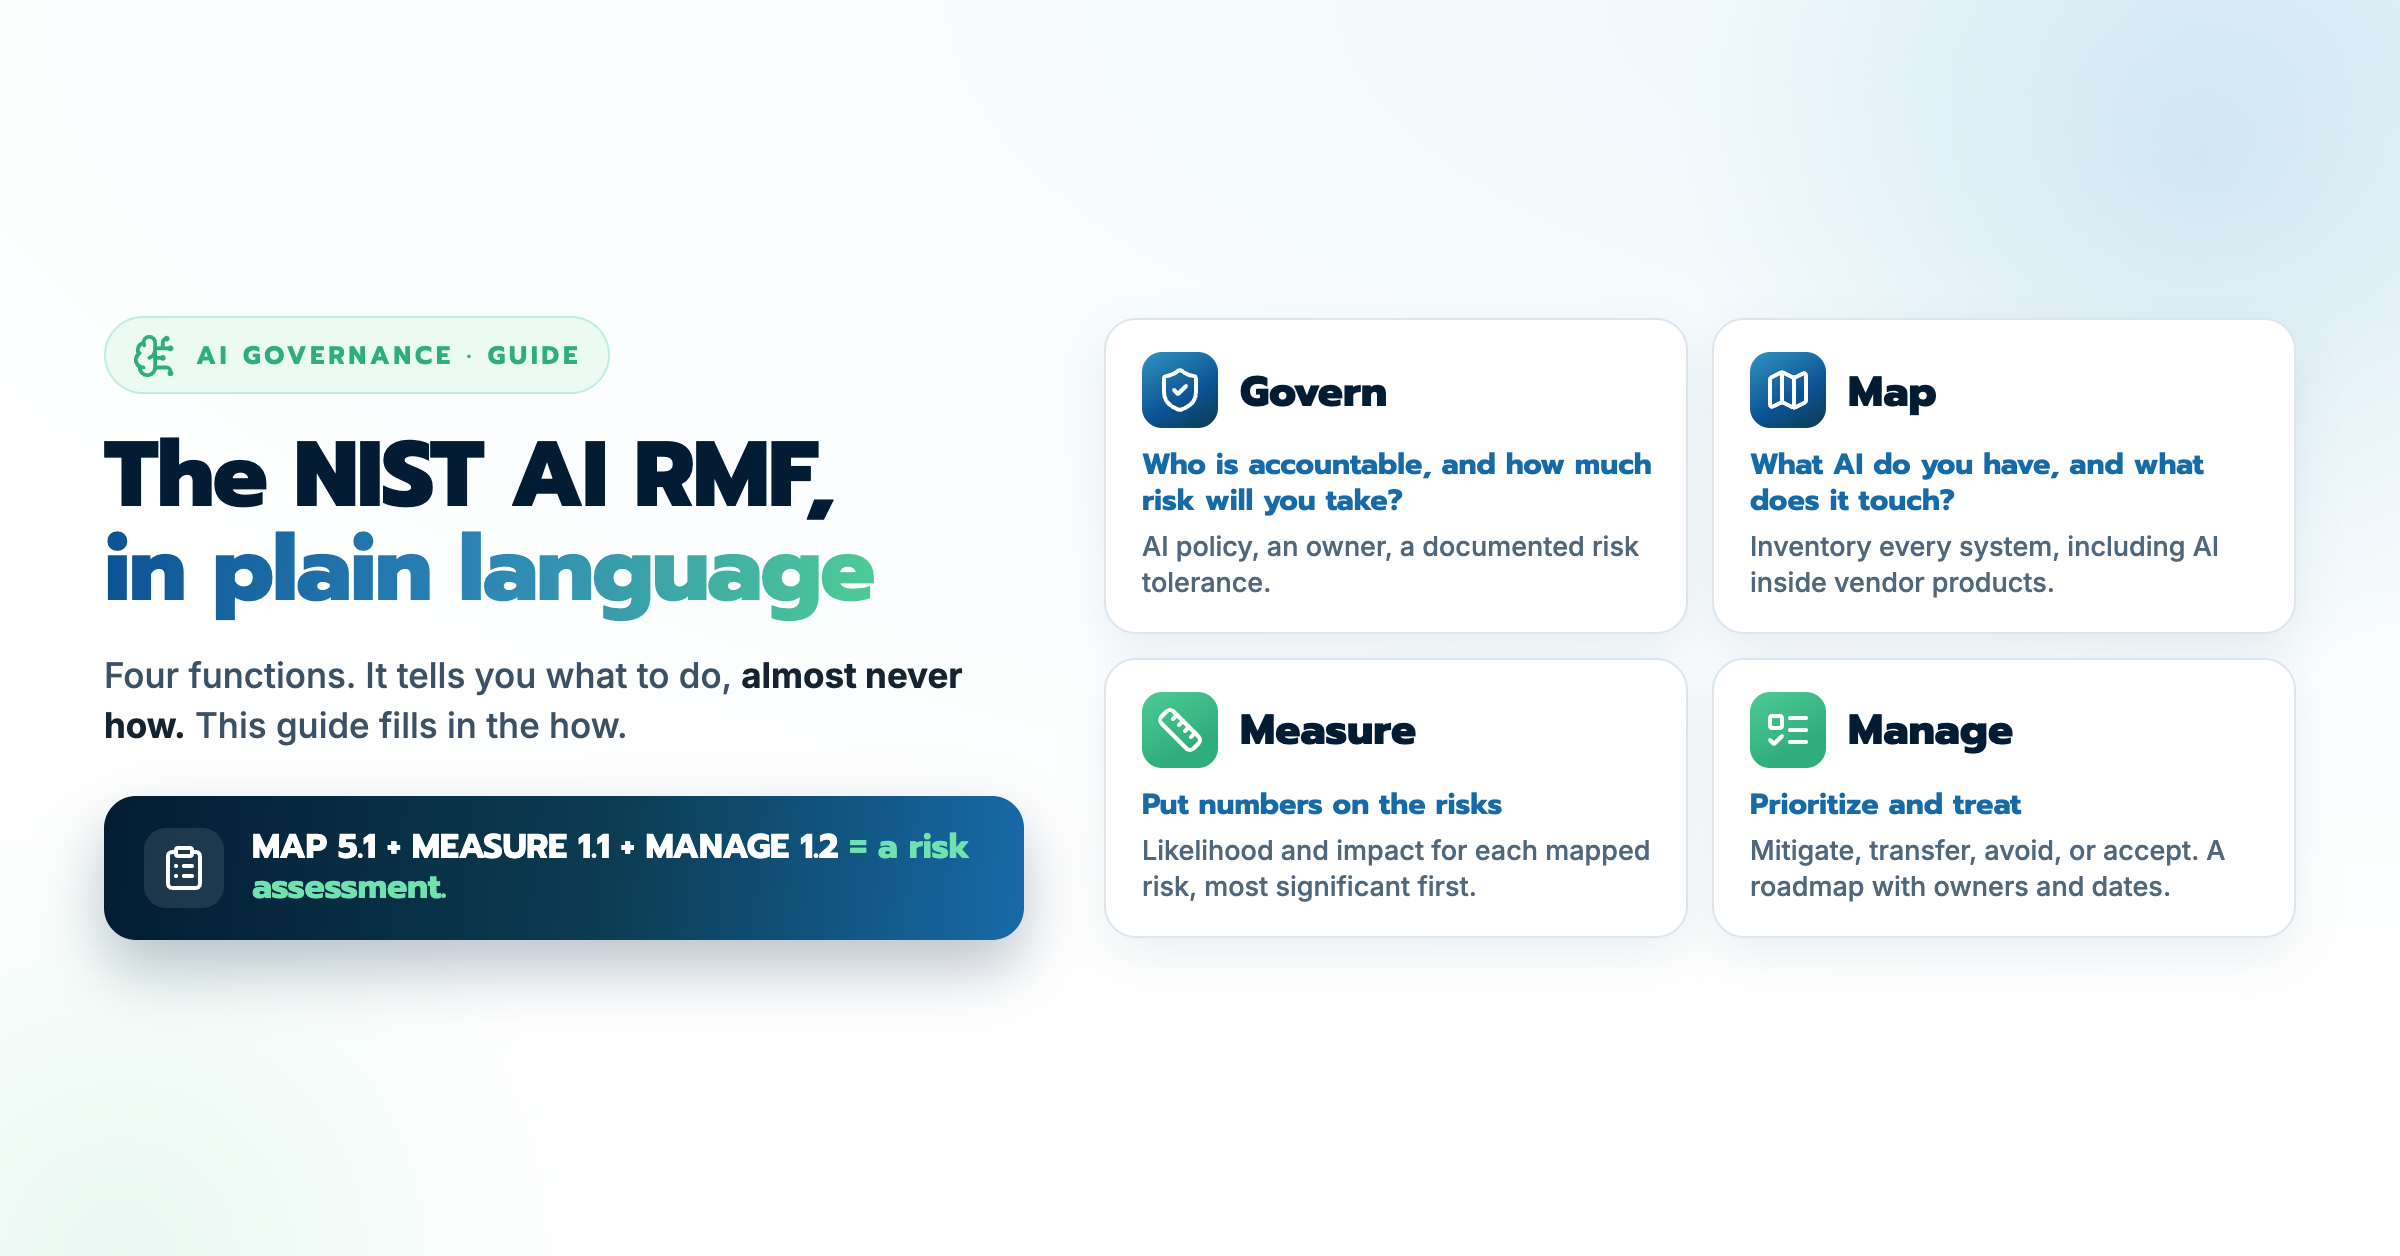
NIST AI RMF for Financial Institutions: A Complete Guide

Financial institutions are adopting AI faster than they are governing it, and the request we now hear on calls is specific: "we need a credible AI...

Read More

8 min read

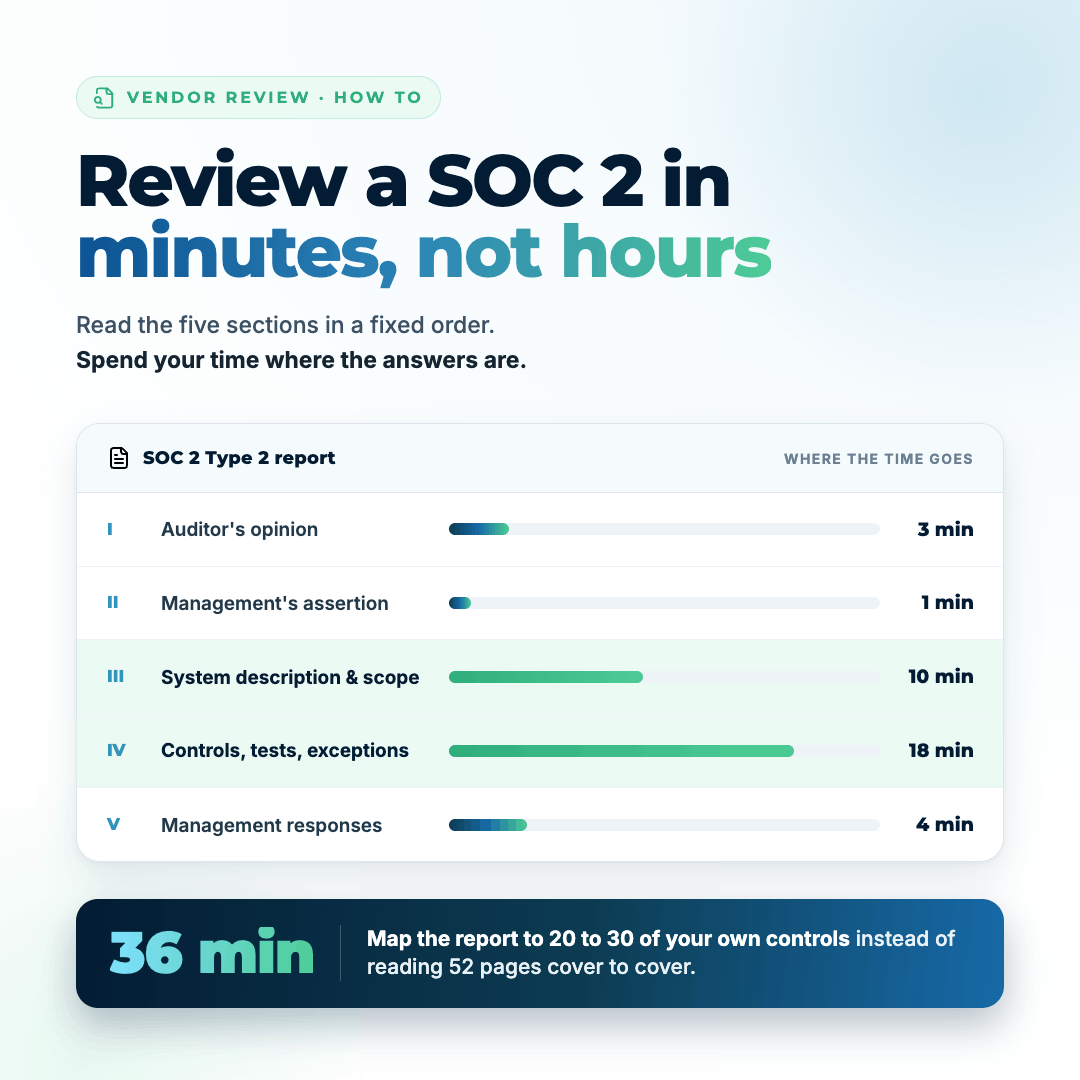
How to Review a SOC 2 Report in Minutes, Not Hours

A security manager at a credit union told us recently that vendor security reviews are the bane of his existence. Another opened a call by saying a...

Read More
Cyber Risk Appetite Statement

8 min read

How to Write a Cyber Risk Appetite Statement

For CISOs, IT risk leaders, compliance officers, and the board committees they report to, a cyber risk appetite statement is the document that...

Read More

8 min read

Shadow AI: A Guide to Finding the AI Already Inside Your Institution

A security officer at a credit union described their AI inventory to us like this: they went through the exercise, came out the other side with only...

Read More

8 min read

Every Vendor Has an AI Feature. Here's How to Assess It

A risk leader at a large financial institution said something on a call this year that we have heard some version of at almost every institution...

Read More
Cybersecurity Risk Register

8 min read

How to Build a Cybersecurity Risk Register

For CISOs, IT risk leaders, compliance officers, and vCISOs, a cybersecurity risk register is the single source of truth that turns scattered...

Read More

5 min read

Quantitative vs Qualitative Cyber Risk Assessment: What Is the Difference?

Quick answer: A qualitative cyber risk assessment rates risk with labels like high, medium, and low, often on a color-coded heat map. A quantitative...

Read More