Skip to the main content.
Watch Demo Meet With Our Team
Rivial’s Cybersecurity blog

The Savvy CISO

Cybersecurity management insights, tips, and trends for security leaders, CISOs, vCISOs, and MSSPs who want to work smarter, not harder.

6 min read

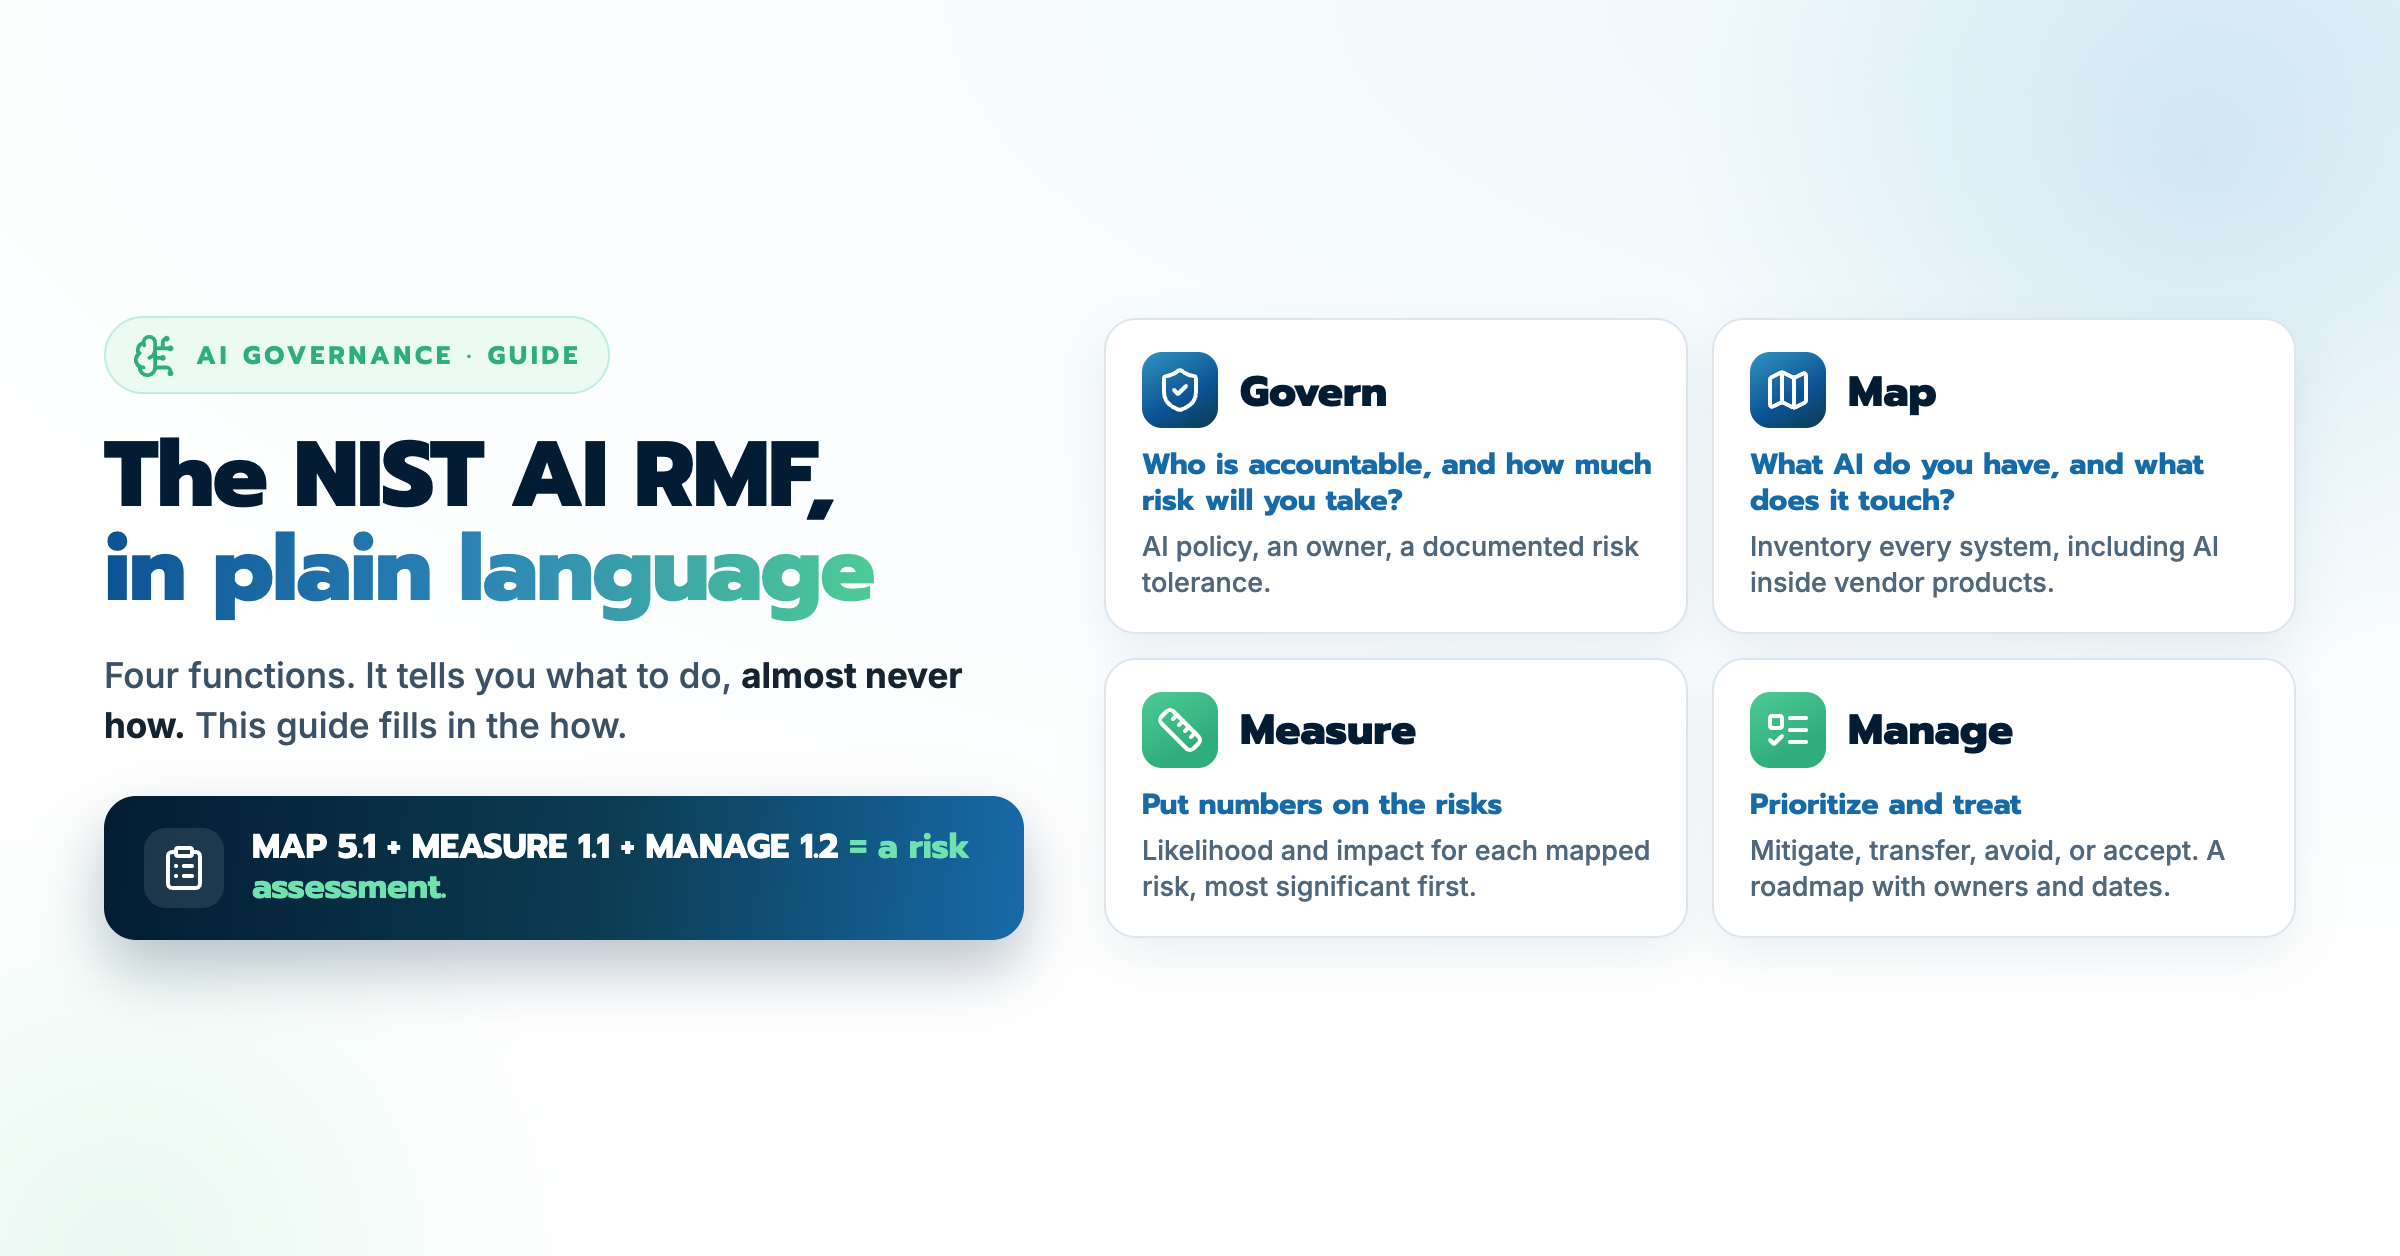
NIST AI RMF for Financial Institutions: A Complete Guide

Financial institutions are adopting AI faster than they are governing it, and the request we now hear on calls is specific: "we need a credible AI governance framework, and we think it is the NIST AI RMF. Where do we start?" Boards are asking for a...

Read More
4 min read

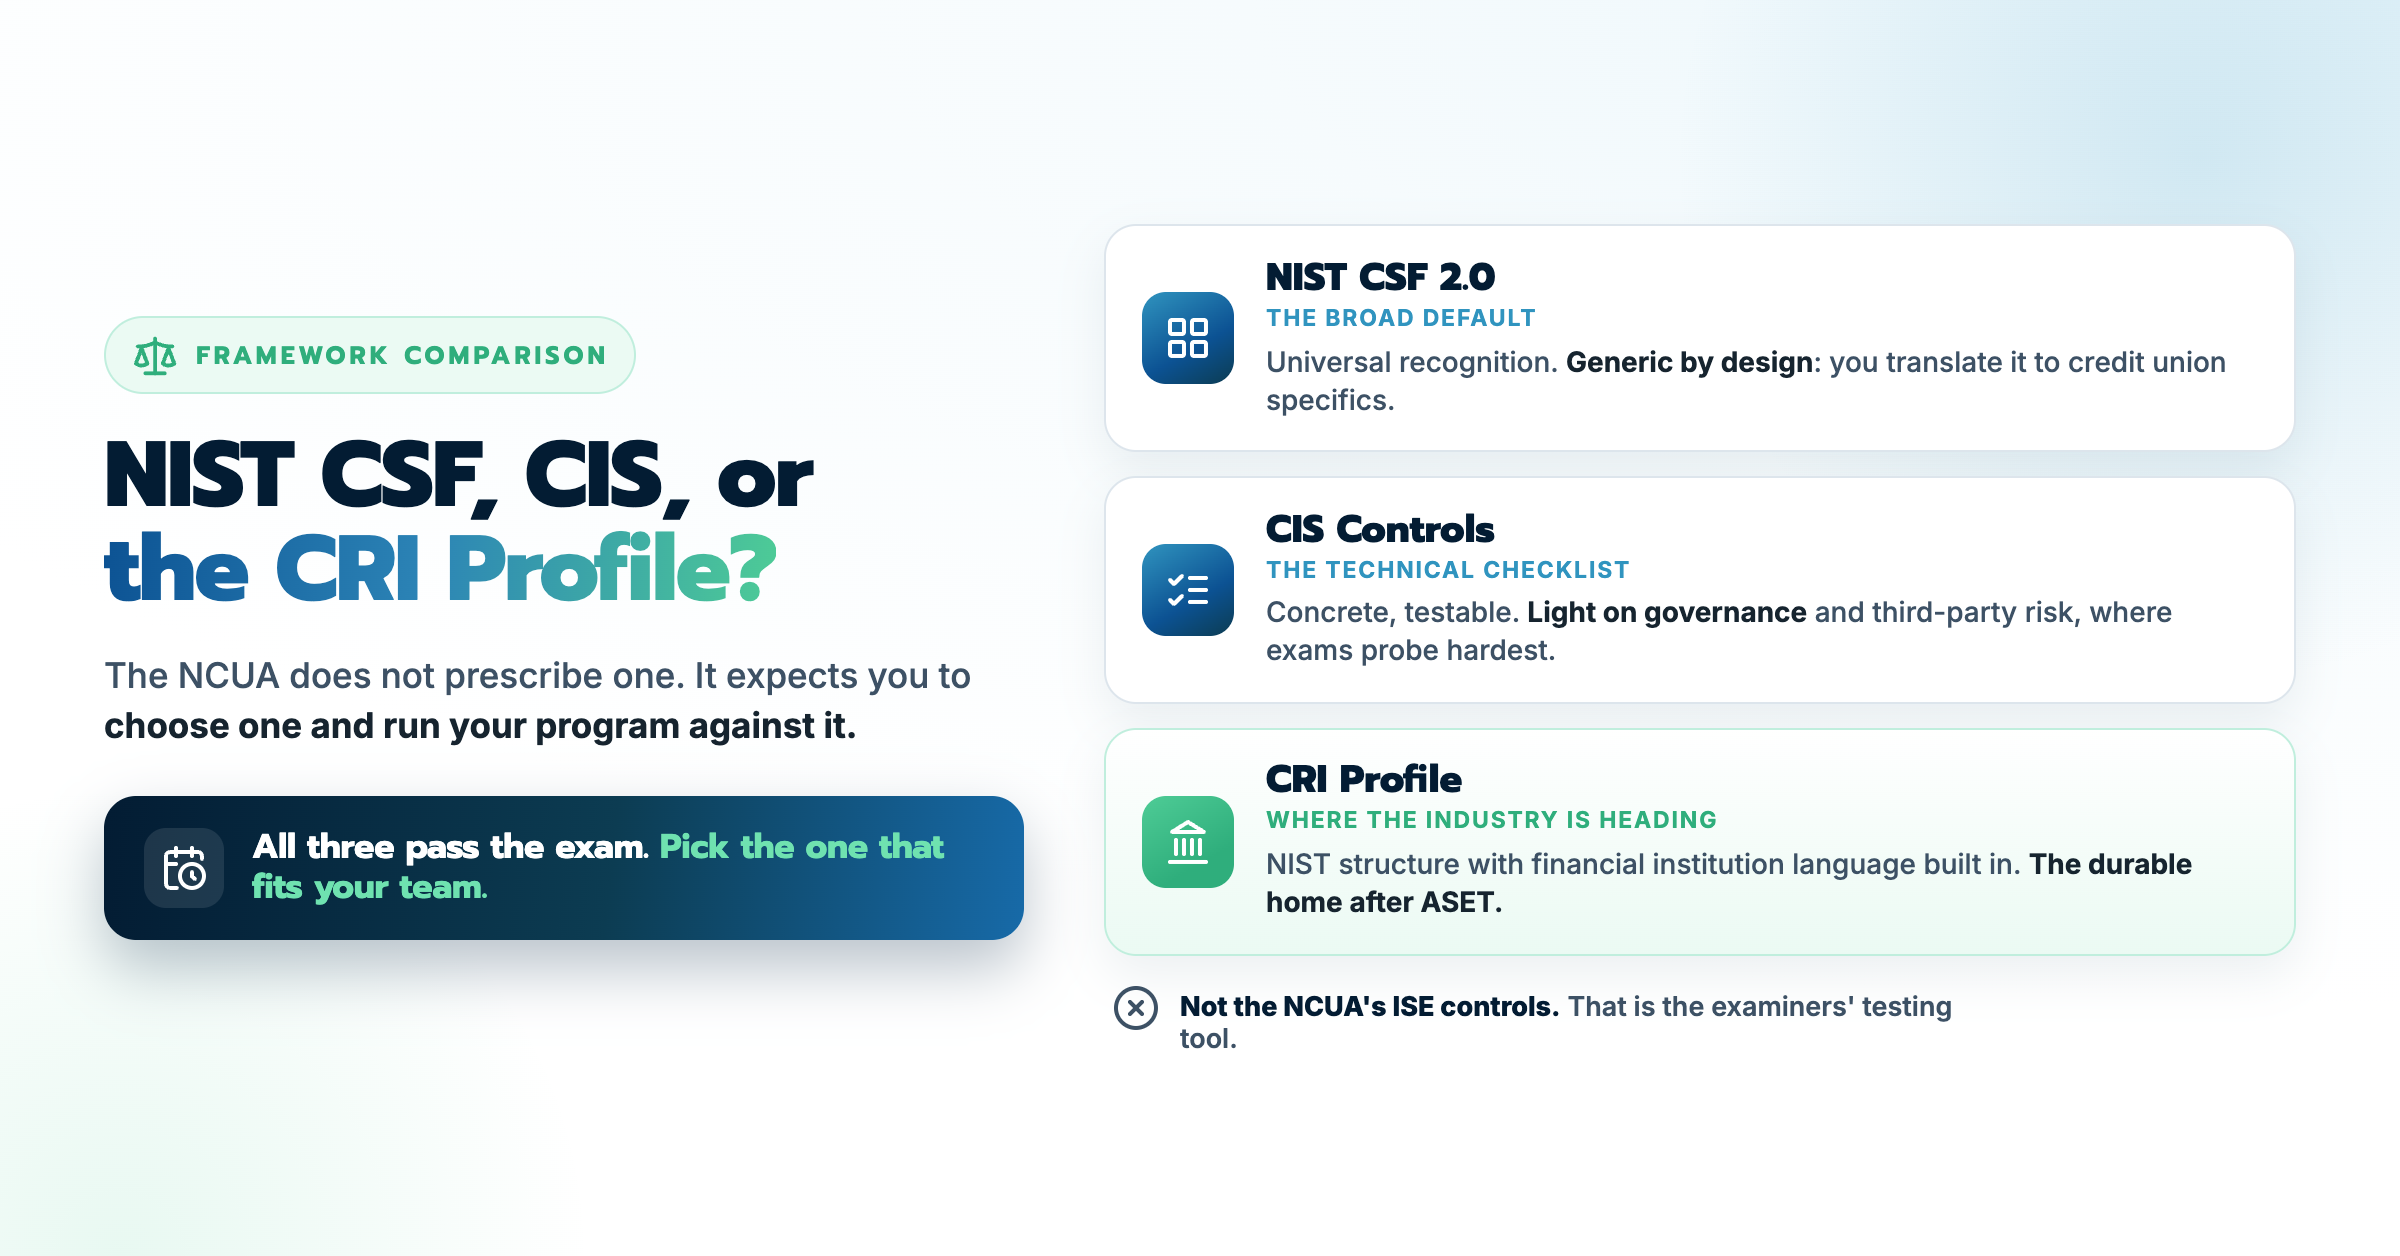
NIST CSF vs CIS vs CRI Profile: Which Framework Should Your Credit Union Choose?

Every credit union security leader eventually asks the same question, usually right before an exam or right after a merger: which framework does the...

Read More

4 min read

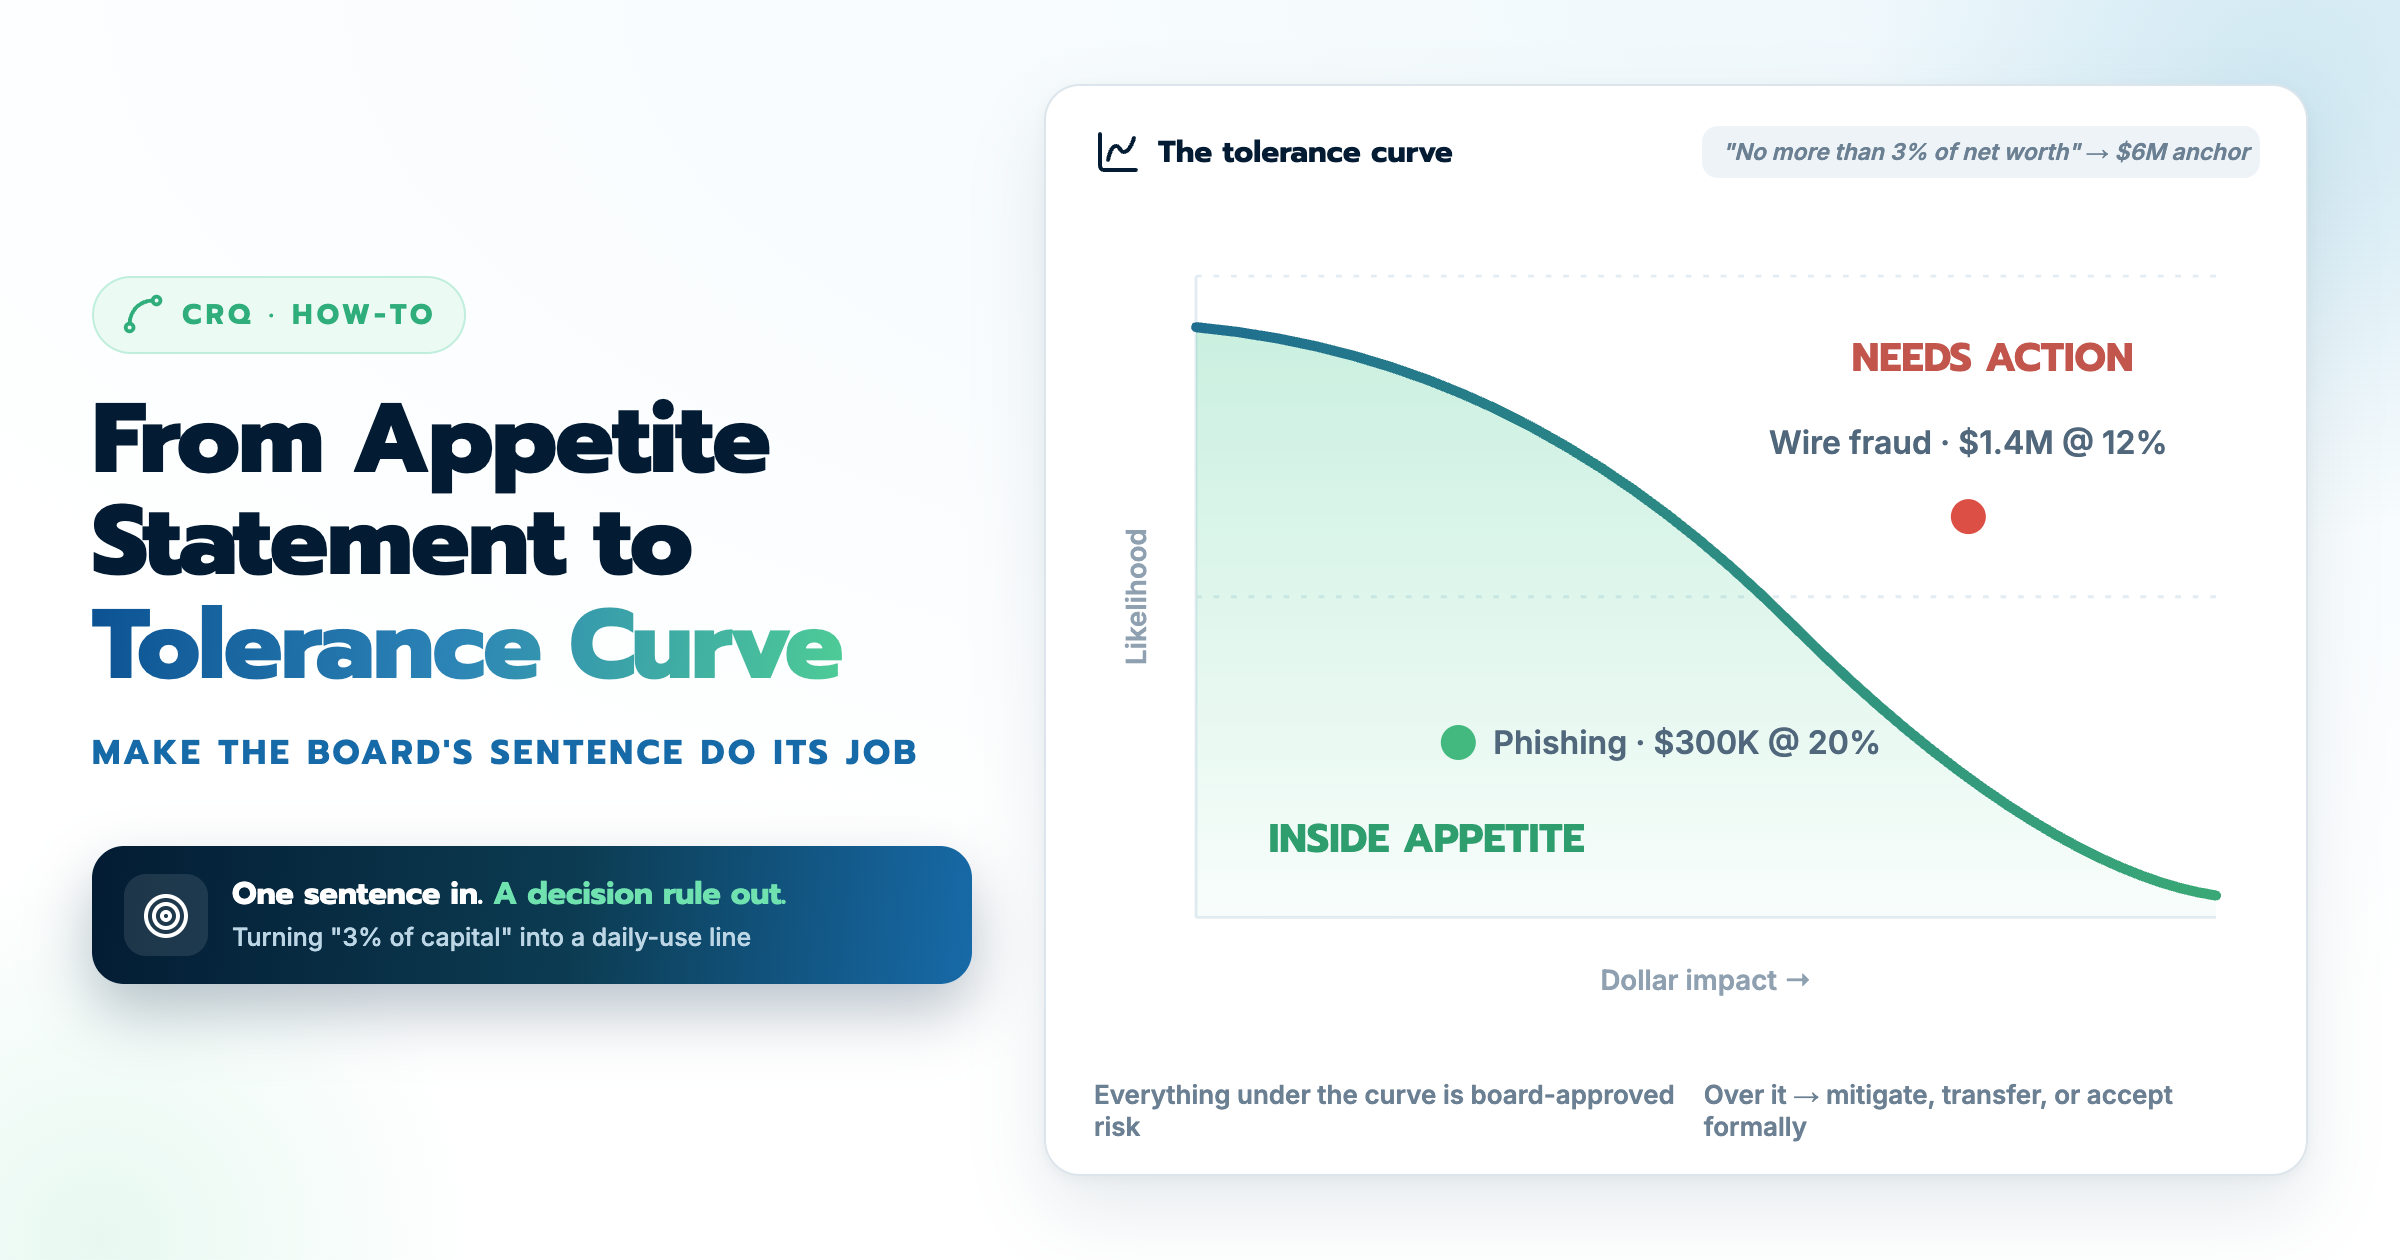
How to Turn a Risk Appetite Statement Into a Usable Curve

Somewhere in your board policy there is a sentence like this: "The credit union will not accept cyber risk exceeding 3 percent of net worth." The...

Read More

5 min read

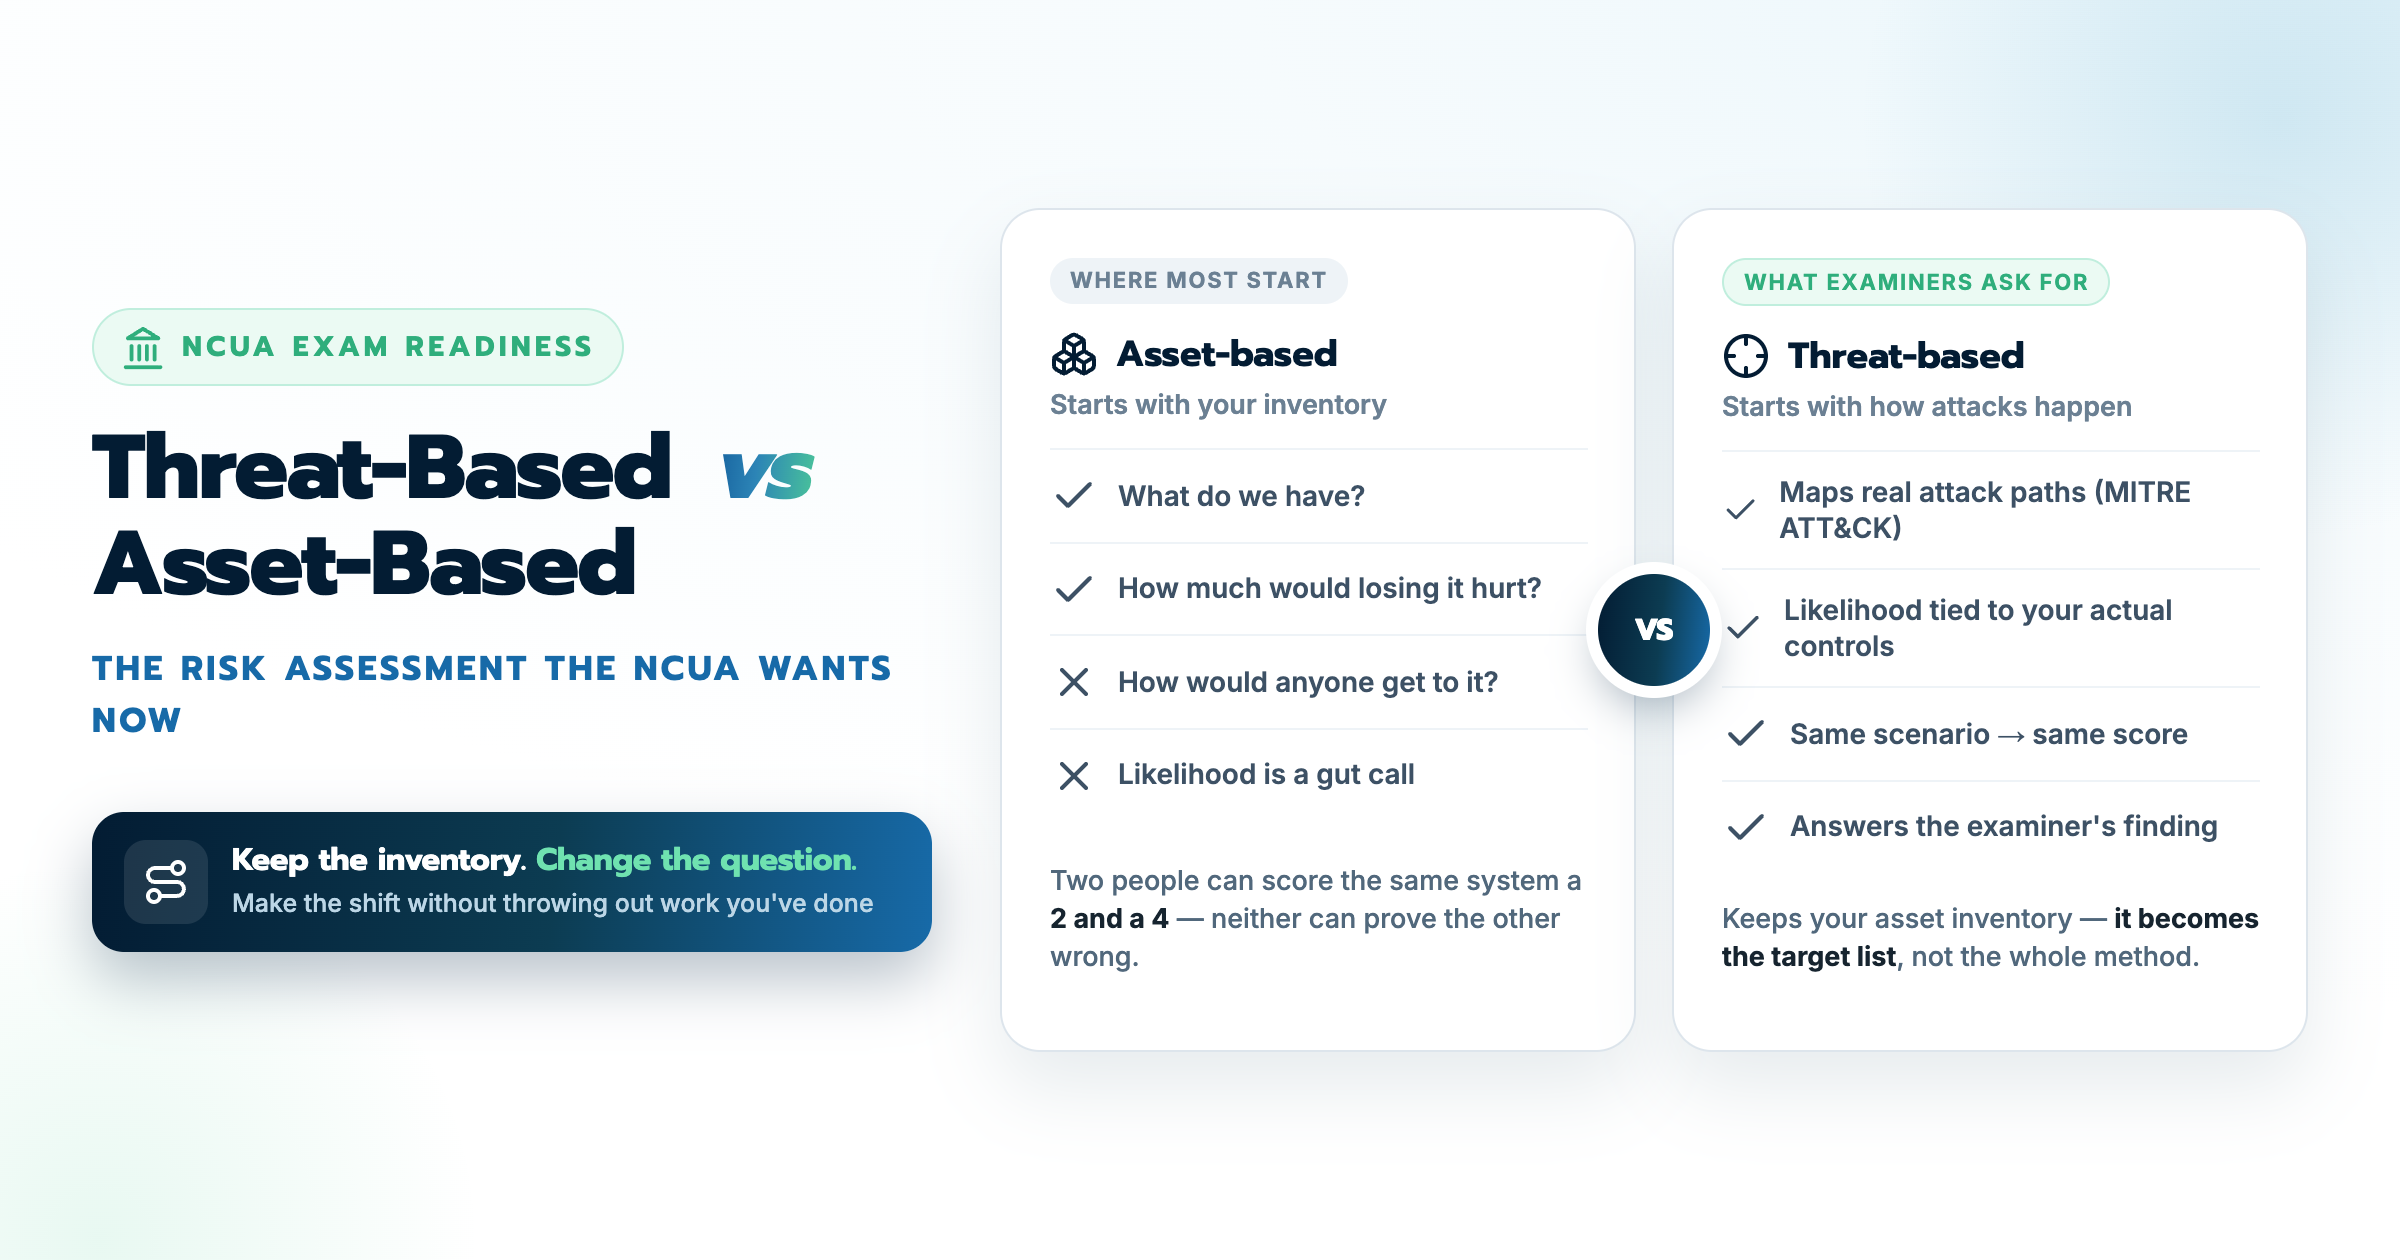
Threat-Based vs Asset-Based Risk Assessment: NCUA View

Pull up your current risk assessment and look at what the rows actually are. For most institutions, they are threats: ransomware, phishing, insider...

Read More

5 min read

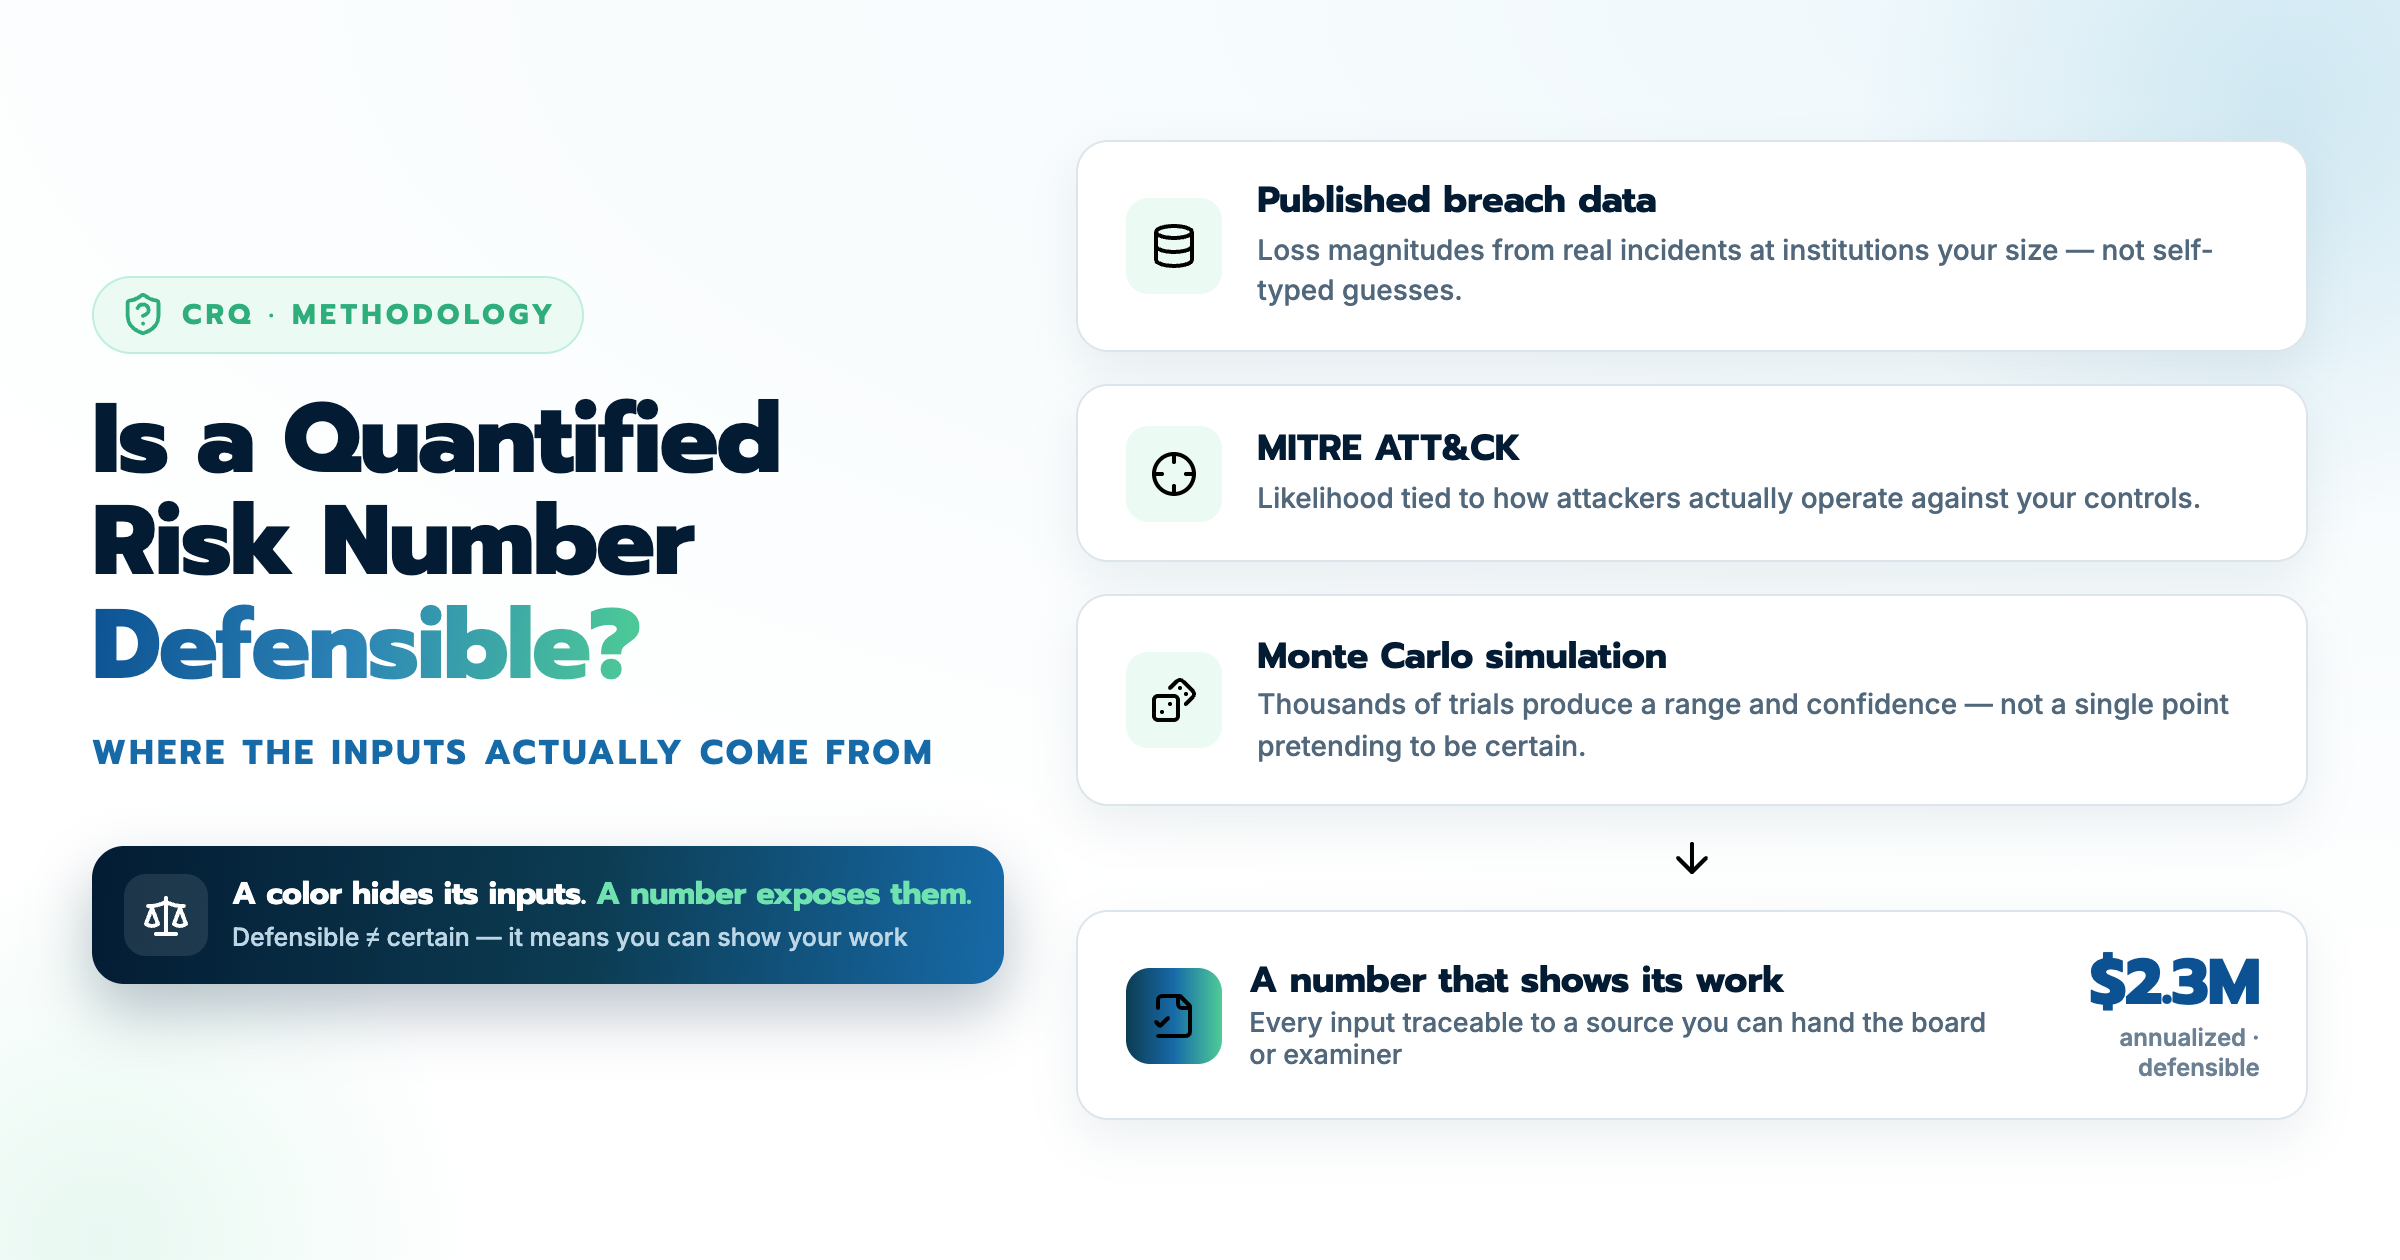
Is a Quantified Cyber Risk Number Defensible? The Inputs

The most common objection to cyber risk quantification does not come from boards. It comes from security leaders, and it goes like this: the number...

Read More

4 min read

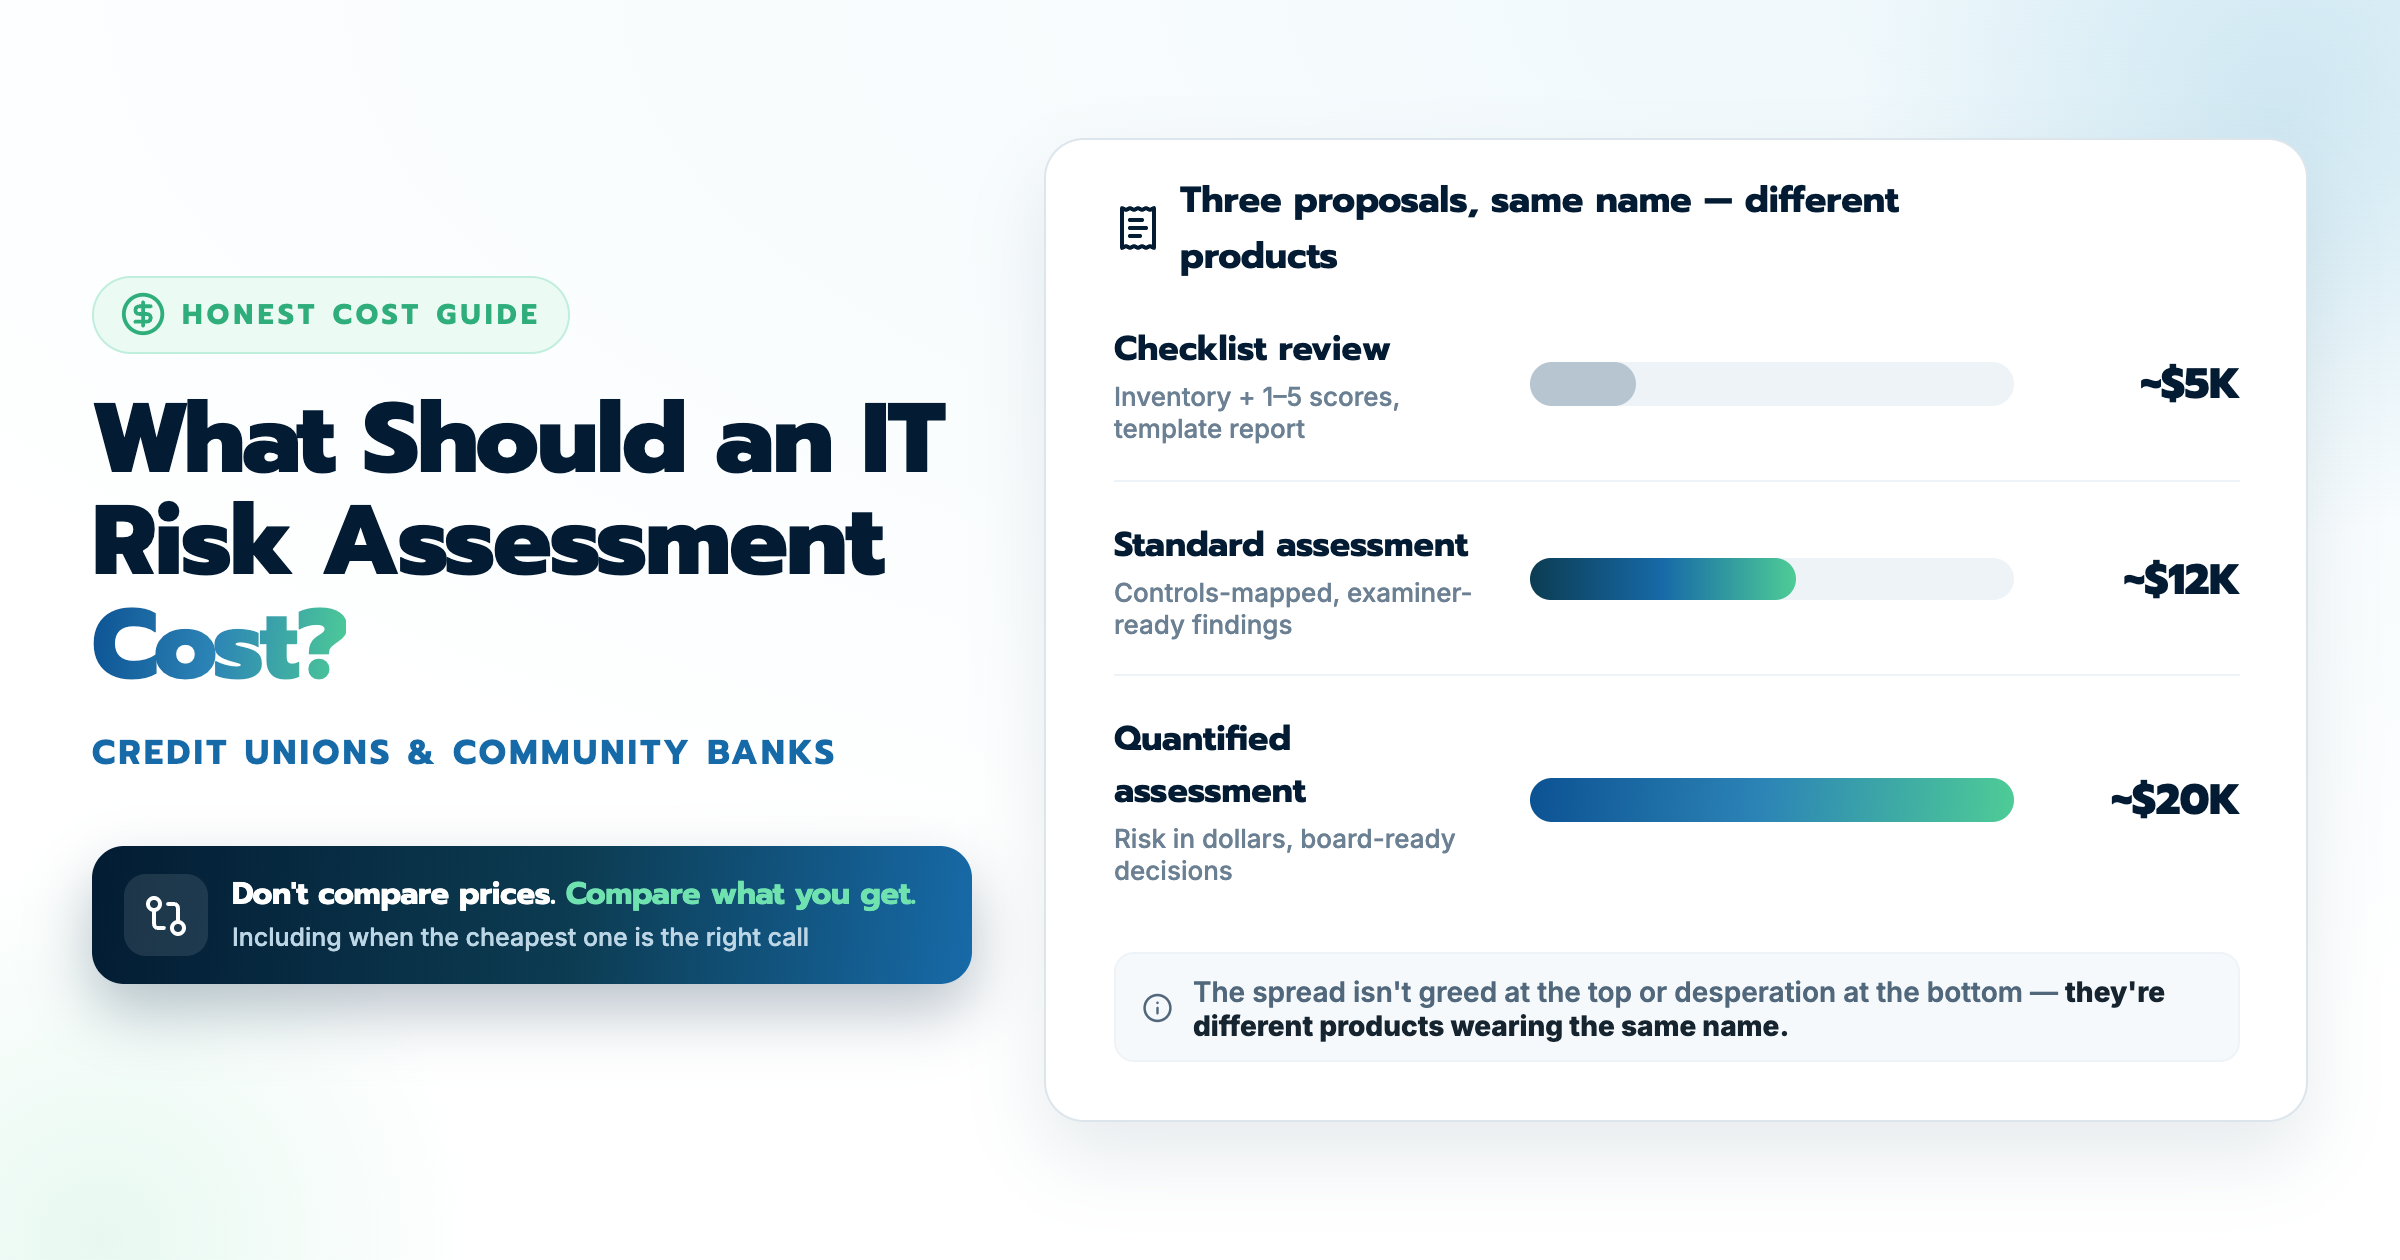
What Should a Credit Union IT Risk Assessment Cost?

You have three proposals on your desk and the numbers are thousands of dollars apart for what each vendor calls the same thing: an IT risk...

Read More

8 min read

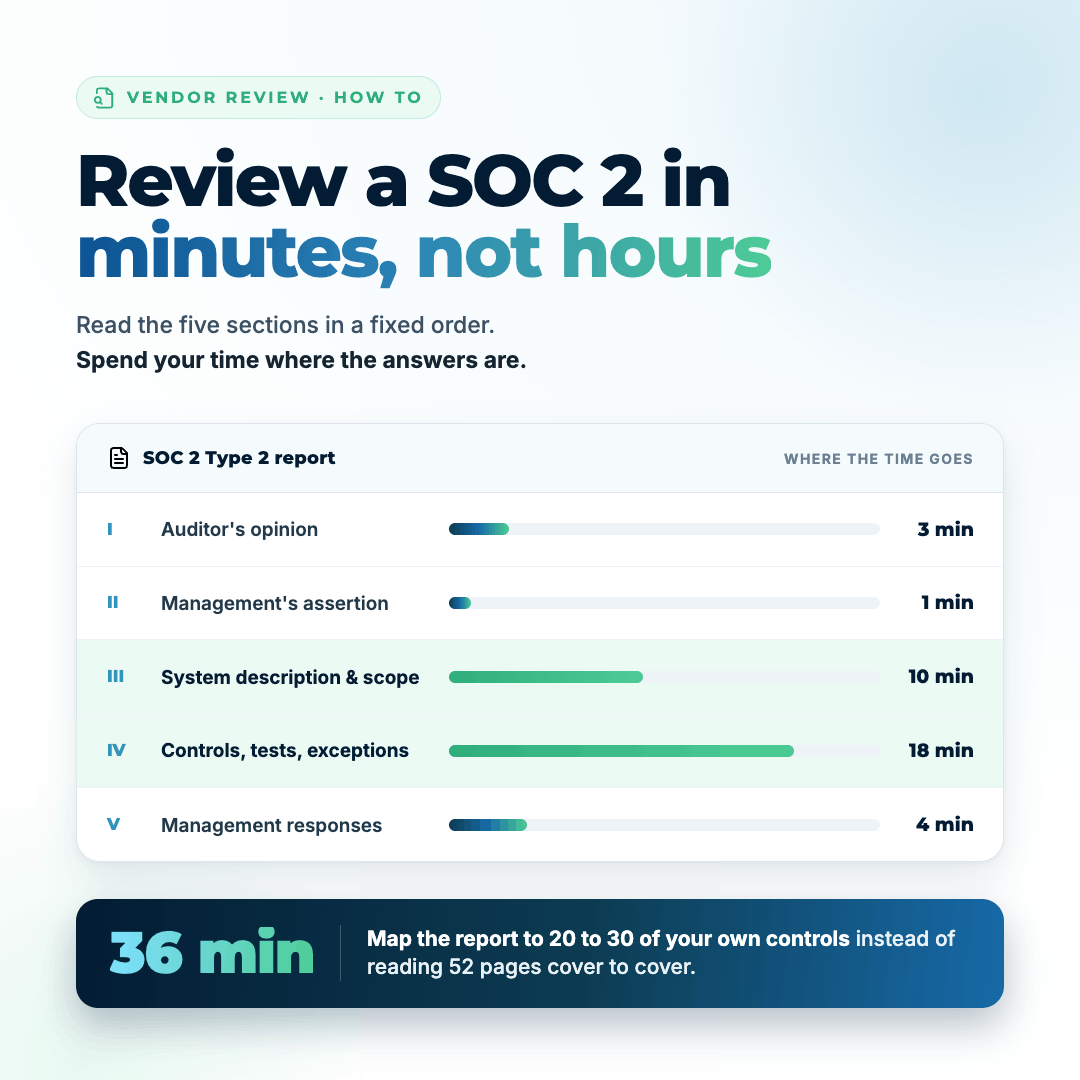
How to Review a SOC 2 Report in Minutes, Not Hours

A security manager at a credit union told us recently that vendor security reviews are the bane of his existence. Another opened a call by saying a...

Read More
Cyber Risk Appetite Statement

8 min read

How to Write a Cyber Risk Appetite Statement

For CISOs, IT risk leaders, compliance officers, and the board committees they report to, a cyber risk appetite statement is the document that...

Read More

8 min read

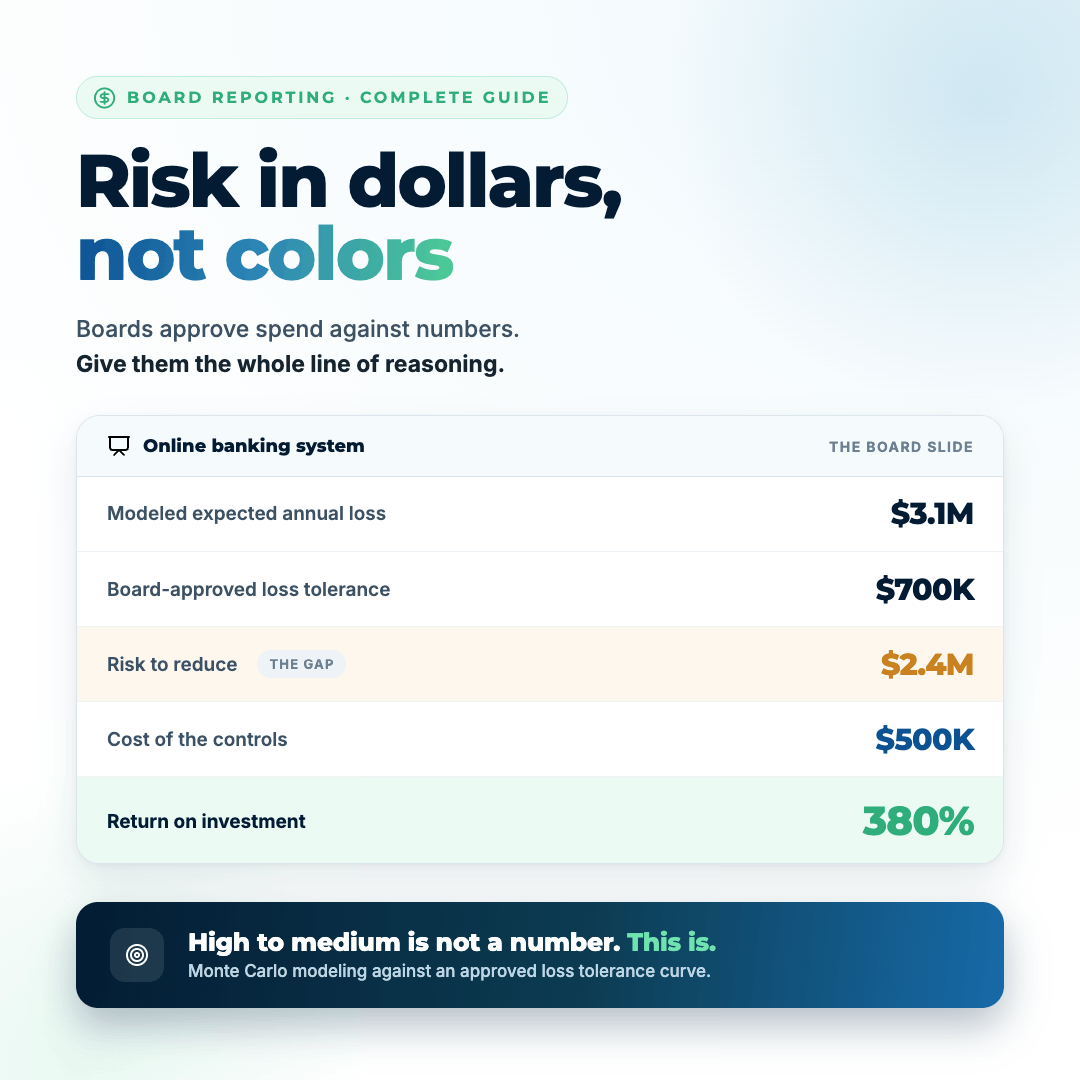
Risk in Dollars, Not Colors: A Complete Guide to Board Reporting

A security officer at a credit union told me that in his entire time at the institution, they had never once talked about risk in numbers. Colors,...

Read More

8 min read

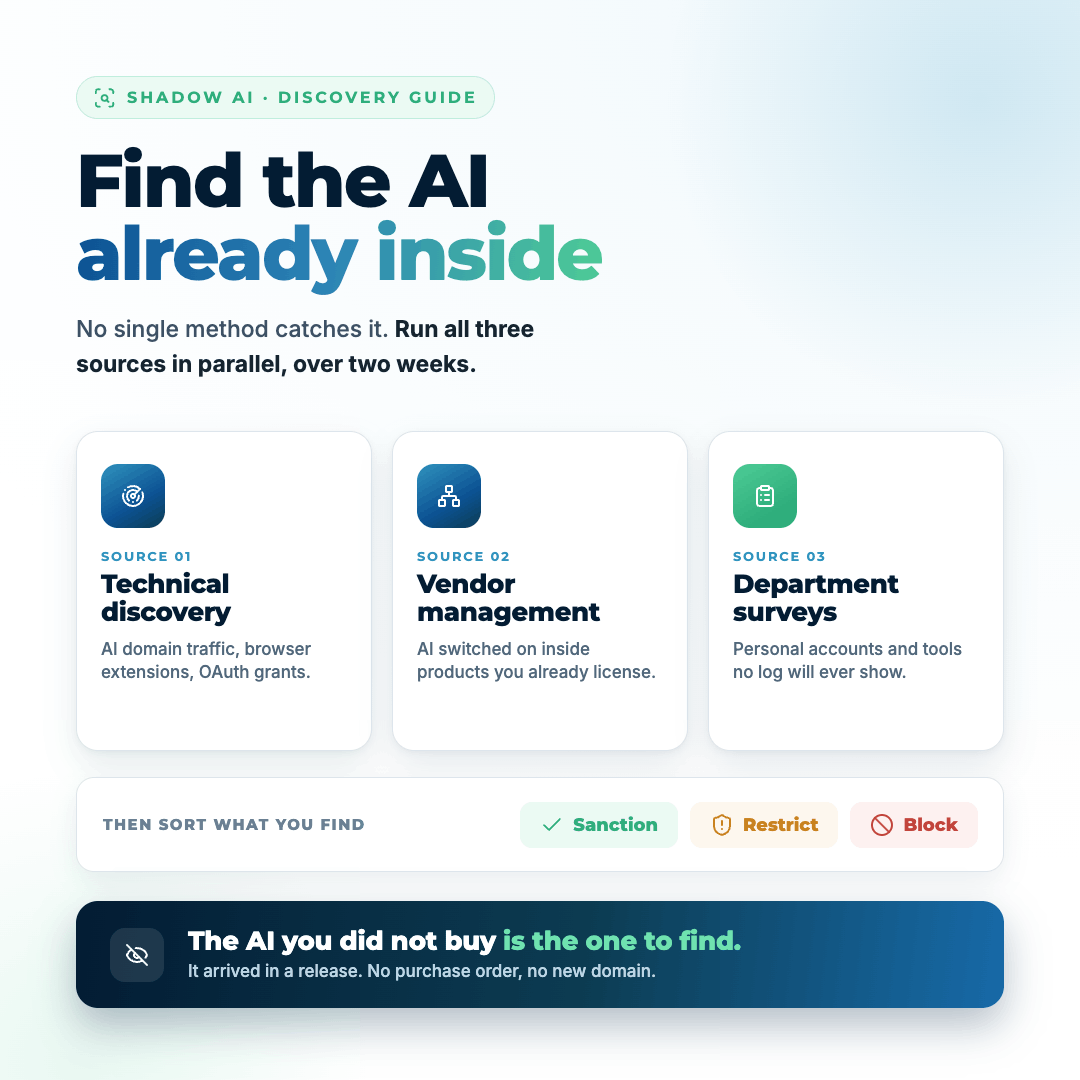
Shadow AI: A Guide to Finding the AI Already Inside Your Institution

A security officer at a credit union described their AI inventory to us like this: they went through the exercise, came out the other side with only...

Read More