Skip to the main content.
Watch Demo Meet With Our Team
Rivial’s Cybersecurity blog

The Savvy CISO

Cybersecurity management insights, tips, and trends for security leaders, CISOs, vCISOs, and MSSPs who want to work smarter, not harder.

5 min read

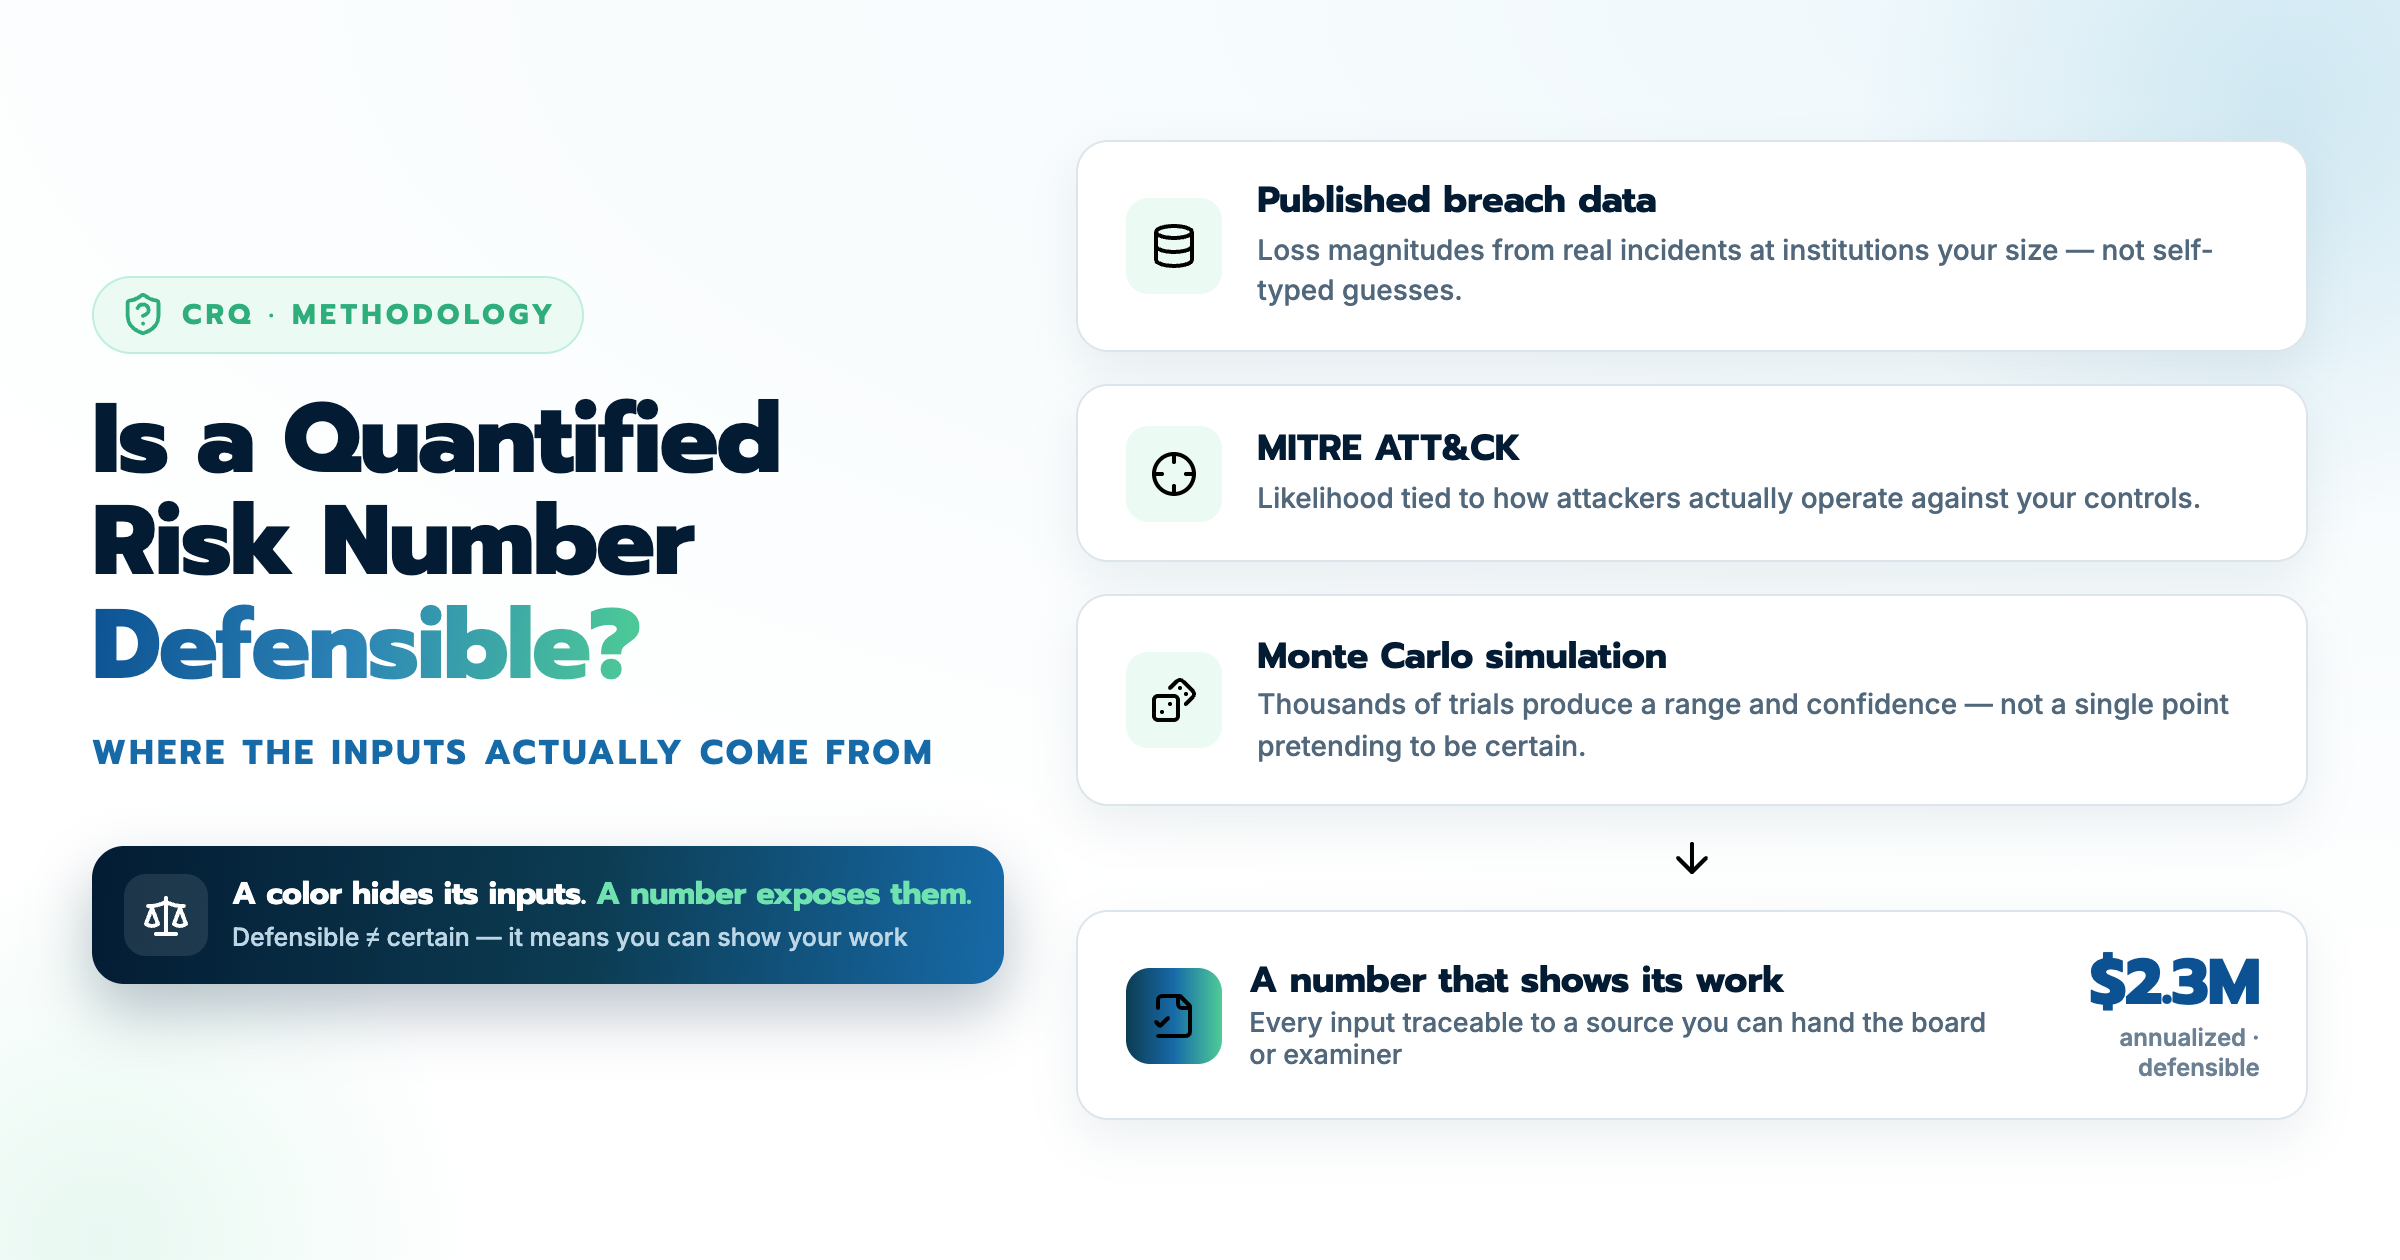
Is a Quantified Cyber Risk Number Defensible? The Inputs

The most common objection to cyber risk quantification does not come from boards. It comes from security leaders, and it goes like this: the number is only as good as the inputs, the inputs are guesses, so the dollar figure is just a guess wearing a...

Read More
4 min read

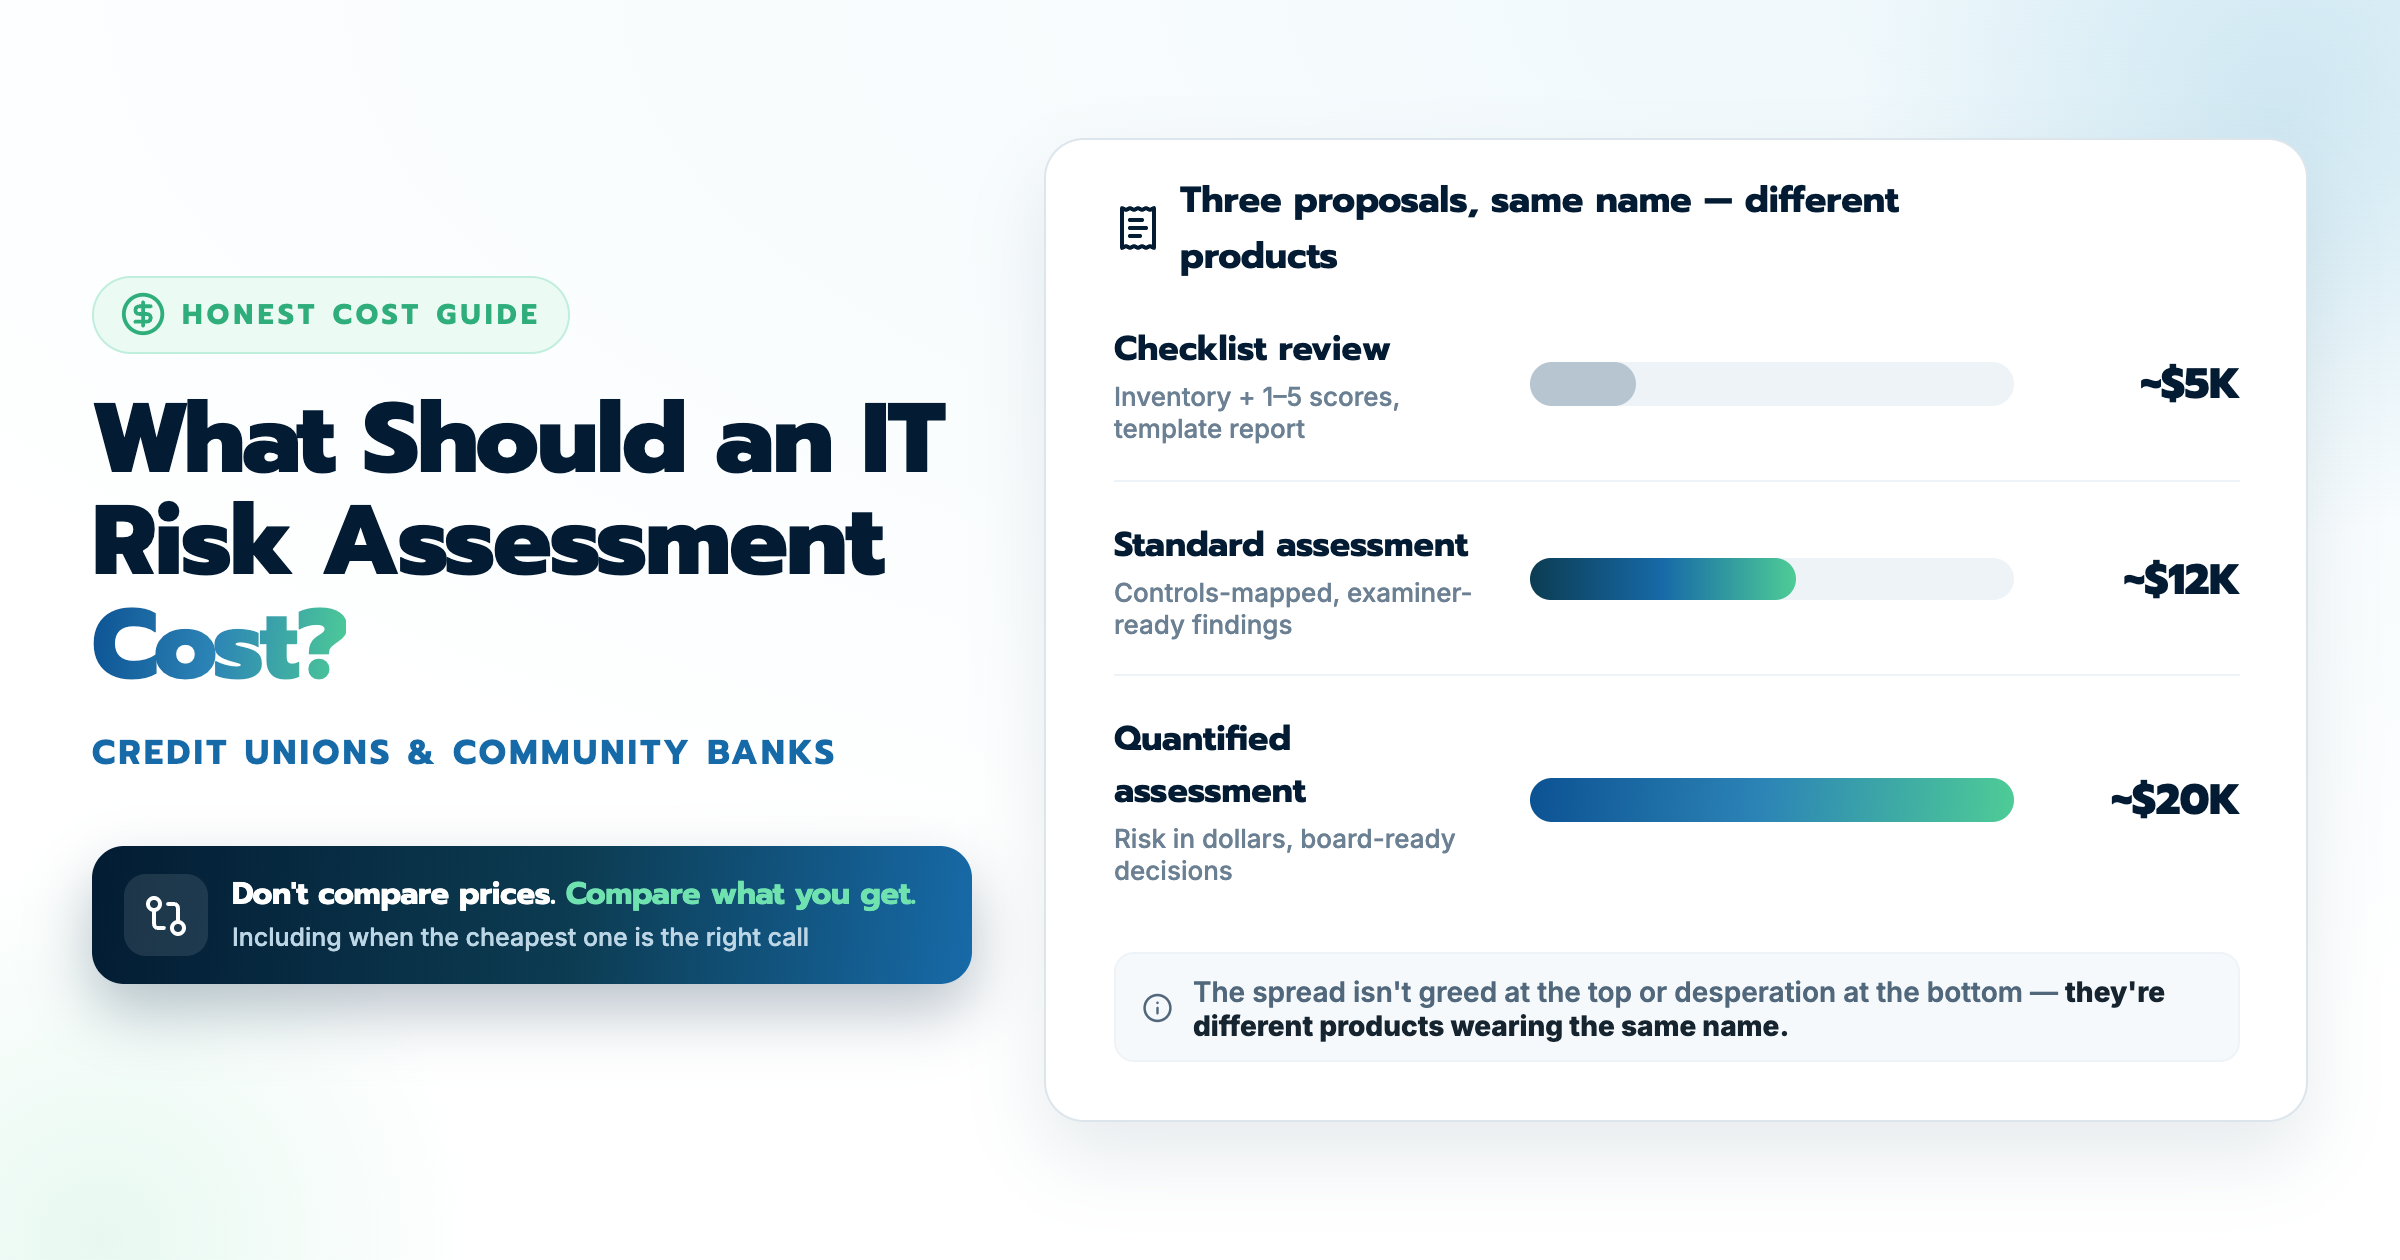
What Should a Credit Union IT Risk Assessment Cost?

You have three proposals on your desk and the numbers are thousands of dollars apart for what each vendor calls the same thing: an IT risk...

Read More

8 min read

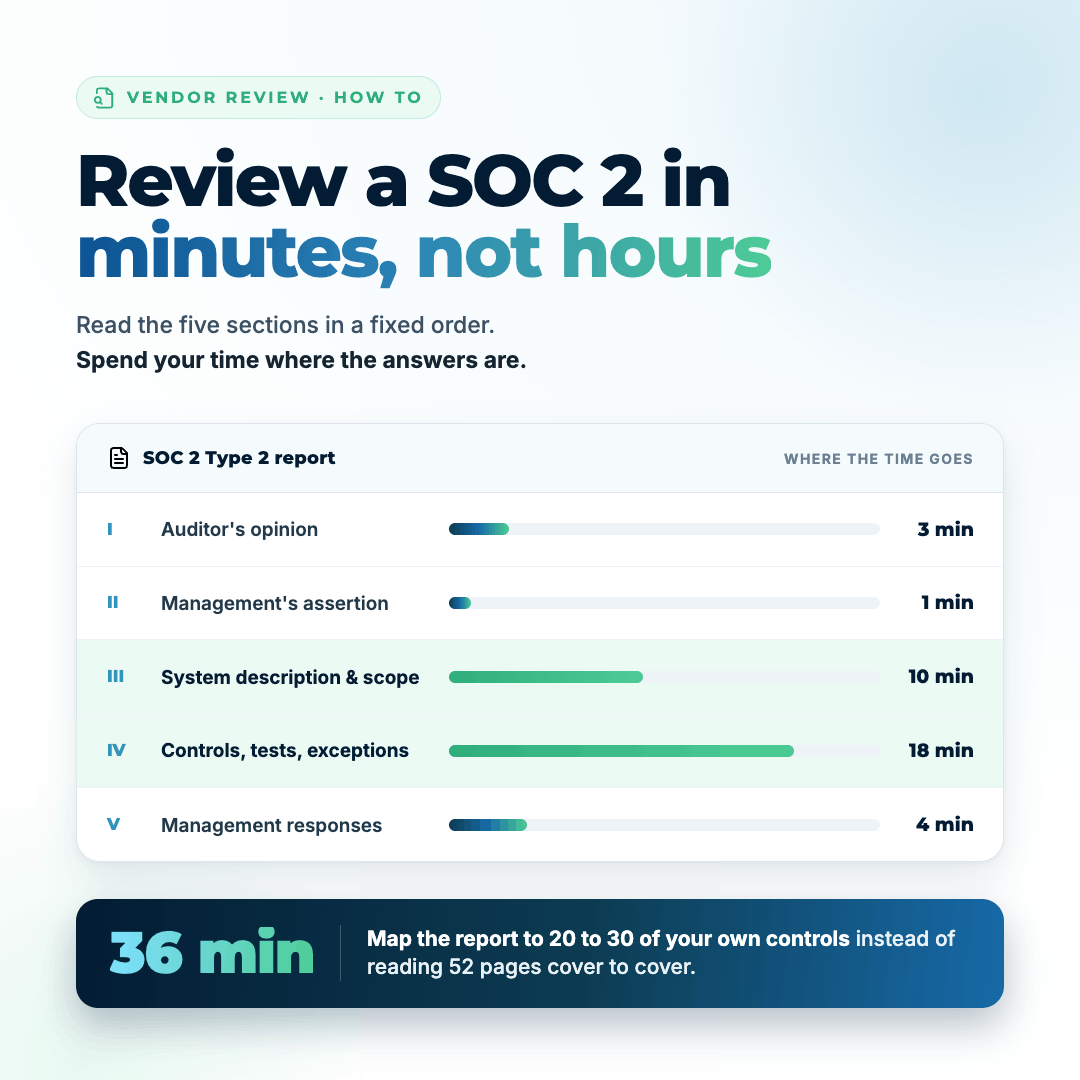
How to Review a SOC 2 Report in Minutes, Not Hours

A security manager at a credit union told us recently that vendor security reviews are the bane of his existence. Another opened a call by saying a...

Read More
Cyber Risk Appetite Statement

8 min read

How to Write a Cyber Risk Appetite Statement

For CISOs, IT risk leaders, compliance officers, and the board committees they report to, a cyber risk appetite statement is the document that...

Read More

8 min read

Risk in Dollars, Not Colors: A Complete Guide to Board Reporting

A security officer at a credit union told me that in his entire time at the institution, they had never once talked about risk in numbers. Colors,...

Read More

8 min read

Shadow AI: A Guide to Finding the AI Already Inside Your Institution

A security officer at a credit union described their AI inventory to us like this: they went through the exercise, came out the other side with only...

Read More

8 min read

Every Vendor Has an AI Feature. Here's How to Assess It

A risk leader at a large financial institution said something on a call this year that we have heard some version of at almost every institution...

Read More
Cybersecurity Risk Register

8 min read

How to Build a Cybersecurity Risk Register

For CISOs, IT risk leaders, compliance officers, and vCISOs, a cybersecurity risk register is the single source of truth that turns scattered...

Read More

5 min read

Quantitative vs Qualitative Cyber Risk Assessment: What Is the Difference?

Quick answer: A qualitative cyber risk assessment rates risk with labels like high, medium, and low, often on a color-coded heat map. A quantitative...

Read More

9 min read

How to Choose the Right vCISO: A Guide for Highly Regulated Organizations

Quick answer: Choose a vCISO who acts as a strategic security leader, not an operator. The right one owns risk, governance, board reporting, and the...

Read More